Arbitrage Opportunities on Polymarket: Finding and Exploiting Price Inefficiencies

Prediction markets have grown fragmented across multiple platforms, each with distinct liquidity pools, user bases, and settlement mechanisms. A binary outcome—whether a political candidate wins, unemployment falls below a threshold, or a company launches a product—may trade at meaningfully different prices on Polymarket, Manifold Markets, PredictIt, and other venues simultaneously. For traders with the tools to detect and execute across these venues, those price gaps represent concrete profit opportunities, provided execution risk, gas costs, and settlement delays do not consume the margin.

The fundamental arbitrage case on Polymarket is straightforward in principle: if a YES share on a political outcome trades at 55 cents on Polymarket but 48 cents on a competing platform, and the trader can simultaneously execute both sides while managing liquidity, time, and regulatory exposure, the difference flows directly to profit. In practice, that execution requires understanding Polymarket’s specific architecture—its use of USDC stablecoin settlement, Polygon Layer-2 infrastructure, Automated Market Maker liquidity dynamics, and UMA oracle resolution. The trader who recognizes price inefficiencies but mishandles settlement timing or underestimates network congestion will find their edge consumed by slippage and delay.

How price discrepancies emerge across prediction markets

Prediction markets are not globally unified. Each platform operates on different blockchains or infrastructure, attracts different participant demographics, and implements different fee structures. Polymarket uses Polygon and charges zero trading fees to users, passing cost recovery to market creators and leveraging the network’s speed and efficiency. Other venues—PredictIt on the Ethereum mainnet with transaction costs, Manifold Markets with its own liquidity mechanics, or offshore platforms like Betfair—each have distinct economic incentives and barriers to entry.

Price discrepancies persist because of market fragmentation and information asymmetry. A sophisticated macroeconomic trader may see a specific outcome as underpriced on Polymarket relative to historical base rates or cross-market pricing, but retail participants on that platform may not have access to the same analysis or competing markets. Conversely, breaking news that affects election odds may move PredictIt faster than Polymarket if news aggregators feed directly into that audience. Liquidity varies by time of day and by market; a YES share may be expensive to acquire in size on a thinly traded Polymarket market but easier to access on Manifold, creating a temporal arbitrage window.

Regulatory uncertainty also drives wedges between markets. Polymarket restricts US retail access through gating mechanisms, whereas PredictIt operates under a specific no-action letter from the CFTC that permits certain US participation. That difference in access creates two separate participant pools with distinct risk tolerances and information sources. A political outcome may be priced more cautiously on Polymarket by international traders concerned about regulatory risk, while US-based participants on PredictIt price the same outcome more aggressively based on their local polling and media environment.

Market maturity also matters. Established markets with high volume and low spreads converge quickly; inefficiencies vanish before a trader can exploit them. Emerging markets, new questions added to a platform, or niche outcomes attract fewer participants and therefore exhibit larger bid-ask spreads and slower price discovery. A market on Polymarket for an obscure regulatory decision may trade at 60 cents on YES, while a more liquid Manifold equivalent for the same outcome has already converged to 52 cents. The trader who recognizes that discrepancy has a narrow window before others notice and trade it away.

Identifying inefficiencies: Tools and data sources

Manual price checking across platforms is slow and error-prone. The trader who opens Polymarket, navigates to a market, then manually switches to PredictIt and Manifold Markets by the time prices have already moved. Systematic arbitrage requires automated or semi-automated price monitoring. Several approaches exist, with varying levels of sophistication and legal clarity.

The simplest method is a spreadsheet or lightweight monitoring script that periodically samples prices from public APIs and exchanges. Polymarket’s subgraph, maintained on The Graph, exposes real-time market data including prices, volumes, and liquidity positions. Other platforms publish APIs or maintain accessible data endpoints. A trader can write a basic script that logs prices at fixed intervals, calculates percentage differences, and alerts when the spread exceeds a predefined threshold. That approach captures only static snapshots and misses the exact timing of price changes; it is sufficient for monitoring illiquid markets but inadequate for fast-moving outcomes.

More sophisticated systems use WebSocket connections to monitor price feeds in real time, calculate implied probabilities across markets, and generate actionable signals the moment a discrepancy appears. Some traders implement order flow aggregators that track bids and asks as they arrive, enabling them to front-run the convergence they anticipate. The legal status of such systems is ambiguous in traditional finance; in prediction markets, which are less regulated and have fewer institutional guardrails, the barriers are lower but not nonexistent.

Data quality is a practical constraint. Platform APIs can be inconsistent, downtime is common, and historical data is often incomplete. A trader relying on a single price feed for a critical decision may find that the feed lag caused them to miss the execution window or, worse, to act on stale information. Cross-referencing multiple sources—published order books, blockchain transaction data, and direct API calls—reduces that risk but also increases complexity and cost.

Execution risk and the costs of speed

Identifying a 7-cent discrepancy on a YES share is only step one. Executing the arbitrage before prices converge is step two, and it is where most theoretical profits evaporate. On Polymarket, a trader must deposit USDC into the platform, identify the market, place a buy order at current liquidity conditions, wait for confirmation, and then simultaneously execute the offsetting sale on a competing platform. Each step introduces latency, cost, and execution uncertainty.

Polygon’s speed advantage is meaningful but not infinite. A transaction to Polymarket typically confirms in seconds, but slippage can reduce the effective fill price compared to the quoted rate. The Automated Market Maker on Polymarket uses a Constant Product formula; large orders move the price against the trader, sometimes by more than the original arbitrage spread. A trader attempting to buy $10,000 of YES shares at a seemingly attractive price may encounter slippage of 200–300 basis points due to limited liquidity, reversing the profit into a loss.

Competing platform execution introduces further complications. If Polymarket settles quickly but PredictIt has network congestion, the trader may find themselves holding an unhedged YES position on Polymarket while the offsetting short sale on PredictIt sits pending. If prices move sharply in the interim—perhaps new polling data releases—that unhedged window can turn a small arbitrage into a large directional bet.

Gas costs on Layer-2 networks like Polygon are negligible compared to Ethereum mainnet, but they are not zero. A trader executing frequent small arbitrage trades across many markets may face $50 to $200 per week in aggregate network costs. That overhead is tolerable if each arbitrage captures 200 basis points, but it destroys economics if inefficiencies average only 50 basis points. The trader must therefore be selective, targeting only markets where the spread is large enough to survive slippage, network costs, and the time value of capital.

Settlement and resolution risk in arbitrage positions

Prediction market arbitrage differs from equity or derivatives arbitrage in one critical respect: the underlying “assets” settle on real-world outcomes with delays and dispute mechanisms. On Polymarket, outcomes are resolved by UMA oracles, which aggregate data from decentralized sources and allow community challenges. That mechanism is robust against single points of failure, but it introduces uncertainty about timing and finality.

A trader executing an arbitrage on election night may lock in a small spread by going long YES on Polymarket and short YES (or long NO) on Manifold, believing the outcome is certain. But election outcomes are sometimes disputed, and regulatory clarity may be unclear; disputes can extend settlement by days or weeks. During that period, the trader’s capital is locked, unable to redeploy to other arbitrages. The effective return on an annualized basis may be poor if the capital is trapped for 30 days waiting for an oracle resolution that should have been obvious in 24 hours.

UMA’s dispute mechanism also creates tail risk. In most cases, the oracle resolves correctly, and both platforms settle to the same outcome. But if a market on Polymarket resolves YES and a competing platform resolves NO—perhaps due to different data inputs or interpretation—the trader’s arbitrage collapses. Both sides of the position cannot be unwound simultaneously if the platforms disagree on the outcome. That scenario is rare, but it is not zero probability, and it represents a potential loss that can exceed the captured arbitrage profit.

Geographic and regulatory complications add another layer. Some traders participate across international prediction markets, UK betting exchanges, and decentralized platforms. Settlement rules, tax treatment, and regulatory approval vary. A trader who successfully arbitrages across three venues but faces unexpected tax liability or regulatory action in one jurisdiction may find the net profit entirely eliminated. Due diligence on jurisdiction-specific rules is therefore as important as price monitoring.

Capital efficiency and bankroll management

Arbitrage capital is locked in two places simultaneously: on Polymarket and on a competing platform. If a trader has $100,000 and identifies a 50-basis-point arbitrage opportunity, executing that opportunity fully consumes the entire bankroll, earning perhaps $500 to $1,000 after costs while tying up all capital. If the trader identifies multiple opportunities on the same day—a reasonable scenario across dozens of active markets—they face a choice: execute only the best opportunity and leave capital idle, or split capital and dilute the return on each position.

Working with leverage or external capital can multiply returns, but it also introduces counterparty risk and fees. Some traders borrow USDC at a fixed rate to increase arbitrage capital, accepting the cost as part of their cost basis. Others solicit limited partners to co-invest, sharing returns in exchange for deployed capital. Both approaches magnify small-percentage arbitrage opportunities into meaningful absolute returns, but they also magnify losses if execution goes wrong or if capital is locked longer than expected.

The practical implication is that successful prediction market arbitrage requires scale and patience. A small-scale trader executing one or two arbitrages per week may earn $100 to $500 per trade, insufficient to justify operational overhead and opportunity cost. A systematic trader who can execute 10 to 20 arbitrages per week across multiple markets, managing capital efficiently and reinvesting profits, can build a sustainable business. The mathematical edge is small—often 20 to 100 basis points per trade—but compounding and scale make it economically viable.

Regulatory and platform-specific constraints

Prediction market arbitrage operates in a legal gray zone that is shifting rapidly. The CFTC has not clearly stated whether frequent trading on prediction markets constitutes futures trading subject to exchange registration, and the regulatory treatment of decentralized platforms like Polymarket remains unsettled. In the US, Polymarket restricts retail account access; operating from a US residential address while arbitraging cross-platform may violate the platform’s terms or expose the trader to regulatory risk.

International traders face jurisdiction-specific rules. UK traders may be subject to Gambling Commission oversight, while EU traders must navigate MiFID II and national derivatives regulations. Some traders operate from jurisdictions with minimal regulation—Singapore, Cayman Islands, or the UAE—to reduce regulatory friction. That approach trades lower regulatory burden for reduced access to traditional financial infrastructure and less recourse if a dispute arises.

Platform-specific constraints also limit arbitrage strategies. Some platforms implement position limits to prevent market manipulation; a trader who attempts to buy too many YES shares on a single market may face reduced liquidity or temporary restrictions. Some platforms require minimum holding periods before withdrawal, effectively locking arbitrage proceeds. Polymarket’s terms explicitly restrict certain forms of account activity; high-frequency trading or suspected arbitrage bots may trigger account review or suspension. A trader should thoroughly review each platform’s terms of service and contact support before deploying large capital.

Building a systematic approach to prediction market arbitrage

Successful arbitrage is not a single trade; it is a system of monitoring, filtering, execution, and risk management. A trader building a systematic approach should start with the following framework. First, establish a price monitoring system that samples multiple platforms at regular intervals and calculates spreads automatically. Second, set minimum spread thresholds—only signal trades if the opportunity exceeds a profitable hurdle rate after fees, slippage, and settlement delays. Third, pre-position capital on each platform in sizes appropriate to historical arbitrage volumes, reducing the need to deposit or withdraw during execution windows.

Fourth, implement position-level risk controls. Do not arbitrage more capital than necessary in single trades; keep positions small enough that market impact is negligible and execution risk is manageable. Fifth, maintain detailed records of every executed arbitrage, including the prices at entry and exit, settlement outcomes, and actual realized profit or loss. Over time, that data reveals which market pairs are most reliable, which platforms have consistent slippage, and which spreads are most likely to close before execution.

Sixth, periodically backtest trading rules on historical data to verify that signaling logic actually captures value. A system that looks good in real time may simply be chasing noise if the spreads were never real or closed too quickly to execute profitably. Seventh, expect and plan for occasional losses. Execution errors, market impact, or unexpected price moves will sometimes result in negative trades. The goal is to ensure that winning trades outnumber and outsize losing trades by a sufficient margin to generate positive expected value over a large sample.

Finally, recognize that prediction market arbitrage is a commodity strategy. As more traders automate detection and execution, spreads compress, and returns diminish. A trader who discovers an arbitrage opportunity today may find that opportunity has been closed by competing automated systems within hours or days. Staying ahead requires continuous system refinement, faster execution infrastructure, or moving into less crowded market niches where competition is lighter. The most durable edge comes from identifying inefficiencies that others miss—markets with limited participation, outcomes that span multiple platforms but attract different trader demographics, or settlement mechanics that create persistent timing gaps.

Frequently asked questions

What is the typical size of arbitrage opportunities on Polymarket?

Price discrepancies vary widely by market liquidity and platform fragmentation. Highly liquid markets on Polymarket with deep volume on competing platforms may exhibit spreads of 10 to 50 basis points; illiquid or niche markets can show spreads of 100 to 300 basis points or more. After accounting for slippage, network costs, and execution delays, profitable opportunities typically require spreads of at least 75 to 150 basis points to deliver positive expected return.

How does Polygon’s low-cost infrastructure affect arbitrage strategy on Polymarket?

Polygon’s Layer-2 scaling reduces gas costs from hundreds of dollars per transaction to cents, enabling frequent trading and small-spread arbitrage that would be economically infeasible on Ethereum mainnet. This makes Polymarket attractive for high-frequency arbitrage strategies, but it also means that competing arbitrageurs can execute quickly, causing spreads to compress faster than on more expensive networks.

What happens if different platforms resolve a market to different outcomes?

Resolution discrepancies are rare but possible if platforms use different data sources or UMA oracle interpretations. If Polymarket resolves a market to YES while a competing platform resolves to NO, an arbitrage position spanning both platforms will realize a loss on one side that cannot be offset by a gain on the other. The trader is exposed to basis risk—the risk that the two sides of a supposedly hedged trade diverge due to different settlement rules or oracle behavior.
Urgent Hiring

🔔 URGENT HIRING – MULTIPLE POSITIONS | KSA & QATAR

Mancon International PVT Ltd. is pleased to announce immediate openings for experienced professionals with a leading employer in KSA and Qatar. Candidates with strong backgrounds in construction, steel fabrication, interior design, e-commerce, and sales are encouraged to apply.
📌 CURRENT VACANCIES – DETAILED REQUIREMENTS

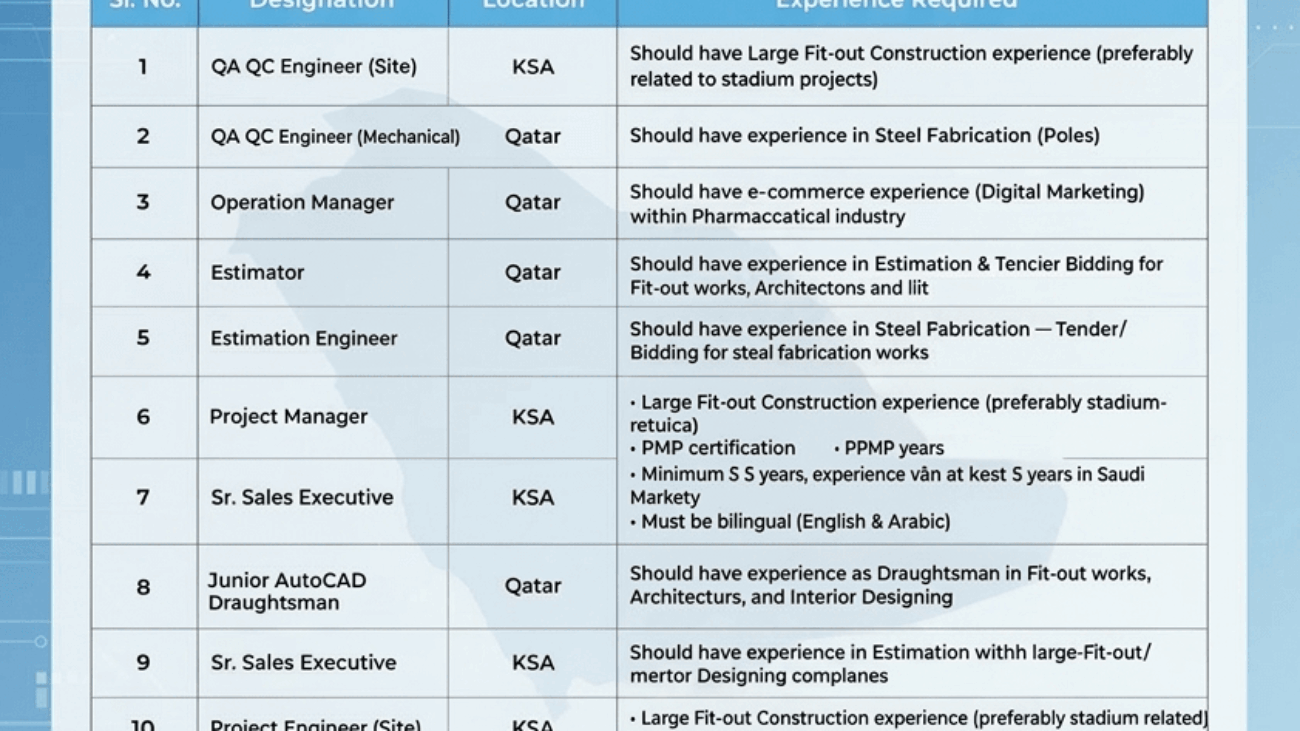
1 QA QC Engineer (Site) KSA Should have large Fit-out Construction experience (preferably related to stadium projects)
2 QA QC Engineer (Mechanical) Qatar Should have experience in Steel Fabrication (Poles)
3 Operation Manager Qatar Should have e-commerce experience (Digital Marketing) within the Pharmaceutical industry
4 Estimator Qatar Should have experience in Estimation & Tender Bidding for Fit-out works, Architecture, and Interior Designing
5 Estimation Engineer Qatar Should have experience in Steel Fabrication – Tender/Bidding for steel fabrication works
6 Project Manager KSA • Large Fit-out Construction experience (preferably stadium-related)
• PMP certification mandatory
• Minimum 15 years of experience as Project Manager
• Must be bilingual (English & Arabic)
7 Junior AutoCAD Draughtsman Qatar Should have experience as Draughtsman in Fit-out works, Architecture, and Interior Designing
8 Sr. Sales Executive KSA • Experience as Sales Executive within large Fit-out/Interior Designing companies
• Minimum 5–7 years’ experience (with at least 5 years in Saudi Market)
• Must be bilingual (English & Arabic)
9 Sales Manager KSA • Experience as Sales Manager within large Fit-out/Interior Designing companies
• Minimum 10 years’ experience (with at least 5 years in Saudi Market)
• Must be bilingual (English & Arabic)
10 Project Engineer (Site) KSA • Large Fit-out Construction experience (preferably stadium-related)
• Minimum 10 years of experience in Project Planning
• Must be bilingual (English & Arabic)
✨ GENERAL BENEFITS (Varies by Position)
Competitive tax-free salary
Food, accommodation, and transport as per company policy
Overtime eligible (subject to site requirements)
Annual leave and air ticket as per the labor law
Full visa sponsorship
📩 HOW TO APPLY
📧 Email: careers@manconint.com
📱 Phone / WhatsApp: +92 321-472-9065
🌐 Website: www.manconint.com

Subject Line: Application for [Position Title] – [KSA/Qatar]

Diagram showing the relationship between Uniswap liquidity pools, price feeds, and dependent DeFi protocols with attack vectors illustrated

Uniswap Price Oracle: How DeFi Protocols Use Uniswap Data for On-Chain Pricing

A lending protocol needs to determine the collateral value of a user’s token holdings in real time. A derivatives platform must price assets for liquidation triggers. An algorithmic stablecoin requires continuous market rates to maintain its peg. Each of these scenarios depends on reliable on-chain price data, yet no single trusted oracle exists inside the blockchain itself. The solution that has emerged across DeFi is to extract pricing information directly from decentralized exchange pools—most prominently from Uniswap, which has become the de facto price oracle for hundreds of protocols despite never being designed primarily for that purpose.

This use case reveals a fundamental tension in decentralized finance. Uniswap’s automated market maker model creates liquidity that enables transparent, continuous pricing based on actual trades. However, that same transparency creates opportunities for manipulation. When a smart contract reads prices from a single Uniswap pool to execute a transaction in the same block, an attacker with sufficient capital can artificially move prices and extract value. Understanding how protocols safely use Uniswap as a price feed requires examining the technical mechanisms, the real-world risks, and the architectural patterns that have evolved to mitigate them.

Diagram showing the relationship between Uniswap liquidity pools, price feeds, and dependent DeFi protocols with attack vectors illustrated

Why Uniswap became the protocol’s de facto price oracle

Before decentralized exchanges reached significant scale, on-chain pricing was either absent or centralized. Early DeFi protocols relied on signed price updates from off-chain sources, creating dependencies on trusted entities. The emergence of Uniswap with its deep liquidity pools and constant product formula changed the equation. Because Uniswap processes hundreds of millions in daily volume across multiple token pairs, the pools reflect real market demand and supply. Any protocol that could directly query the exchange rates embedded in those pools would have access to a price signal derived from actual transactions rather than external attestation.

The appeal is straightforward: no oracle operator, no signed messages, no time delay between market movement and contract execution. The price is simply the ratio of token balances in a liquidity pool at the moment the smart contract reads it. For many early protocols, this appeared to be a perfect solution. A lending protocol could check the price of collateral directly from Uniswap before accepting a deposit or triggering liquidation. An automated market maker could verify prices across Uniswap pools to arbitrage inefficiencies. The promise was seamless, trustless pricing—and it worked until it did not.

The critical limitation is that instantaneous prices in Uniswap are not guaranteed to reflect fair market rates. A pool shows the exchange rate for the next trade, not the consensus price across all markets. More importantly, that price can be moved within a single transaction block by someone with enough capital and control. When a protocol naively reads a price from Uniswap and executes a trade or loan agreement based on that instant reading, it becomes vulnerable to a specific class of attack that has cost tens of millions in losses across DeFi history.

Despite these challenges, Uniswap remains the most widely used on-chain price source. Its size, diversity of trading pairs, and open architecture make it more resilient than smaller alternatives. Protocols have learned to use Uniswap more carefully—checking multiple pools, averaging prices over time, and comparing results to alternative sources—but the fundamental pattern persists. Understanding how to use Uniswap safely requires understanding how it can be attacked.

The constant product formula and how prices emerge

Uniswap’s core mechanism is mathematically simple: the product of the two token balances in a pool must remain constant. If a pool contains 1,000 units of token A and 100 units of token B, the invariant is 1,000 × 100 = 100,000. When a trader buys token B by selling token A, the new balance might be 1,100 token A and 90.9 token B, preserving the product (1,100 × 90.9 ≈ 100,000). The exchange rate emerges from this adjustment: the trader received 9.1 tokens at a cost of 100 tokens, establishing a temporary price.

This formula creates a property that makes Uniswap suitable for on-chain pricing: prices are discoverable without external input. No order book is needed, no market maker sets prices, and no off-chain computation is required. The rate at which tokens exchange is determined solely by the ratio of reserves in the pool. A smart contract can query the balances of a Uniswap v2 or v3 pool, apply the constant product formula, and calculate the price of any swap. This is what makes Uniswap a price oracle in practice—it is a source of verifiable, on-chain exchange rates.

However, this same mechanism creates vulnerability. Because prices are tied directly to the pool balances, anyone who changes the balances also changes the prices. A large trade executed before another transaction in the same block will alter the price that subsequent transactions see. This is not accidental behavior; it is inherent to how the system works. The attacker does not need to corrupt Uniswap or compromise any oracle infrastructure. They simply need to front-run a transaction or manipulate the pool in the same block.

The mathematical elegance of constant product pricing therefore contains a hidden cost: users of Uniswap as a price oracle must account for the possibility that the price they read in block N may have been artificially shifted by transactions earlier in the same block. Unlike a traditional oracle that aggregates data from multiple independent sources and signs a commitment to a price, Uniswap offers only the instantaneous ratio at a specific moment.

Flash loan attacks and sandwich attacks on protocols using Uniswap pricing

A flash loan is a special type of transaction in DeFi that allows a smart contract to borrow a large amount of capital, execute any code, and repay the loan—all within a single transaction block. If the loan is not repaid by the end of the block, the entire transaction reverts. Flash loans are useful for legitimate purposes like arbitrage and liquidation, but they enable a specific attack vector: borrow millions, use that capital to manipulate a Uniswap pool, and execute a trade or loan agreement against the artificially inflated price, all before the loan must be repaid.

An attacker could use a flash loan to buy a large amount of token A on Uniswap, shifting the price dramatically. If a lending protocol naively reads the new price and allows the attacker to borrow token B against overvalued collateral, the attacker can then repay the flash loan and keep the profit. The protocol suffers a loss because it allowed a loan at an artificially favorable rate. This is not a flaw in the flash loan mechanism itself; it is a consequence of building price logic that trusts an instantaneous Uniswap reading without safeguards.

Sandwich attacks follow a similar pattern but without flash loans. An attacker observes a pending transaction that will execute a large trade through Uniswap. The attacker places their own transaction before it (front-running) to move the price, executes the victim’s transaction at a worse rate, and then reverses their position (back-running) to profit from the movement. If a downstream protocol read the price at the moment the victim’s transaction executed, the protocol would see the artificially moved price and might make decisions based on false data.

The most famous example involved bZx in 2020, where attackers used flash loans to manipulate prices on Uniswap and other exchanges, causing a lending protocol to liquidate positions at manipulated rates. The loss exceeded $600,000 and highlighted a critical lesson: using Uniswap as a price oracle requires defenses against these attack patterns. Simply querying the current reserve ratio is insufficient.

Time-weighted average prices and safer oracle design

The most widely adopted defense is the time-weighted average price (TWAP), which Uniswap natively supports through its TWAP oracle mechanism. Instead of reading the instantaneous price, a protocol queries the average price over a fixed historical window—such as the last hour or the last 1,000 blocks. An attacker can still move prices in the current block, but they cannot retroactively change the average of prices from past blocks that have already been finalized. This makes TWAP manipulation far more expensive and difficult.

Uniswap v2 provides a simple TWAP mechanism through accumulated price observations stored on the blockchain. A smart contract can read the current cumulative price counter and compare it to a value from a previous block, computing the average. While this requires either storing previous prices off-chain or maintaining state across multiple blocks, it remains fully on-chain and decentralized. The v3 version offers more sophisticated oracle infrastructure with better precision and flexibility.

However, TWAP is not risk-free. An attacker with sustained capital over a longer period can gradually move prices and influence the average. The defense works best when the observation window is long relative to the attacker’s resources and when the pool has high liquidity that absorbs price movements. A small, low-liquidity pool is more vulnerable to sustained manipulation than a large, heavily traded pool. This is why protocols using Uniswap for pricing typically prioritize large pools with stable, deep liquidity.

An alternative or complementary approach is to use multiple independent price sources and aggregate them. A protocol might compare Uniswap’s TWAP to prices from Balancer, Curve, or other decentralized exchanges. If prices diverge significantly, the protocol can revert the transaction or use a fallback mechanism. This reduces the impact of a successful attack on any single exchange, though it increases computational cost and complexity.

How DeFi protocols implement Uniswap data safely

Modern protocols using Uniswap as a price feed have converged on specific architectural patterns. The first is to query TWAP prices rather than spot prices, using Uniswap’s historical price data with a sufficient lookback window to resist short-term manipulation. The second is to implement slippage checks and require users to specify maximum acceptable price impact when executing trades. A user might accept a trade at the current spot price, but if the actual execution price is more than 1 percent worse than expected, the transaction reverts. This forces attackers to manipulate prices more dramatically and visibly.

The third pattern is to avoid making critical decisions based solely on Uniswap prices. A lending protocol might use Uniswap as one input to collateral valuation but compare it to prices from other sources or to historical ranges. If Uniswap shows a price that is far outside recent norms, the protocol might use a capped or conservative value instead. This reduces the reward for price manipulation and forces attackers to accept lower profits.

A fourth layer of defense is rate limiting or circuit breakers. Some protocols restrict the amount of collateral a user can pledge or the size of a liquidation in a single transaction. This reduces the potential damage if a price manipulation attack succeeds, spreading the risk over multiple transactions and time periods. An attacker must choose between accepting a smaller total profit or spreading their attack across multiple blocks and facing the likelihood that other protocols or traders will arbitrage the prices back to fair levels.

The most sophisticated protocols also implement oracle governance, where the protocol can change its price sources or adjust parameters if an attack is detected. Some use decentralized identifier systems or committee mechanisms to control which price feeds are trusted. This is more complex than pure on-chain logic but provides additional resilience when circumstances warrant it.

When Uniswap pricing is and is not appropriate

Using Uniswap as a price oracle is appropriate for many use cases but dangerous for others. For swap execution, where a user explicitly sends a transaction to exchange tokens and accepts some slippage, Uniswap pricing is inherent to the operation. The user is agreeing to the terms that the protocol executes. Slippage settings protect against unexpected price movement.

For lending protocols and collateral valuation, the decision is more nuanced. A lending platform accepting a widely traded token like ETH or USDC as collateral can safely use Uniswap pricing with TWAP and multiple source comparison, because the liquidity is deep and the token trades on dozens of other exchanges. Manipulation becomes expensive and difficult when the token is liquid everywhere. However, a lending platform accepting a newly launched or low-liquidity token is taking on substantial risk. An attacker with moderate capital could dominate the pool and set prices, especially if the token does not trade on alternative exchanges.

Derivatives platforms and algorithmic stablecoins face particular challenges. These protocols often require precision and real-time accuracy that a TWAP oracle cannot guarantee. A liquidation delay of even one block can allow losses to compound. An algorithmic stablecoin that reads prices from Uniswap and adjusts supply based on those prices is essentially betting that the Uniswap prices are safe from manipulation. History suggests this is a risky bet. These applications might use Uniswap as a confirmation or sanity check but typically rely on additional infrastructure like a uniswap governance-backed oracle or off-chain attested prices.

The general rule is that the more critical the decision is to the protocol’s financial safety, the more defensive the oracle design should be. Casual pricing for statistical or UI purposes can use instant spot prices. Execution of trades can use slippage checks. Collateral valuation should use TWAP with backup sources. Liquidation triggers should use aggregated prices with governance oversight.

The evolution of Uniswap’s oracle capabilities across versions

Uniswap v1 and v2 provided basic oracle support through cumulative price tracking, but the infrastructure was minimal. Developers had to implement TWAP logic themselves and manage historical checkpoints. This worked but was not seamless and required careful engineering to avoid mistakes.

Uniswap v3 introduced a significant improvement with integrated oracle functionality. The v3 pools track not just cumulative prices but also cardinality—the number of observations stored—and allow arbitrary lookback windows. A protocol can query the average price over the last 3,600 blocks (roughly 14 hours on Ethereum) without external reference points. The oracle also supports multiple fee tiers, so a protocol can measure prices across the 0.01%, 0.05%, 0.30%, and 1% fee pools simultaneously, reducing reliance on a single tier.

This architectural evolution reflects Uniswap’s increasing role as DeFi infrastructure. The developers recognized that protocols needed better oracle support and built it directly into the protocol. However, the responsibility for safe usage remains on the protocol developer. A v3 oracle is a more powerful tool, but it still requires judgment about observation windows, fee tier selection, and fallback mechanisms.

Going forward, the question is whether Uniswap will remain the dominant on-chain price source or whether specialized oracle protocols will capture more share. Protocols like Pyth Network and Chainlink aggregate prices from multiple sources off-chain and report them on-chain, trading decentralization for resilience and precision. Uniswap’s advantage is that its prices are fully on-chain and require no external trust. Its disadvantage is that safety still depends on the protocol that consumes the data.

Real-world lessons from oracle attacks in DeFi history

The bZx attack in 2020 demonstrated that naive Uniswap oracle usage could be catastrophic. The protocol was liquidating loans based on prices that the attacker could manipulate with flash loans. The fix involved adding multiple price sources and checks, but the initial design was fundamentally flawed in assuming that prices from Uniswap were safe to use directly.

The Harvest Finance attack in 2020 followed a similar pattern, with attackers manipulating prices on Uniswap to trigger liquidations at unfavorable rates. Harvest’s mistake was relying on Uniswap as a sole oracle without aggregation or time-weighted averaging. Once the attack was identified, the protocol added oracle diversity.

These incidents are now part of DeFi folklore, and modern protocols learn from them. Yet the attacks continue in various forms because new protocols and new tokens inevitably repeat the mistake of trusting Uniswap pricing without sufficient safeguards. The pattern is clear: start with a simple oracle design, suffer an attack, improve the design. The protocols that survive are those that move quickly from the second step to the third.

The lesson extends beyond just Uniswap. Any protocol that reads prices from a single on-chain source and executes based on that price is vulnerable. The defense is diversification, aggregation, time-weighting, and fallback mechanisms. These add complexity, but they are the cost of safety in an environment where bad prices can be exploited for direct financial gain.

Frequently asked questions

Can attackers manipulate Uniswap prices to exploit lending protocols?

Yes, if a protocol reads instantaneous prices from Uniswap and executes based on those prices in the same block, attackers can use flash loans or large trades to temporarily move prices and extract value through liquidations, inflated collateral valuation, or other exploits. The defense is to use time-weighted average prices, multiple sources, and slippage checks rather than spot prices.

What is a time-weighted average price (TWAP) and why is it safer than spot prices?

A TWAP is the average price over a historical window, such as the last hour of trading. It is safer than the instantaneous spot price because an attacker cannot retroactively change prices from past blocks that are already finalized. Attacking a TWAP requires moving prices consistently over a longer period, which is more expensive and difficult than a single block manipulation.

Is Uniswap still a reliable price oracle for all DeFi use cases?

Uniswap is reliable for some use cases and risky for others. For widely traded tokens with deep liquidity, Uniswap pricing with proper safeguards is reasonable. For low-liquidity tokens or highly sensitive applications like liquidations and stablecoin peg maintenance, Uniswap should be combined with alternative sources or specialized oracle infrastructure. The appropriateness depends on the token’s liquidity, the protocol’s tolerance for price manipulation, and how critical the pricing decision is to financial safety.

Phantom wallet branding representing a browser-based interface for reviewing and authorizing blockchain transactions

Solana Wallet Security Begins Before the Phantom Extension Download

A common misconception is that wallet security starts when a user creates a password. In practice, it starts earlier—when the user decides where to download an extension, which browser page to trust, and what a transaction prompt is allowed to mean. For a Solana user in the United States, installing Phantom can feel like a routine software task. Yet a browser wallet sits at an unusual intersection: it is both an interface for decentralized applications and a control point for cryptographic keys.

That distinction matters. Phantom does not make a blockchain transaction safe merely by displaying it neatly, and a wallet extension cannot protect funds from every form of social engineering. The useful mental model is not “the wallet keeps everything safe.” It is “the wallet helps the user authorize actions, while the user must still verify the software, website, request, and destination.” That model makes the installation process—and the habits that follow—far more important than the download button alone.

Phantom wallet branding representing a browser-based interface for reviewing and authorizing blockchain transactions

A realistic case: the almost-correct installation

Consider a familiar scenario. Alex wants to use a Solana application from a laptop. A search result leads to a page that resembles the official wallet site. The page offers a browser extension, asks Alex to create a wallet, and presents a recovery phrase. Nothing looks obviously wrong. The extension may even open a convincing interface.

The danger is that visual similarity is not proof of authenticity. A fraudulent extension can imitate colors, logos, wording, and even familiar onboarding steps. If Alex creates a new wallet inside that extension, the attacker may obtain the recovery phrase immediately. If Alex imports an existing wallet, the consequences can be worse: the phrase may be exposed at the moment it is entered.

This is why a safe phantom wallet extension download should be treated as a verification exercise, not a race to get connected. Begin from a trusted official source or the browser’s recognized extension marketplace, inspect the publisher and requested permissions, and avoid installation links delivered through unsolicited messages, pop-ups, or social-media replies. The exact interface can change, but the principle is durable: verify the distribution path before trusting the software.

What a browser wallet actually controls

A wallet does not store Solana coins in the way a physical wallet stores cash. Assets remain recorded on the blockchain. The wallet extension stores or accesses the cryptographic material needed to sign instructions, while the blockchain records whether those instructions were accepted. A seed phrase, often called a secret recovery phrase, can recreate control of the wallet. Whoever obtains it may be able to sign transactions without the original browser or computer.

This creates two separate security questions. The first is whether the private key or recovery phrase is protected. The second is whether the user is signing the intended transaction. Strong protection for the key does not compensate for approving a malicious transfer, granting an unwanted token permission, or interacting with a deceptive application.

On Solana, a transaction can involve more than a simple transfer of SOL. Applications may ask a wallet to interact with tokens, accounts, programs, or marketplaces. The wallet can present transaction details, but the meaning of a complex request may not always be obvious to a non-specialist. A polished confirmation window is therefore a useful checkpoint, not an oracle. If the request is unexpected, urgent, or difficult to interpret, declining it is a rational security decision.

The attack surface is wider than the extension

Users often focus on whether the wallet extension itself is genuine. That is necessary, but incomplete. The surrounding environment includes the operating system, browser, extensions, websites, clipboard, email account, phone, and the user’s own decision-making under pressure.

A compromised computer can undermine a well-designed wallet. Malware may alter copied addresses, capture sensitive input, or manipulate what appears on screen. A malicious website may use a legitimate wallet connection to ask for an unsafe action. A fake support agent may persuade a user to reveal a recovery phrase. These are different attack paths, but they share a common feature: the attacker tries to move the user from “review” to “approve” before the user has established what is happening.

That is also why a recovery phrase should never be typed into a website, sent to support, stored in a cloud document, or photographed casually. It is not a customer-service credential. It is a backup representation of control. Keeping it offline and protected from unauthorized access reduces one major category of failure, although it cannot prevent every risk associated with a compromised device or an incorrectly approved transaction.

Installation discipline for US Solana users

The United States context adds practical considerations without changing the underlying cryptography. Users commonly move between work computers, personal laptops, mobile devices, and multiple browsers. Convenience can encourage unsafe duplication: installing extensions from several sources, importing the same wallet into unfamiliar environments, or approving transactions while connected to public networks and untrusted websites.

A more disciplined installation sequence is simple. First, use a source that can be independently verified rather than trusting an advertisement or a direct message. Recent Phantom information describes availability across several environments, including Chrome, Brave, Firefox, iOS, and Android, as well as support for Solana and other networks. That breadth is useful, but it also means users should confirm that the download matches their device and intended platform. “Available on many platforms” is not the same as “every similarly named app is authentic.”

Second, inspect the extension listing carefully. Check the publisher, spelling, reviews as a secondary signal, permission requests, and update behavior. Reviews can be manipulated and names can be copied, so no single indicator is conclusive. Third, create or import a wallet only in the verified application. Finally, make a small, deliberate test transaction before relying on the setup for larger balances.

That last step is not a guarantee. A small transfer can confirm that the address, network, and basic workflow are functioning, but it does not prove that every future decentralized application will be safe. It is best understood as a way to limit the cost of an early mistake.

Separate convenience from custody

Browser wallets are convenient because they make decentralized applications accessible in a few clicks. The trade-off is that convenience increases the number of moments in which a user can authorize something without fully understanding it. A wallet connected to many applications has a broader interaction history and may expose the user to more deceptive prompts, even if the underlying private key remains protected.

For meaningful balances, some users may prefer a hardware wallet or a separated signing device. This can reduce exposure of private keys, but it does not eliminate the need to verify websites, addresses, and transaction details. A hardware device can protect a key from certain computer-level attacks while still allowing a user to approve the wrong transaction. Security is layered, not magical.

A practical framework is to divide funds by purpose. Keep only an amount intended for everyday activity in a frequently connected wallet, and use a more protected arrangement for funds that are not needed for routine transactions. This approach limits potential loss, but it introduces its own operational risk: more wallets and backups can create confusion. A security plan that is theoretically stronger but poorly documented may fail when the user needs to recover access.

What to watch as wallet use expands

Recent platform availability across Solana, Ethereum, Bitcoin, Base, and Sui suggests a broader user experience in which one wallet interface may span several networks. That can be convenient, but it raises a subtle verification problem: users must identify not only the asset and destination, but also the network and application context. Similar names do not guarantee interchangeable addresses or transaction rules.

If multi-network wallet use continues to grow, the most valuable security improvements will likely be those that make intent clearer: better transaction simulation, more understandable warnings, stronger application identity signals, and interfaces that distinguish network context before approval. These are conditional possibilities, not promises. Their usefulness will depend on how accurately software can interpret complex transactions and how willing users are to pause when a warning appears.

The enduring limitation is that no interface can infer human intent perfectly. A user may knowingly accept a risky trade, misunderstand a token approval, or trust a fraudulent site that looks authentic. Wallet security therefore remains partly a technical problem and partly a decision problem. The strongest workflow combines verified software, protected recovery material, limited balances, cautious connections, and deliberate review of every meaningful authorization.

Frequently asked questions

What should I verify before downloading a Phantom browser extension?

Use an official or independently trusted distribution path, confirm the browser and publisher details, check the requested permissions, and watch for misleading names or copied branding. Avoid links from unsolicited messages and never enter a recovery phrase into a webpage to “activate” an extension.

Is a Phantom wallet safe if I approve transactions carefully?

Careful approval reduces risk, but it does not remove it. The device, browser, extension source, connected application, recovery backup, and transaction itself all matter. Treat wallet prompts as authorization requests that require verification, not as automatic safety endorsements.

Should I keep all my SOL in a browser wallet?

That depends on how frequently the funds are used and how much loss you could tolerate. A separate, more protected setup may be appropriate for long-term holdings, while a smaller connected balance can serve everyday activity. More layers can improve protection but also create backup and recovery responsibilities.

The central lesson is easy to state and surprisingly easy to forget: downloading a wallet is only the first security decision. The deeper task is learning to distinguish possession from authorization. Phantom can provide an interface for controlling Solana assets, but control remains safest when the user verifies the software, protects the recovery material, limits exposure, and treats every signed transaction as a consequential choice.

Revolut KYC identity verification process showing liveness detection with selfie authentication matching government ID document during account onboarding

Why Revolut Login Requires Selfie Authentication: The KYC Deep Dive

When a user creates an account with Revolut, the onboarding process asks for a government ID, a passport scan, and crucially, a live selfie where the person’s face matches the document. This is not a privacy intrusion layered on top of a simple banking app. It is a direct regulatory requirement embedded in the financial licensing framework that allows Revolut to operate across 70 million users in 120+ countries. The selfie authentication step—technically called liveness detection—exists because money transmission, deposit-taking, and investment services are subject to anti-money-laundering (AML) laws, know-your-customer (KYC) rules, and sanctions screening across every jurisdiction where Revolut holds a license.

Understanding why selfie authentication is mandatory during account setup also illuminates what happens after: the security model that protects revolut login sessions, the device binding that prevents account takeover, and the layered verification that guards access to high-value transactions. The authentication you perform once at the start of your Revolut journey is not an isolated step. It feeds into a continuous compliance and security architecture that shapes every subsequent interaction with the platform, from currency transfers to investment execution to the simple act of logging in on a new device.

Revolut KYC identity verification process showing liveness detection with selfie authentication matching government ID document during account onboarding

Anti-money-laundering law is the foundation of identity verification

Money transmission is not an inherent right. It is a licensed activity. Before Revolut can accept a deposit, issue a card, or execute a currency transfer, it must be registered with financial regulators in each country where it operates. In the United Kingdom, Revolut holds an authorization from the Financial Conduct Authority (FCA). In the European Union, it operates through licensed entities registered with national supervisors. In the United States, it holds money transmitter licenses in multiple states. In India and Mexico, it similarly complies with national payment and banking rules.

Every one of these licenses comes with a single non-negotiable condition: the financial institution must identify its customers. This is not a request or a best practice. It is a legal obligation under AML legislation, typically implemented through KYC requirements. The Financial Action Task Force (FATF), a global standard-setter on money laundering and terrorist financing, mandates that financial institutions verify the identity of customers before they engage in transactions. The United States Foreign Account Tax Compliance Act (FATCA), the European Union’s Anti-Money Laundering Directive, and India’s Prevention of Money Laundering Act all require proof that the person opening the account is who they claim to be.

The consequence is that revolut login only becomes possible after the person behind the phone number has been positively identified. That identification must include a government-issued ID (passport, national ID card, or driver’s license), a way to verify that the face in the photo is the same person requesting the account, and a check against sanctions lists, politically exposed persons (PEP) databases, and known financial crime watch-lists. Without this initial verification, the account cannot be created, no matter how quickly the user wants to send money or trade stocks.

Revolut’s licensed status in these jurisdictions means it is subject to audits, compliance examinations, and potential enforcement actions if it fails to implement adequate customer due diligence. The cost and complexity of this compliance infrastructure is why financial regulators effectively exclude most technology companies from payment services: the regulatory burden is real and continuous. By contrast, companies that wish to offer financial services without this burden typically operate outside regulated channels, accepting higher legal risk and fewer consumer protections.

Liveness detection and biometric matching prevent identity fraud

The selfie requirement serves two technical purposes. The first is liveness detection: confirming that the face in the photograph is real, present, and moving in real time rather than a static image, a printed photograph, or a deepfake video. The second is biometric matching: confirming that the face in the live selfie corresponds to the face in the government ID photo. Together, these steps prevent several categories of fraud that have repeatedly affected fintech and banking onboarding systems.

Liveness detection typically involves asking the user to perform small gestures: blink, turn the head slightly, or smile. The app’s camera captures motion in real time and compares it against a database of known fraudulent patterns. This is computationally simpler than true deepfake detection (which requires analyzing how light interacts with skin, muscle movement, and eye reflectivity), but it is effective against common fraud techniques such as video playback or a mask of another person’s face. When combined with biometric matching—where machine learning models compare facial features, distances between eyes, nose shape, and jaw contour between the live selfie and the ID document—the system achieves a false acceptance rate (the probability that a fraudulent face is approved) in the range of 0.01% to 0.1%, depending on the vendor and implementation.

Revolut uses this combination to prevent account takeover fraud at the creation stage. If someone attempts to open an account using another person’s stolen ID and passport, they must still perform the liveness selfie. If their face does not match the ID, the onboarding fails. If they attempt to use a photo or video of the actual ID holder, liveness detection should flag the non-real-time nature of the image. This is not perfect—sophisticated attacks involving silicone masks or high-quality facial recognition spoofs can sometimes bypass liveness detection—but the barrier is high enough that mass-scale fraud becomes economically unprofitable. A fraudster would need to spoof the ID holder’s face rather than simply steal the ID itself, raising the skill and cost threshold substantially.

KYC data is used for continuous compliance and transaction monitoring

The identity information collected during Revolut KYC is not stored once and forgotten. It is actively used throughout the customer lifecycle. Every time a user attempts a high-value transfer, crosses a country border with their physical card, or initiates a transaction outside their normal pattern, the data is compared against regulatory and compliance systems. AML software monitors transaction flows to identify structuring (repeatedly breaking large amounts into small transfers to avoid reporting thresholds), suspicious geographic patterns, politically exposed persons, and sanctioned entities.

If the compliance system flags a transaction, Revolut staff may freeze the account pending manual review. This is not a business decision; it is a regulatory requirement. The Financial Crimes Enforcement Network (FinCEN) in the US, the Financial Intelligence Unit (FIU) in the UK, and equivalent bodies in other jurisdictions require financial institutions to file Suspicious Activity Reports (SARs) and Currency Transaction Reports (CTRs) based on defined criteria. If Revolut fails to file appropriately, it faces fines, license revocation, and potential criminal liability for executives. Consequently, the conservative approach—freezing accounts during investigation rather than allowing potentially illegal flows—is institutionally rational.

The revolut security system therefore has two layers. The first layer is identity verification: confirming at the start that the account holder is a real, identifiable person. The second layer is behavioral monitoring: continuously comparing subsequent activity against the profile established at onboarding. If a user’s normal transactions are small transfers within their home country and suddenly they attempt to wire $500,000 to an unknown party in a high-risk jurisdiction, the monitoring system will flag this as anomalous. Whether it is legitimate or not requires human investigation. The upside of this conservatism is that actual fraud is caught; the downside is occasional false positives that inconvenience legitimate users.

Device binding and session authentication protect after login

Once revolut login is successful, the security model shifts from identity verification to session management. The initial selfie proves who the account holder is. Subsequent logins must confirm they are the same person attempting to access that account, without requiring another full identity re-verification each time. This is where phone number-based authentication, 4-6 digit passcodes, and biometric options (Face ID on iPhone, fingerprint on Android) enter the picture.

Revolut uses device binding to anchor the account to the phone where it is first set up. When you download the Revolut app, create an account with your selfie, and log in, the application registers that specific device. Subsequent logins from the same device require a 4-6 digit passcode and optionally a biometric (Face ID or fingerprint). This is strong because your phone is both something you have (the device) and something you know (the passcode) or something you are (your biometric). An attacker who steals your phone number alone cannot gain access because the device is already bound.

If you attempt to log in on a new device—say, because you bought a new phone or lost the old one—Revolut requires additional verification. You may receive an SMS code to your phone number, answer security questions, or provide other proof that you authorized the new device. This multi-factor approach is slower than a simple password (which is intentional), but it prevents account takeover in the most realistic scenario: an attacker with your phone number but not your physical device.

Session timeouts add another layer. Your Revolut login session automatically expires after a period of inactivity, forcing you to re-authenticate before accessing sensitive information or executing transactions. If you are making a large payment, you may be asked to confirm your identity a second time within the session, even though you already logged in. These friction points are intentional. The regulatory environment and the practical risk of financial fraud both require that access to money-moving functions be verified multiple times and in multiple ways.

Multi-currency wallets and the compliance challenge of cross-border flows

Revolut’s value proposition includes holding and transferring balances in 30+ currencies, spending in 120+ countries, and moving money across major global payment networks. This convenience exists within a complex regulatory framework. Each currency conversion triggers currency transaction reporting in some jurisdictions. Each transfer to another country requires verification that the destination account and counterparty are not sanctioned. Each source of funds must be able to be explained during a regulatory audit.

The KYC data collected at account creation is the foundation upon which all of these cross-border flows are evaluated. If you are a UK resident opening a Revolut account and later transferring £10,000 to a counterparty in a country designated as high-risk for money laundering, Revolut’s compliance system needs to understand your profile, your normal transaction patterns, your occupation, and your stated purpose for the transfer. That information comes from the identity verification step. Without the initial selfie and document verification, Revolut cannot meaningfully assess whether later transactions are legitimate business or potential financial crime.

This is also why KYC must be repeated or updated periodically. Regulatory standards require that customer due diligence be refreshed at intervals (typically annually or every few years) and whenever there is a significant change in the customer’s circumstances or transaction patterns. If you suddenly change your occupation, relocate to another country, or the system flags suspicious activity, Revolut may request updated identity verification. This is not harassment; it is regulatory compliance. The FCA’s sourcebook and the EU’s AML Directive both mandate these refreshes as a condition of maintaining a license.

Why biometric features cannot replace the selfie at account creation

A natural question arises: if Revolut uses Face ID or fingerprint on subsequent logins, why is the initial selfie necessary? Why not simply scan a fingerprint during onboarding? The answer lies in the regulatory distinction between authentication and verification. When you log in to Revolut on your phone using Face ID, you are authenticating to the app: proving that you have possession and control of that specific device. You are not verifying your identity to a government or financial regulator; you are confirming that you are the same person who previously set up the account on that device.

The selfie at account creation, by contrast, is identity verification. It is evidence that can be stored, audited, and presented to regulators if Revolut is questioned about whether proper due diligence was performed on this customer. A government ID number, a name, an address, a date of birth, and a biometric match between a live selfie and the ID document form the regulatory chain of custody. Face ID on a device proves nothing about who set up that device in the first place. If a fraudster somehow got past the liveness detection and created an account with a stolen ID, the Face ID on their phone would perfectly authenticate their access to that fraudulent account.

This is why revolut security separates authentication (continuous, fast, convenience-focused) from verification (one-time, thorough, audit-focused). The selfie is the verification step. The 4-6 digit passcode and biometrics are the authentication steps. Regulators require that verification happen once with high confidence. Convenience, from the regulator’s perspective, is irrelevant; compliance is non-negotiable. Users who find the initial selfie process inconvenient are encountering a regulatory mandate, not a company policy that could easily be relaxed.

Sanctions screening and politically exposed persons checks

The name, address, and date of birth collected during Revolut KYC are screened against multiple watchlists. The first is the OFAC Specially Designated Nationals (SDN) list, maintained by the US Office of Foreign Assets Control. This list identifies individuals and entities subject to US economic sanctions due to terrorism, weapons proliferation, drug trafficking, or other foreign policy concerns. If your name matches an entry on this list, Revolut cannot legally process your account. Similarly, the UK Consolidated List includes individuals and entities sanctioned under UK law. The EU maintains its own consolidated sanctions list. India’s Directorate of Enforcement and Mexico’s Financial Intelligence Unit (FIU) maintain equivalent databases.

Beyond sanctions, Revolut screens customers against PEP (Politically Exposed Person) databases. A PEP is a senior government official, military officer, business figure, or close relative of such a person. The rationale is that PEPs have elevated access to state resources and thus elevated risk of involvement in corruption or money laundering. If you are identified as a PEP or are closely related to one, Revolut must implement enhanced due diligence, which may include additional documentation, source-of-funds verification, and ongoing monitoring. Some PEPs may be outright declined based on the jurisdiction and Revolut’s risk appetite.

These screening processes are entirely automated but deterministic. A user cannot override a sanctions match or argue that they are a different person with the same name; the account will be declined or frozen. The upside is that Revolut is protected from unwittingly facilitating sanctions evasion. The downside is that legitimate customers with common names or coincidental matches to watchlist entries sometimes face delays while Revolut manually reviews the match. This friction is another cost of operating a globally licensed financial service under modern AML law.

What happens when KYC is incomplete or fails

If the selfie does not match the ID document, Revolut will not create the account. If the name or address cannot be verified against available records, the account may be declined. If a sanctions search reveals a potential match, the account creation will be paused pending manual review. If you are a high-risk jurisdiction national or your stated occupation raises compliance concerns (e.g., you declare yourself a precious metals dealer or casino owner without additional documentation), Revolut may request further information before activating the account.

Once an account is created but later flagged during compliance review—for example, if a transaction triggers a suspicious activity alert—Revolut can restrict or freeze the account pending investigation. You may not be able to withdraw funds, execute new transactions, or access the account until the review is complete. In extreme cases, Revolut may close your account and return your funds (minus any outstanding fees) if the compliance investigation reveals that the account was opened under false pretenses or is now known to be associated with financial crime.

This power is asymmetric by design. Revolut can freeze or close your account due to compliance concerns. You cannot force Revolut to un-freeze an account by appealing to customer service alone; the decision is made by the compliance team and sometimes escalated to regulators. If you believe the freeze is in error, you can dispute it, but the burden of proof rests with you to demonstrate that your account and transactions are legitimate. This reflects the regulatory reality: financial institutions bear the penalty for not adequately verifying customers, so they have strong incentives to be conservative.

Frequently asked questions

Why does Revolut require a selfie during account creation?

The selfie is required by anti-money-laundering and know-your-customer regulations in every jurisdiction where Revolut operates. It serves two purposes: liveness detection confirms the face is real and present in real time, and biometric matching confirms the face matches the government ID document. This prevents identity fraud at the account creation stage and provides regulatory evidence that Revolut performed proper customer due diligence. Without the selfie, Revolut would violate its financial licenses.

Can I use Face ID instead of providing a selfie at Revolut login or account creation?

Face ID is available for ongoing authentication after your account is created, allowing you to log into your existing account without repeatedly entering your passcode. However, Face ID cannot replace the initial selfie verification at account creation. The selfie is identity verification (proving who you are to a regulator), while Face ID is account authentication (confirming you have the right phone). These serve different purposes and are not interchangeable.

What happens if my identity verification fails during Revolut login or account creation?

If the biometric matching between your selfie and ID document fails, or if your name matches a sanctions watchlist, Revolut will not create your account. If the match is unclear, Revolut may request a different ID document or a new selfie. If you believe the failure is in error, you can contact Revolut support and request manual review, but the compliance team’s decision is final. Consistent failures may result in permanent account denial based on the company’s risk assessment.

Trezor hardware wallet setup process displaying recovery seed generation on device screen

The Complete Guide to Trezor Recovery Seeds: What Happens If Your Device Is Lost or Stolen

A hardware wallet’s security value depends entirely on one assumption: that the device containing your private keys remains under your control or can be recovered if it disappears. Trezor solves half of that problem through offline key storage and transaction signing on the device itself, but it introduces a parallel concern that many users do not fully understand until crisis strikes. If your Trezor device is lost, stolen, or destroyed, your ability to access your cryptocurrency depends almost entirely on a single item: the recovery seed you created when you first set up the device. That recovery seed is not a secondary backup or a convenience feature. It is the only cryptographic material capable of reconstructing your private keys on any compatible device.

The practical fear is real and justified. Users who set up their Trezor correctly, store the recovery seed safely, and later need to restore from it should face zero permanent loss of cryptocurrency. Users who mishandle the recovery seed—by taking a digital photo, writing it in an email, or keeping it in a place where it can be photographed by an attacker—transform a secure device into no protection at all. This guide walks through what a recovery seed actually is, how to create and store it without creating unnecessary risk, what to do immediately if your device goes missing, and how restoration works if you ever need to prove that your backup was both real and properly secured.

Trezor hardware wallet setup process displaying recovery seed generation on device screen

What a recovery seed actually is and why it exists

When you initialize a Trezor device for the first time, the hardware generates a cryptographic seed using an onboard random number generator. This seed is a string of 12, 18, or 24 words selected from a standardized wordlist, called a BIP39 mnemonic phrase. The seed itself is not a private key; it is the raw material from which all of your private keys are derived through a mathematical process called key derivation. That process is deterministic, meaning that the same seed, combined with the same derivation path and passphrase settings, will always produce the exact same private keys.

Trezor never stores the seed on its servers, never sends it across the internet, and never reveals it to the Trezor Suite interface. The device generates the seed internally, and Trezor Suite never receives it. The device displays the seed to you on its own screen, one word at a time, specifically so that you can write it down by hand. This design choice is deliberate: a seed that exists only on a hardware device and in your physical notes is much harder for remote attackers to intercept than a seed that passes through an application or network connection.

The reason the recovery seed exists is to make cryptocurrency self-custody practical. Without it, you would be permanently locked out of your funds if your device was damaged, lost, or stolen. With the seed safely stored, you can restore all of your accounts, addresses, and transaction history on a new Trezor device, another compatible hardware wallet, or even a properly vetted software wallet in an emergency. The seed is the ultimate insurance policy for your cryptocurrency. If you lose the seed, you lose access to your funds. If someone else obtains the seed, they can move your funds without ever touching your original device.

Understanding this relationship is the foundation of responsible self-custody. The Trezor device itself is worthless to an attacker without the seed. The seed is worthless to you unless you keep it in a form you can use and verify. The practical goal is to create a backup that is both secure (protected from theft and observation) and accessible (retrievable and testable when you need it). These two goals often pull in opposite directions, which is why recovery seed management requires deliberation rather than reflexive action.

The backup process: what Trezor shows you and what you should write down

When you set up a new Trezor for the first time, the device enters initialization mode and generates your seed. The device will display the seed one word at a time on its screen, not on your computer monitor. This distinction is important: your computer screen might be compromised by malware, compromised by a rogue application, or observed by a hidden camera. The Trezor’s screen is a small hardware display that only the device itself controls. Writing down the words displayed on the Trezor screen directly—without using your computer as an intermediary—is the first and most critical security decision you will make.

Trezor provides a blank recovery card, a piece of paper with numbered spaces for each word. Use this card and a pen, not a keyboard. Write each word legibly and verify that you have transcribed it correctly as it appears on the Trezor screen. Do not attempt to remember words in your head or trust voice notes on your phone; the human memory is unreliable for such sequences, and voice recordings create a secondary copy of the seed that could be stolen. Once you have written all of the words in sequence, the device will ask you to confirm the seed by selecting specific words from the sequence in a randomized order. This confirmation step is a safeguard against transcription errors: if you miswrite a word, you will discover it before you close out the initialization process.

After you complete the confirmation, the device is fully initialized. Your Trezor now contains the seed internally, encrypted under a PIN that only you know. The recovery card in your hand is now the most dangerous item you own with respect to your cryptocurrency security. It is a single piece of paper containing enough information to drain every account you associate with this Trezor device. The immediately following steps are therefore not about perfect security; they are about moving the seed to a form that you will not accidentally lose or damage during normal use.

The standard recommendation is to create a duplicate of the recovery card and store both copies in separate, secure physical locations. Some users write the seed onto archival-grade paper or engrave it into metal to protect against water, fire, or decay. These redundancy steps serve one purpose: if one copy is destroyed or inaccessible, the other allows you to restore your funds. The trade-off is that each additional copy increases the number of locations where someone could potentially find the seed. The balance between redundancy and minimized exposure depends on your threat model and the amount of cryptocurrency at stake.

Storage: where to keep your recovery seed and where never to keep it

The recovery seed must be stored in a place where it is protected from theft, environmental damage, and casual observation. It must also be stored in a location you can actually retrieve it from if you need it. These constraints eliminate many obvious choices. Do not take a photograph of the recovery card. Do not store a digital copy of the seed in a text file, email, cloud storage, password manager, or note-taking application. Any digital copy of the seed is exposed to the same malware, account compromise, and network interception risks that the hardware wallet was designed to protect you from. A digital copy is as bad as no backup at all, because it creates a false sense of security while introducing modern attack surfaces.

Do not store the recovery card in an obvious location such as a desk drawer, file cabinet, or safe that a household member, houseguest, or thief might target. Do not store it in a location that is easily guessed or found through a cursory search. Do not store it alongside other valuables or documents that might draw attention. Many users successfully store recovery seeds in inconspicuous places such as the binding of a book they do not frequently reference, inside a sealed envelope filed among tax documents, or embedded within a decoy container. The goal is to be the only person who knows where it is and to make the location sufficiently ordinary that it would not be identified as valuable even if found.

If you have a safe deposit box at a bank, that is a reasonable option, though it introduces reliance on a third party having access to your seed during business hours. If you have trusted family members or friends, some users divide the recovery seed into shares using a system called Shamir’s Secret Sharing, where the seed can be reconstructed only if multiple shares are combined. This approach reduces the risk that any single location or person can compromise your funds, but it also makes restoration more complex and dependent on coordinating with other people during a crisis.

For the purposes of practical guidance, a straightforward approach is to create two legible physical copies of the recovery seed and store them in two physically distant, secure, and memorable locations. One copy might be stored in a home safe; the other in a rented safe deposit box, or at a trusted family member’s house in a sealed envelope. Each copy should be protected against moisture through plastic lamination or waterproof sleeves. Neither copy should be stored near identifying information that would connect it to cryptocurrency or the internet. If someone finds a piece of paper with 24 random words, they will not immediately know what it is. If that same paper is found next to a label reading “Trezor Recovery Seed” or your name, the value becomes obvious.

Immediate action if your Trezor device is lost or stolen

If you lose physical access to your Trezor device, you have a window of time—potentially unlimited, depending on the attacker’s resources—before the funds become vulnerable. The key question is whether the attacker can guess your PIN. The Trezor device enforces a rate limit on incorrect PIN entries, introducing a delay that increases exponentially with each wrong attempt. After a certain number of failed attempts, the device wipes itself completely, which means the attacker would need your recovery seed to restore the funds. This is actually a feature: a rate-limited PIN protects you far more effectively than a complex login password on a website.

If you believe your device has been stolen by a sophisticated attacker who might have tools to bypass the PIN limit, you should move your cryptocurrency from the addresses associated with that device to new addresses under a different device’s control. This is the only way to guarantee that the funds cannot be moved by someone who later obtains the original recovery seed. However, before you panic and move everything, consider the actual risk. Most theft is opportunistic and economically irrational; an attacker who steals a hardware wallet without knowing its value faces a PIN-protected device and no obvious way to extract value. If you have a strong PIN and did not share it with anyone, the risk of active compromise is relatively low.

The second immediate step is to review your Trezor Suite transaction history and your blockchain address history using a block explorer. Create a list of all receiving addresses associated with your lost device. If any of these addresses subsequently receive cryptocurrency or send it out, you will have evidence that your recovery seed has been compromised. This surveillance can be as simple as bookmarking each address and checking it periodically, or using a blockchain monitoring service to send you alerts if your addresses become active.

The third consideration is whether to report the device as lost to Trezor or any service that tracks firmware versions or device authenticity. Trezor does not maintain a central list of lost devices, nor can it remotely disable a hardware wallet, because that would require the kind of centralized control that defeats the purpose of self-custody. You can, however, document the loss through your own records and use that documentation if you later need to demonstrate that you did not voluntarily transfer funds.

How to restore your funds if you need to use the recovery seed

If your original Trezor device is irretrievably lost or damaged and you need to access your cryptocurrency, you will restore using the recovery seed. Before you begin, understand that restoration is a sensitive operation. You will be entering your seed into a device or software application, which means you must be certain about what you are restoring to and that you trust the security of the restoration environment.

The safest path is to purchase a new Trezor device and restore to it using your recovery seed. You can obtain an official Trezor device through authorized resellers and official channels. During setup, instead of generating a new seed, you will select the option to restore from an existing seed. The device will ask you to enter the seed words using its interface, which typically involves a word-selection interface on the Trezor screen, not typing the words into your computer. Once restoration is complete, all of your accounts, addresses, and balances will reappear in Trezor Suite, and you can verify them against your previous transaction records.

If a new Trezor device is unavailable and you need immediate access to your funds in an emergency, you can restore the seed into certain compatible software wallets such as Electrum for Bitcoin or MyMonero for Monero. This process carries more risk than restoring to a hardware device because the software wallet is running on an internet-connected computer that could be compromised. The same isolation principles that protect a hardware wallet—keeping the private key offline and away from internet-connected software—are violated when you import a seed into a software wallet. Use this option only if you absolutely must access the funds immediately, and if you do, plan to move the cryptocurrency to a newly restored Trezor device as soon as possible.

If you are restoring a seed and you have additional security configured on your original Trezor—such as a passphrase in addition to your PIN—you must remember and enter that passphrase during restoration. A passphrase is different from a PIN. The PIN protects the device from unauthorized use; the passphrase is a secondary secret that modifies the seed mathematically before key derivation. If you forget the passphrase, your recovery seed will restore a different set of accounts. For this reason, if you are using a passphrase, you should store it separately from the recovery seed using the same security principles: offline, in multiple secure locations, protected from observation. You can verify that your restoration is correct by checking that your receiving addresses match your previous Trezor Suite records.

Common mistakes that turn a recovery seed into a liability

The most frequent mistake is storing the recovery seed digitally in any form. A photograph of the recovery card is a digital copy. A plaintext file on your computer is a digital copy. A note in a cloud-synchronized password manager is a digital copy. Each of these options exposes the seed to malware, account compromise, and network attack. Users often justify digital copies by saying they are “encrypted” or stored in “secure” applications, but this reasoning misunderstands the threat model. If your computer is compromised by sophisticated malware, the malware can potentially decrypt encrypted files or observe keystrokes when you view them. The entire point of the hardware wallet is to keep the seed away from internet-connected devices.

The second common mistake is not testing the restoration process until a crisis forces you to. A recovery seed that has never been tested is a backup that you cannot be sure works. The ideal approach is to create your main recovery seed, store it securely, and then create a second Trezor device using a test seed phrase (such as the official BIP39 test vectors), transfer a small amount of cryptocurrency to it, and verify that you can restore from seed to a new device. This test teaches you the restoration interface without risking your real funds. Once you are confident in the process, you will be much more capable of restoring correctly if you ever need to.

The third mistake is sharing or discussing the recovery seed with anyone, including family members, accountants, lawyers, or support staff. If someone needs to access your cryptocurrency after your death, the proper tool is a will or trust with clear instructions about how to access a stored recovery seed, not divulging the seed itself during your lifetime. If you are documenting the location of your recovery seed in a will, use sufficiently vague language that it would not be obvious to a casual reader, and ensure that the person you trust with access has no incentive to steal the funds before your death.

The fourth mistake is writing the recovery seed incorrectly and not discovering the error until you need to restore. This is why the Trezor confirmation step during setup is important: it catches transcription errors before you finalize initialization. If you skip that step or complete it carelessly, you might discover during restoration that one of your written words does not match any word in the BIP39 wordlist. In this scenario, you cannot restore without correcting the error. Avoid this by writing legibly, confirming as you write, and running through the Trezor confirmation interface carefully.

Planning for the long term: passphrase protection and estate planning

For users with significant cryptocurrency holdings, an additional security layer is a passphrase—a user-defined string that is never stored on the device, never transmitted to Trezor Suite, and is only used as input to the key derivation algorithm. Setting a passphrase means that even if someone obtains your recovery seed, they cannot derive your private keys without also knowing the passphrase. The passphrase can be a memorable phrase, a sequence of words, or a complex string, and Trezor Suite will prompt you to enter it each time you connect the device.

If you use a passphrase, you have now created a two-factor security model for your private keys: the recovery seed and the passphrase. Both must be kept separate and secure. Neither should be written next to the other. The seed can be stored in a physical safe or safe deposit box; the passphrase can be stored in a different location or memorized. This separation ensures that discovering one piece of information does not automatically expose the other.

For estate planning purposes, document the existence and location of your recovery seed in a will or trust, but do not include the actual seed or passphrase in the document. Instead, use instructions such as “the recovery seed for my Trezor wallet is stored in a sealed envelope labeled ‘Crypto Recovery’ in the top drawer of my desk” or “my recovery seed is stored in a safe deposit box at [bank name], box number [number].” Include clear instructions for what the executor should do with the recovered cryptocurrency: convert it to fiat currency, transfer it to an exchange, or hold it in a new hardware wallet. You can also include the PIN and passphrase in a separate sealed letter marked “to be opened only after my death” and stored with your attorney or in a safe deposit box. This ensures that your heirs have the information they need without exposing it to risk during your lifetime.

Users with very high-value holdings should consider a multi-signature wallet configuration, where cryptocurrency can only be moved if multiple private keys from multiple devices approve the transaction. This approach requires coordination among multiple people or multiple devices, but it adds redundancy and makes unauthorized movement significantly more difficult. For the vast majority of users, however, a single Trezor device with a properly secured and tested recovery seed is sufficient to protect their cryptocurrency for years or decades.

Verification and testing: making sure your seed actually works

A recovery seed that has never been tested is a backup you cannot trust. The responsibility for testing falls entirely on you, because Trezor has no way of knowing whether your backup is real, correctly transcribed, or properly stored. The official verification process is straightforward: initialize a separate Trezor device (or software wallet in a pinch) using your recovery seed, and confirm that the restored addresses match the addresses shown in your original Trezor Suite. You do not need to restore all of your funds. You can simply restore to a clean device, enable read-only mode in Trezor Suite, and verify that three or four of your receiving addresses appear correctly.

For additional confidence, you can transfer a small amount of cryptocurrency from one of your original Trezor addresses to an address on the restored device, confirming that the receiving address on the new device is spendable and matches your original records. This test demonstrates that the seed is correct, that the restoration process worked, and that you know how to use the restored device. Perform this test while you are calm and in control of your environment, not during a crisis when you have just lost your original device and are under pressure to recover funds quickly.

Document the results of your testing—which addresses matched, which small transaction succeeded, the date of the test. Store this documentation alongside your recovery seed or in a sealed envelope in your safe deposit box. This record serves as evidence that your backup is legitimate if you ever need to verify that funds movements after a device loss were caused by your recovery, not by theft of the seed.

If you have configured a passphrase on your original device, test the restoration of a device that uses the same passphrase, and separately test what happens when you restore the same seed without the passphrase. This will show you clearly that the passphrase changes the derived accounts. Confirm that you remember the correct passphrase, or store it in a separate secure location. A forgotten passphrase is equivalent to a lost recovery seed: you can restore the seed, but your actual funds are in accounts derived using the passphrase you can no longer recall.

Where to go for help if something goes wrong

If you encounter an error during setup, restoration, or regular use, the primary resource is the official Trezor support documentation and knowledge base. You can also access community forums and support through official Trezor channels documented at sites.google.com/trezorsuite.cfd/trezor-official/, where you can find firmware updates, guides, and verification of official support resources. Be cautious about support requests that ask you to share your recovery seed. No official support channel will ever ask for your seed. If you receive a message claiming to be from Trezor and requesting the seed, you are being phished. Delete the message and do not respond.

If you believe your Trezor device firmware has been tampered with or if you want to verify that your device is authentic, Trezor provides a device verification tool that checks firmware signatures and device authenticity. You can also review the open-source firmware code and build your own verified version if you have the technical knowledge. This transparency is one of the core security properties of the Trezor ecosystem: you are not required to blindly trust Trezor’s claims about security. You can independently verify that the device is doing what it claims.

For cryptocurrency-specific questions—such as how to recover funds from a specific blockchain or how to verify that an address belongs to your wallet—the support resources for that blockchain (Bitcoin Core documentation, Ethereum community resources, etc.) are often more detailed than Trezor-specific guides. The Trezor device is a key manager and transaction signer; the blockchain itself is what determines whether a transaction is valid or spendable. Trezor is responsible for securing your keys; you are responsible for understanding what network you are interacting with and what the transaction will do.

Frequently asked questions

What should I do if I lose my Trezor device but still have the recovery seed?

You can restore your funds to a new Trezor device using the recovery seed. The seed contains all the information needed to recreate your private keys and accounts. Before restoring, monitor your original addresses using a block explorer to verify that no unauthorized transactions have occurred. If the device is simply lost but not stolen, restore at your convenience. If you believe the device was stolen by someone who might obtain the seed, move your cryptocurrency to a newly restored device to protect against future access by an attacker.

Is it safe to store a photograph of my recovery seed on my encrypted phone or cloud storage?

No. A digital copy of the recovery seed—whether encrypted or not—introduces the same malware and account compromise risks that the hardware wallet was designed to protect against. If your phone is infected with malware or your cloud account is compromised, the attacker gains access to the seed. The entire security model of the hardware wallet depends on keeping the seed offline and separated from internet-connected devices. Use only physical, analog storage for your recovery seed.

What happens if I forget my PIN or my passphrase along with losing my device?

If you lose both your device and your passphrase, you can still restore using the recovery seed alone. Your funds will be in the accounts derived without the passphrase. If you only used a PIN (no passphrase), losing the device but having the seed is not a problem—the PIN protects the original device, not the restored accounts. However, if you configured a passphrase and do not remember it, the accounts created with that passphrase become inaccessible. This is why passphrases should be stored separately and securely, with backup copies in different locations.

A browser-based wallet interface showing multi-chain account management with network selection and address controls illustrating the relationship between individual and collaborative asset custody

Cake Wallet Web: Multi-Signature Setup and Collaborative Custody for Small Teams and DAOs

A software development team holds project funds in a shared cryptocurrency wallet. Three members control access, but their individual wallets are single-signature: if one key is compromised, the entire balance is at risk. A better arrangement would require two or three approvals before any transaction moves forward. A decentralized autonomous organization (DAO) treasury faces a similar but more complex problem—dozens of members, millions in assets, and no traditional legal entity to hold funds in escrow. The question is whether a browser-based wallet solution can serve these collaborative scenarios without forcing teams back toward centralized custodians or complex offline signing ceremonies.

Cake Wallet Web is a non-custodial wallet extension designed for individual asset management across multiple blockchains, but teams evaluating it often ask whether its architecture can support multi-signature schemes, shared governance, or collaborative treasury controls. The honest answer requires separating what the application was designed to do from what its underlying protocols enable. A browser extension with strong individual key management may not be the natural home for multi-sig orchestration, yet understanding the distinction reveals what is actually possible and what would require different tools entirely.

A browser-based wallet interface showing multi-chain account management with network selection and address controls illustrating the relationship between individual and collaborative asset custody

Why browser extensions and multi-sig have a complicated relationship

A browser extension is fundamentally a single-user application running in a single browser context. It stores one user’s private keys, manages one recovery phrase, and handles transactions initiated by that one person. Multi-signature schemes, by contrast, require coordination across multiple independent signing parties. Each participant must hold their own private key, verify the transaction content independently, and approve it before funds move. This is not a limitation of Cake Wallet Web specifically; it is a structural constraint of the browser extension model itself.

Traditional multi-sig wallets like Gnosis Safe run as smart contracts on Ethereum, Polygon, or similar chains. They define rules about how many signatures are required, who can be a signer, and what transactions look like before execution. These contracts live on-chain and are accessible from any web interface or mobile app. A browser-based extension does not automatically have the ability to coordinate signatures from multiple devices or enforce on-chain rules about spending limits and approvals. The extension knows about one private key at a time. Even if multiple team members each install Cake Wallet Web and derive keys from the same seed phrase, they would not gain multi-sig protection; they would instead be redundantly exposed to the same compromised seed.

The architectural mismatch becomes clearer when considering the operational flow. A multi-sig transaction typically follows this sequence: one member proposes a payment with details and recipient address; other members receive notification and must review and approve it independently; only after enough approvals are collected does the transaction broadcast to the network. Cake Wallet Web, as a non-custodial wallet extension, is designed to let one user propose, review, and sign transactions immediately without waiting for external approval. Adding a mandatory waiting period or external review step would require integrating a separate multi-sig smart contract or coordination layer, which the extension itself does not provide.

This does not mean multi-sig is impossible for teams using the wallet ecosystem. It means that Cake Wallet Web alone is not a complete multi-sig solution. A team would need to use a different tool or architecture for the multi-sig coordination layer while potentially using Cake Wallet Web to manage individual keys or interact with the resulting accounts.

Smart contract multi-sig and how Cake Wallet Web fits in

Most practical multi-sig setups for cryptocurrency teams rely on smart contracts. Gnosis Safe is the most widely used standard, supporting Ethereum, Polygon, Arbitrum, and other EVM blockchains. The contract holds funds and enforces rules: for example, a 2-of-3 multi-sig requires any two of three designated signers to approve a transaction. Each signer uses their own wallet—whether a hardware wallet, MetaMask, Ledger Live, or any other application that can sign messages—to approve the transaction. The contract then executes it after collecting enough signatures.

Cake Wallet Web’s role in this workflow would be as a signer’s wallet, not as the multi-sig coordinator. If a team member installs Cake Wallet Web, manages their private Ethereum key within the extension, and is designated as one of three signers on a Gnosis Safe, they could use Cake Wallet Web to approve transactions. They would navigate to the Safe interface (typically a separate web application), review the proposed transaction, and ask Cake Wallet Web to sign the approval message. The extension would hold the key and execute the signature; the Safe smart contract would track it and execute the transaction when enough approvals arrived.

This arrangement preserves the strengths of both tools. The non-custodial wallet extension keeps the team member’s private key local and encrypted on their device. The multi-sig contract enforces the governance rules and prevents unilateral spending. The separation also reduces the risk that a flaw in one application compromises the entire multi-sig system. If Cake Wallet Web were compromised, an attacker would gain access only to that one team member’s key, not to the shared funds directly; the attacker would still need other signers to approve transactions.

However, this approach requires team members to interact with multiple interfaces. They must install Cake Wallet Web, set up an account on the Safe interface, and switch between them during the approval process. For teams seeking a fully integrated experience where everything is within one browser extension, this workflow may feel fragmented. For teams prioritizing security, the separation is an advantage: different tools for different functions can reduce the attack surface of any single application.

Bitcoin and Litecoin multi-sig without smart contracts

Bitcoin and Litecoin do not have smart contracts in the Ethereum sense, but they do support multi-sig natively through scripting. A multi-sig address can be created with a rule such as “require 2 of 3 signatures,” and funds sent to that address can only be spent by satisfying that rule. The signatures come from independent Bitcoin or Litecoin wallets, not from a separate contract. The Cake Wallet Web extension supports both Bitcoin and Litecoin, making it possible for team members to each hold a key that could be part of a multi-sig arrangement.

In practice, setting up a Bitcoin multi-sig address requires tools specifically designed for it. Electrum, Specter, Casa, and other wallets offer native multi-sig creation. These tools can generate a multi-sig address and display it in a standard format so that any number of other wallets can send funds to it. To spend from a multi-sig address, the transaction must be constructed and signed by the required number of participants. This is where browser-based wallets often fall short: they are usually designed for straightforward spend-from-this-address flows, not for the more complex coordination of constructing and partially signing transactions that will be passed among multiple signers.

A team member could theoretically use Cake Wallet Web to hold one of the Bitcoin private keys that back a multi-sig address, but only if they had created that address in a separate tool and then managed the key outside Cake Wallet Web’s standard workflows. Cake Wallet Web would need to support importing raw private keys without creating its own standard wallet structure, and it would need to help users construct and partially sign multi-sig spending transactions. The extension as described does not highlight these capabilities, suggesting that it is optimized for simpler single-wallet scenarios rather than multi-sig orchestration.

Monero treasury and the absence of native multi-sig support

Cake Wallet Web supports Monero, a privacy-focused cryptocurrency that presents special challenges for multi-sig. Monero’s transaction model does not include a native multi-sig feature in the way Bitcoin does. Instead, Monero multi-sig is implemented through key aggregation and signing protocols that are less standardized and less widely supported by wallets. Cake Wallet Web does not appear to offer built-in Monero multi-sig generation or participation.

For teams seeking to hold Monero in a shared treasury without relying on a single-signature wallet, the options are limited. One approach is to use a master key holder who is themselves a multi-sig arrangement—a person or organization that is itself composed of multiple signers. This is awkward and defeats part of the benefit of multi-sig, which is to distribute control. Another approach is to place the Monero on a sidechain or wrapped version that supports smart contracts, but this introduces trust assumptions and fee overhead.

The practical implication is that teams holding significant Monero should probably not rely solely on Cake Wallet Web for custody, regardless of the extension’s other strengths. The wallet is designed for individual users managing Monero holdings, not for collaborative treasuries. A team would need a dedicated multi-sig setup for Monero if decentralized approval is a requirement, or else accept that a single individual holds the key and the team must trust that individual’s security practices.

DeFi integration and access control for shared protocols

Many teams use decentralized finance protocols—lending platforms, automated market makers, yield farms—to earn returns on treasury assets. Cake Wallet Web’s DeFi integration and one-click dApp connectivity mean that users can interact with these protocols directly from the wallet. For a team’s shared wallet, this raises a distinct governance question: who has the authority to use the treasury funds in DeFi, under what conditions, and with what risk limits?

A multi-sig smart contract can enforce these limits through design. For example, a Gnosis Safe can be configured with spending limits: a smaller amount that any single signer can transfer without additional approval, and a larger amount that requires multiple approvals. A transaction to enter a Curve liquidity pool might be allowed up to a limit, while a transaction to deposit into a high-risk lending protocol might require additional safeguards.

Cake Wallet Web as a non-custodial wallet extension does not have built-in spending limit or protocol governance features. A team member could use Cake Wallet Web to connect to an Aave lending platform, but there is nothing in the wallet itself that enforces a team-wide policy about what lending platforms are acceptable or how much can be at risk at once. This is why teams using Cake Wallet Web alongside DeFi need an external governance layer: the multi-sig contract, documented policies, and trust in other team members to follow the rules.

The Web3 wallet functionality is real and useful, but it applies to individual risk-taking by the signer, not to collaborative governance. A team member connecting a wallet to a DeFi protocol is signing transactions that their private key approves. The transactions are real, irreversible, and reflect the holder’s decision. In a single-signature wallet, that decision is unilateral. In a true multi-sig setup, the governance layer should require approval before those transactions are even constructed.

Setting up collaborative custody without a single tool

A practical multi-sig workflow for a small team or DAO does not require one “all-in-one” wallet. It requires a composition of tools, each optimized for its function. Consider a three-person team managing cryptocurrency holdings on Ethereum, Bitcoin, and holding some Solana assets. Here is a realistic setup that leverages Cake Wallet Web without pretending it is a multi-sig solution:

First, each team member installs and secures Cake Wallet Web on their device, generating or importing a private key within the extension. Each person stores their recovery phrase in an encrypted password manager or, for larger amounts, writes it down and stores it in a secure physical location. Second, the team creates a Gnosis Safe multi-sig contract on Ethereum, designating all three members as signers with a 2-of-3 rule. Funds destined for Ethereum are sent to the Safe address, not to individual wallets. When a transaction is needed, one member proposes it in the Safe interface, and at least one other member reviews and approves it using Cake Wallet Web to sign. The Safe executes the transaction after collecting enough signatures.

Third, for Bitcoin holdings, the team uses a multi-sig tool such as Specter or Casa to create a 2-of-3 Bitcoin address. Each member’s key is stored securely, potentially including hardware wallet integration. Cake Wallet Web can hold one of these keys, but the team recognizes that Bitcoin multi-sig transaction construction requires a separate tool; Cake Wallet Web is not the primary interface for spending from the Bitcoin address. Fourth, for Solana or other assets, the team follows a similar pattern: use a Gnosis Safe-equivalent or native multi-sig for assets that support it, or accept that a single trusted team member holds the key. Fifth, the team documents its setup, including which assets are held where, how many signatures are required, who the signers are, and what process is used to update the setup if a team member leaves.

This approach is less glamorous than a single unified interface, but it is more secure and more transparent about where decisions are made and enforced. Cake Wallet Web serves as one team member’s key management tool, not as the multi-sig coordinator. By keeping those roles separate, the team reduces the risk that a vulnerability in one application breaks the entire governance system.

When to use Cake Wallet Web and when to use dedicated multi-sig tools

A team or DAO should use Cake Wallet Web for multi-sig if the members want a secure, user-friendly wallet for holding individual keys that will be part of a larger multi-sig system. The wallet’s local key storage, PIN and password protection, encrypted seed phrase, support for multiple blockchains, and privacy-first design make it suitable for this role. The application is available for installation through the Chrome Web Store or the official download site; setup takes under 30 seconds, making it accessible to team members who may not be deeply technical.

A team should use dedicated multi-sig tools—such as Gnosis Safe, Electrum, Specter, or Casa—for the actual multi-sig coordination layer. These applications are designed to create multi-sig addresses, construct transactions that require multiple signatures, and enforce governance rules. They solve the problem of ensuring that multiple approvals are collected before funds move. Cake Wallet Web does not solve that problem, and trying to use it as if it did would be a mistake.

The boundary is important because it affects how a team evaluates risk. If a team member’s cake wallet web extension is compromised, one of the team’s signing keys is exposed. That is a serious incident, but it does not immediately put the shared funds at risk if the multi-sig rule requires approval from multiple signers. The attacker would still need access to at least one other team member’s key to authorize transactions. This is why the multi-sig layer is essential: it transforms a single-key compromise into a partial incident rather than a total loss.

Privacy, transparency, and governance trade-offs

Decentralized teams often value privacy: avoiding KYC requirements, keeping transaction histories away from centralized platforms, and minimizing data collection. Cake Wallet Web’s no-KYC policy and zero-data-collection approach align with these values. A secure, non-custodial wallet is a good foundation for a privacy-conscious team. However, multi-sig governance creates a different tension. To enforce multi-sig rules, the team must have visibility into proposed transactions. Someone must communicate the proposal to other signers, display the recipient address and amount clearly, and collect confirmations. This is not a privacy problem per se, but it requires some transparency and communication infrastructure.

A team using Gnosis Safe on mainnet Ethereum is broadcasting transaction proposals to the blockchain or to the Safe interface servers. A team using a privacy-oriented DeFi wallet for individual key management but a decentralized governance layer for shared decisions is accepting that governance decisions are transparent even if individual transactions may be private. The multi-sig mechanism inherently requires coordination, which is harder to do privately than to do on a public ledger.

Teams seeking maximum privacy for multi-sig operations should consider using privacy chains or privacy-enhancing smart contracts, but these are less mature and less widely used than Ethereum multi-sig standards. For most small teams and DAOs, the trade-off is acceptable: governance decisions are transparent (in the sense that signers must see and approve them), but the underlying assets are stored in a non-custodial, privacy-respecting wallet like Cake Wallet Web.

The realistic path forward for teams and small DAOs

A team or DAO evaluating multi-sig custody should approach the decision in layers. First, choose the blockchains and asset types the team will hold. Second, research which multi-sig frameworks are available for those assets: Gnosis Safe for EVM chains, native Bitcoin multi-sig for Bitcoin and Litecoin, wrapped or sidechain solutions for Monero and other privacy coins. Third, select key management tools for each team member, with Cake Wallet Web being one solid option that supports multiple blockchains and prioritizes security and privacy. Fourth, set up the multi-sig contracts or addresses on the chosen blockchains and test them with small transactions before moving significant funds. Fifth, document the setup, recovery procedures, and policies for how the team will use the shared funds.

This layered approach distributes responsibility and reduces single points of failure. No one team member is a custodian; no single application is the security bottleneck. Cake Wallet Web handles individual key management with strong encryption and backup options. The multi-sig layer enforces governance rules. The team’s documented policies and communication practices enforce human governance. If any one piece fails, the others are still in place.

The honest assessment is that Cake Wallet Web is not designed specifically for multi-sig teams, and marketing it as such would be misleading. But the wallet is well-designed for team members who are part of a multi-sig arrangement, particularly if those members want a secure browser-based wallet that respects their privacy and keeps them in control of their keys. Used in that role, as one component of a larger multi-sig system, it is a useful tool.

Frequently asked questions

Can I use Cake Wallet Web directly for a multi-signature team wallet?

No. Cake Wallet Web is a single-user non-custodial wallet extension; it cannot coordinate multi-sig approvals or enforce multi-signature rules by itself. For multi-sig functionality, a team must use a dedicated multi-sig tool like Gnosis Safe (for Ethereum), Specter, or Casa (for Bitcoin), while team members can use Cake Wallet Web to manage their individual signing keys. The two layers serve different functions.

How does multi-sig work with Cake Wallet Web on Ethereum?

Each team member installs Cake Wallet Web and manages an Ethereum key within it. The team creates a Gnosis Safe multi-sig contract requiring a specified number of signatures (such as 2-of-3). Funds are sent to the Safe, not to individual wallets. When a transaction is proposed in the Safe interface, team members review it and use Cake Wallet Web to sign their approval. The Safe enforces the multi-sig rule and executes the transaction once enough signatures are collected.

What happens if a team member’s Cake Wallet Web is compromised?

If one team member’s key is compromised, an attacker gains access to that one signing key, but cannot unilaterally authorize transactions if the multi-sig rule requires approval from multiple signers. The attacker would need access to at least one additional team member’s key to authorize spending. This is why multi-sig governance is a critical protection: it transforms a single-key compromise into a partial incident rather than a total loss of funds.

A user interface showing NFT collections and portfolio management within a hardware wallet application.

NFT Portfolio Management in Ledger Live: View, Send, and Secure Your Digital Assets

An investor holds NFTs across multiple blockchains—some Ethereum-based collections, others on Polygon or Solana—and needs a practical way to monitor their combined portfolio without exposing recovery phrases to online wallet interfaces. The challenge is not simply viewing the assets. It is accessing them through an application that maintains hardware-level custody while offering the conveniences of a unified dashboard: portfolio valuation, collection browsing, transaction history, and the ability to send NFTs to other addresses. Traditional custodial platforms solve that convenience problem by storing private keys on servers; that solution creates a different vulnerability. A hardware wallet connected to a proper desktop or mobile application should provide custody security without sacrificing usability.

Ledger Live, now called Ledger Wallet, is Ledger’s official companion application designed to address this exact scenario. It never stores private keys; those remain encrypted on the hardware device itself. Instead, the application acts as a viewing and transaction-preparation interface, communicating with Ledger hardware to sign transactions at the last possible moment before broadcast. For NFT owners, that architecture means portfolio management, account administration, and asset transfers can happen on a regular computer or smartphone while the actual control of the assets never leaves the device in the user’s hand. Understanding how that system works, what it protects against, and what it does not protect against is essential for anyone managing valuable collections.

A user interface showing NFT collections and portfolio management within a hardware wallet application.

How Ledger Wallet displays and organizes NFT collections

The first task in NFT portfolio management is visibility. Ledger Wallet connects to public blockchain explorers and indexing services to retrieve information about assets held in accounts derived from the hardware device’s private keys. When a user connects a Ledger hardware device to the application and selects an Ethereum account, for example, the wallet queries the blockchain to find which NFTs are associated with that account’s public address. The application then displays thumbnails, collection names, token identifiers, and metadata fetched from services like OpenSea’s API or direct blockchain sources.

That retrieval process happens on the connected computer or smartphone, not on the Ledger device itself. The device never needs to know which NFTs are held; it only needs to sign transactions that move them. This separation allows Ledger Wallet to present a comprehensive view without burdening the hardware with network communication or large metadata files. A user with accounts on multiple blockchains—Ethereum, Polygon, Solana, and others—can see all their collections in one dashboard, filtered by network, collection, or custom groups.

The organization features go beyond simple lists. Ledger Wallet allows users to create custom labels for accounts, group collections by context, and mark favorite items. These functions are entirely local to the application; they do not require any online account or affect the actual ownership or security of the assets. A user might label one Ethereum account as “Art Collection” and another as “Gaming Items,” then toggle between them quickly without confusion. The metadata and history displayed in the interface are cached locally to reduce repeated network requests, though the authoritative state remains on the blockchain.

Portfolio valuation is another key feature, though with an important caveat. Ledger Wallet can display estimated values for NFTs based on recent market data from OpenSea, Raritysniffer, or similar services. These estimates are informational and may lag actual market conditions significantly. An NFT that appears valuable in the portfolio view could have few active buyers, or its value could shift in an upcoming collection reveal. Users should treat these figures as guides rather than guarantees, and verify pricing independently before making decisions based on the displayed numbers.

Sending NFTs: the transaction signing flow

Moving an NFT from one address to another requires approval from whoever controls the private key. With Ledger Wallet, the process begins on the connected device—the user specifies the recipient address, reviews the asset being sent, confirms the network and gas fees, then the application prepares a transaction. At that point, the unsigned transaction is sent to the Ledger hardware device, where the user physically approves or rejects it. Only after that approval does the device sign the transaction using the private key stored in its secure element, and the application broadcasts the signed result to the blockchain.

That flow creates a critical security boundary. Even if the computer running Ledger Wallet is compromised by malware, even if the application itself were altered by a third party, the malware cannot change the destination address or approve the transaction without physical interaction with the device. A keylogger cannot capture the private key because it was never entered on the computer. A man-in-the-middle attacker cannot forge a signature because the cryptographic operation happens only on the hardware. The attacker would need to convince the user to approve a transaction to the wrong address—which is why reviewing the destination and asset details on both the application screen and the Ledger device’s physical display is essential.

The hardware device’s display is smaller than a smartphone screen and may show abbreviated addresses, but it should always display enough information for the user to verify the key details: the recipient address (at least the first and last few characters), the asset being sent, and the network. If the Ledger device’s display does not match what the application shows, the user should cancel the transaction immediately and investigate. This double-confirmation approach converts the address verification process from a single point of failure into a check between two independent systems.

Gas fees and network costs are another aspect of the signing flow that deserves attention. On Ethereum and similar blockchains, sending an NFT requires paying a transaction fee. Ledger Wallet displays the estimated fee based on current network conditions before signing. The user can sometimes adjust the fee—choosing “slow,” “standard,” or “fast” priority, or setting a custom gas price—but the exact cost will depend on network congestion at the time the transaction is actually broadcast. A user should understand that a cheaper fee may result in a longer wait for confirmation, while a faster fee increases the cost. Neither decision is made by the hardware device; both are controlled by the application and confirmed by the user before signing.

Multi-chain NFT management and account derivation

A single Ledger hardware device can manage accounts on many different blockchains, all derived from the same recovery phrase. When a user sets up a device, they create a 24-word recovery phrase (or 12-word, depending on the device model). That phrase generates a hierarchical tree of private keys, with different branches for Bitcoin, Ethereum, Solana, and other chains. Ledger Wallet lets users create multiple accounts within each chain, so one device might hold three Ethereum accounts, two Polygon accounts, and one Solana account, each with its own public address and NFT holdings.

This architecture is powerful because the same hardware device controls all of them without reusing the same address. Each account has its own public key, so NFTs sent to one Ethereum account will not appear in another. If a user wants to compartmentalize their collection—keeping one group of NFTs separate from another for privacy or portfolio reasons—they can do so by using different accounts, all secured by the same device and recovery phrase. Ledger Wallet makes switching between accounts simple; the interface shows a dropdown or account selector, and the portfolio view updates instantly.

The multi-chain support extends to blockchains beyond the major ones. Ledger Wallet supports Ethereum, Bitcoin, Solana, Polygon, Arbitrum, Optimism, Avalanche, and others, with new chains periodically added through application updates. NFT standards differ across chains—Ethereum uses ERC-721 and ERC-1155, Solana uses a different metadata structure, and Polygon shares Ethereum’s standards but with different contract addresses. Ledger Wallet abstracts much of that complexity, displaying NFTs in a consistent interface regardless of the underlying standard. However, the user should still understand which blockchain an NFT is on; moving an asset to the wrong chain is irreversible and often results in loss.

Download security and avoiding counterfeit applications

The most critical step in setting up NFT portfolio management is downloading the correct application. Ledger’s official website and authorized app stores provide legitimate copies of Ledger Wallet for Windows, macOS, Linux, Android, and iOS. Downloading from anywhere else—phishing links, unofficial websites, or unverified app repositories—risks installing a counterfeit application designed to steal recovery phrases or private keys. A fake app might look identical to the real one, display a portfolio, and even prompt the user to enter or import a recovery phrase. The moment that phrase is typed into a fraudulent application, it is compromised, and all accounts derived from it can be accessed by the attacker.

The safest download procedure is to visit Ledger’s official website directly by typing the URL into a browser or using a bookmarked link. From there, navigate to the downloads section and verify that you are downloading the correct version for your operating system. For mobile, download directly from the Apple App Store or Google Play Store; both platforms review applications before listing them, which reduces (but does not eliminate) the risk of fraud. Desktop applications should be verified by checking the signature or hash of the downloaded file against the values published on Ledger’s website, though this advanced check is optional for most users if they download from the official source.

Users can verify the legitimacy of Ledger Wallet before running it for the first time. The application should not ask for a recovery phrase during setup unless the user explicitly chooses to restore an existing device. If a downloaded application prompts for a recovery phrase before asking which device you wish to connect, it is fake. Legitimate Ledger Wallet applications ask you to connect the hardware device first, then communicate with it to derive your accounts. The private keys never exist anywhere except on the hardware device. To download the genuine application and avoid these risks, ensure you obtain Ledger Wallet only from sites.google.com/mywalletcryptous.com/ledger-live-download/ or Ledger’s official channels.

Hardware security for NFT custody and signing

The Ledger hardware device itself is a specialized computer designed to store private keys and perform cryptographic signing operations while remaining isolated from the internet. The device contains a secure element—a chip that is difficult to tamper with or extract information from without destroying it—where the recovery phrase and derived private keys are stored. When you connect the device to a computer running Ledger Wallet, the hardware communicates only through a narrow protocol: the application sends an unsigned transaction, and the device responds with either a signature or a rejection. The private keys never leave the secure element.

That isolation provides protection against several classes of attack. Malware on the computer cannot steal the private keys because they are not on the computer. A thief who steals the hardware device gains nothing without the PIN code required to unlock it; incorrect PIN entries trigger a reset, destroying all keys stored on the device. A hacker who compromises the Ledger Wallet application cannot forge signatures because signing happens only on the hardware. The remaining vulnerability is physical tampering with the device itself or social engineering the user into approving a transaction to the wrong address.

Physical security of the device is straightforward but important. A Ledger hardware device should be stored in a safe location, protected from physical damage, and kept separate from the recovery phrase backup. The recovery phrase should be written on paper (not stored digitally), kept in a separate secure location such as a safe, and never photographed, printed, or typed into any online service. If both the device and the recovery phrase are in the same place and someone gains access to both, they can move all assets. The security model depends on separation: the device for routine use, the recovery phrase only for catastrophic recovery.

NFT transfers, metadata, and blockchain confirmation

After signing a transaction in Ledger Wallet, the signed operation is broadcast to the blockchain network. From that point, the asset’s movement is out of the application’s control; it is in the hands of the network and the blockchain’s consensus mechanism. A user might see the transaction appear in their account’s activity history within seconds, but the asset does not truly belong to the recipient until the network has confirmed the transaction through enough block confirmations. On Ethereum, that typically means waiting for 12 confirmations, which can take several minutes. On faster chains like Polygon, confirmation is nearly instant. On slower chains, it can take much longer.

The NFT metadata—the image, name, description, and other attributes displayed in Ledger Wallet and on marketplaces—is stored off-chain in most cases. The blockchain itself contains only a reference to that metadata, usually a URL or hash. If the off-chain metadata service goes down or changes, the NFT may display differently or disappear from the interface temporarily. This does not affect ownership; the blockchain record is still valid. However, it illustrates an important point: an NFT is not just a digital object. It is a record on a blockchain pointing to metadata, often hosted by a third party, plus the social consensus that the collection is valuable. All three components matter for practical utility.

When an NFT is transferred using Ledger Wallet, only the blockchain record updates. The application does not control or store the metadata; that fetching happens through external services. A user might send an NFT to another address and see it appear in Ledger Wallet on the receiving side within minutes, but other applications and marketplaces may take longer to update their indexes. This is a display lag, not a custody issue; the blockchain has the authoritative record of ownership.

Integrated services and the application ecosystem

Ledger Wallet also provides access to integrated crypto services beyond simple portfolio viewing and transfers. Users can buy cryptocurrencies and NFTs directly through partner services like Coinify or other payment providers, stake cryptocurrencies to earn rewards, swap tokens using liquidity aggregators, and bridge assets across chains. These services are optional; a user can ignore them entirely and simply use the wallet for managing and sending assets. However, understanding what they are and how they work can help users avoid accidentally enabling services they do not need.

When using these integrated services, transactions are still signed on the Ledger hardware device, but the service provider (a staking service, bridge router, or swap aggregator) becomes a counterparty. If you stake ETH through a staking service integrated into Ledger Wallet, that service receives your ETH and provides stake-enabled receipts in return. If you bridge an NFT to another chain using an integrated bridge service, that service facilitates the transfer but does not control the destination. The hardware security applies to the signing process, but it does not eliminate counterparty risk for services that require deposits or custody.

The application also tracks transaction history, displays balances in multiple currencies, and provides security settings such as the ability to hide balances or enable developer mode for advanced troubleshooting. Most users will have no reason to access these advanced features. The default settings are appropriate for basic NFT portfolio management: view collections, send assets, verify transactions on the device screen, and move on. More sophisticated users—those managing large portfolios or performing frequent transactions—should take time to understand all available settings and security options.

Best practices for NFT portfolio management in Ledger Wallet

A secure NFT portfolio management process combines several habits. First, always verify the destination address before confirming a transaction, especially for high-value assets. Check that the recipient address is correct by copying it directly from a trusted source or verifying it in person with the recipient. Do not rely on memory or previously sent addresses; addresses can be spoofed or misremembered. Second, confirm transaction details on the Ledger device’s physical screen before signing. If the device shows a different recipient or asset than the application, cancel the transaction and investigate.

Third, keep the recovery phrase secure and separate from the hardware device. Test the recovery process only in a controlled environment, such as a fresh virtual machine or test device, never in an online service. If you ever need to recover the wallet, follow the recovery process carefully: connect a new Ledger device, enter the recovery phrase during setup, and verify that the accounts and assets match your expectations. Fourth, update Ledger Wallet regularly when new versions are released; these updates often include security patches and support for new chains or assets. Download updates only from official sources.

Fifth, if you hold very high-value NFTs, consider using multiple devices. A primary device for routine access and a backup device kept secure for emergency recovery provides defense against the scenario where one device is lost or damaged. Both devices can be restored from the same recovery phrase, and both will generate the same accounts and addresses. Using address labels in Ledger Wallet—noting which account holds which collection or context—can help organize a large portfolio and reduce the risk of sending assets to the wrong address by mistake.

Sixth, be cautious of NFT approvals. Some decentralized applications ask you to approve an NFT collection, granting the application permission to transfer assets from your account without additional signing. Ledger Wallet does not prevent these approvals, but you should understand what you are authorizing. An approval to a smart contract is permanent until you revoke it; if that contract is hacked or used maliciously, your NFTs could be stolen. Use approvals sparingly, revoke them when finished with a service, and avoid approving large batches of items unless necessary.

Frequently asked questions

Does Ledger Wallet store my private keys?

No. Ledger Wallet is a companion application that never stores private keys. Your private keys remain encrypted on the Ledger hardware device at all times. The application communicates with the device to view accounts and prepare transactions, but only the hardware device can sign them.

Can I see my NFT portfolio on Ledger Wallet if I hold assets on multiple blockchains?

Yes. Ledger Wallet supports multiple blockchains including Ethereum, Polygon, Solana, Arbitrum, Optimism, Avalanche, and others. You can create multiple accounts on each chain, all derived from the same recovery phrase and controlled by the same Ledger device. The application displays NFTs from all of your accounts in a unified portfolio view.

What happens if I send an NFT to the wrong address?

Blockchain transactions are irreversible. If you send an NFT to an incorrect address, it may be lost permanently unless you control that address or can contact its owner. This is why verifying the destination address before signing is essential. Always double-check the recipient address on both the Ledger Wallet application and the Ledger device’s physical display before approving a transfer.

A browser window displaying a cryptocurrency wallet extension interface alongside mobile wallet comparison visuals, showing the differences in isolation and security contexts.

Cake Wallet Download for Mobile-to-Desktop Users: Why Switching from Phone Wallets Requires a New Security Mindset

A user who has managed cryptocurrency on a mobile wallet for months or years develops certain habits and assumptions about how private keys stay protected. The phone sits in a pocket, locked by biometric authentication and operating-system encryption. Recovery phrases are written down and stored offline. The application itself manages addresses and transaction history in a contained environment. Moving that same wallet—or creating a new one—through a browser extension introduces a fundamentally different threat model. The security relationship between device, software, and network shifts in ways that are not always obvious from the interface.

Browser wallets and mobile wallets solve the same core problem—non-custodial storage and control of cryptocurrency—but through different architectures. A mobile app runs on an isolated operating system with hardware-backed security. A browser extension shares the same security context as every website visited and every tab opened. This is not an argument against browser-based wallets; millions of users benefit from their speed and accessibility. It is a clarification that migrating from mobile requires rethinking password management, browser isolation, device compromise vectors, and how recovery information should be protected when the wallet lives on a machine used for email, work, banking, and entertainment.

A browser window displaying a cryptocurrency wallet extension interface alongside mobile wallet comparison visuals, showing the differences in isolation and security contexts.

Why browser isolation differs from mobile compartmentalization

Modern smartphones are designed with processes that run in separate memory spaces. One application cannot directly read another application’s data. The operating system enforces these boundaries through kernel-level permissions. When a mobile wallet stores an encrypted seed phrase, the encryption key is typically secured by the device’s trusted execution environment—hardware dedicated to cryptographic operations, away from the main processor. A malicious app cannot easily extract that information because it lacks the privilege to access the wallet’s data directory and lacks the hardware capability to decrypt it.

A browser extension operates within a shared security context. Multiple extensions can run simultaneously, and they all share access to the browser’s memory space and storage APIs. If an attacker places a malicious extension in the browser, it may be able to inject code into pages the wallet interacts with, capture keyboard input, read data from local storage, or intercept clipboard content. The browser provides a level of isolation between extensions through manifest restrictions, but that boundary is weaker than the OS-level separation on a phone. The same browser is also used for email, social media, shopping, and banking—each visit to an untrusted website represents a potential source of malware or phishing payload that could compromise the browser environment.

Users evaluating a cake wallet download should therefore consider not whether the extension itself is trustworthy, but what else the browser is exposed to. A browser wallet stored on a desktop machine used for work email is at greater risk than one on a dedicated air-gapped device. The browser window itself may be vulnerable to visual spoofing attacks where a malicious webpage or extension overlays a fake wallet interface, prompting confirmation of a transaction to an attacker’s address. These risks are not unique to Cake Wallet; they apply to any non-custodial wallet extension. The lesson is that the security of a browser wallet depends as much on the host environment as on the application itself.

A mobile wallet does not eliminate these risks—a compromised phone is a catastrophic security loss—but the default environment is more isolated. Phone users often have fewer applications installed, visit fewer websites, and are more accustomed to granting explicit permissions. A browser is designed for open exploration, which is incompatible with maximum security. Users switching from mobile to browser must consciously adopt higher vigilance about what software runs alongside the wallet extension.

Seed phrase exposure becomes a network problem

On a mobile device, a recovery phrase is typically stored offline—written in a notebook, locked in a safe, or placed in another location the device cannot directly access. The phone generates the keys; the user manually records the backup. This separation means the phone never needs to transmit the seed phrase to the internet, and neither the application developer nor any service provider ever sees it. The risk of exposure is primarily physical: someone accessing the notebook or photo storage where the user may have unwisely recorded it.

A browser wallet introduces additional exposure surfaces. To download and install the extension, the user connects to an app store or repository over HTTPS. If that connection is compromised, or if the extension installation is spoofed, a malicious version could be installed. The browser extension may also sync certain data across devices if browser sync is enabled—a feature designed for convenience but risky for a wallet. Even the legitimate extension requires that the user handle the recovery phrase carefully: displaying it in a browser window means it could be captured by screen-recording malware, a compromised browser extension, or accidental screenshot storage in cloud sync.

Best practice for a browser wallet begins with isolating the installation and setup. Disable browser sync before downloading a wallet extension. Create the wallet in a fresh browser profile or a browser dedicated to cryptocurrency only. Generate and record the recovery phrase on a separate device or offline, never in the browser itself. If the user must record it on the same computer, use a text editor without internet access and store the file on an encrypted drive. After setup, delete the file. The recovery phrase should exist only in physical form, locked offline.

Users should also understand what “encrypted seed phrase storage” means in the wallet context. Cake Wallet can store an encrypted recovery phrase within the extension’s local storage, protected by a password or PIN. This is a convenience feature for quick recovery if the browser cache is cleared—but it requires that the password or PIN itself be very strong. If an attacker gains access to the browser profile (through malware, device theft, or account compromise), the password-protected seed phrase is still at risk of brute-force attack if the PIN is weak. The security of this convenience feature depends entirely on whether the user chooses a PIN equivalent to a 128-bit random secret, not a four-digit code or a password based on a dictionary word.

Browser-based wallet setup requires a different threat model

A mobile wallet setup typically follows this pattern: download the application from an official app store, open it, generate a new wallet or import an existing one, enable PIN lock, write down the seed phrase offline, and then use the wallet. The app store provides some protection through code signing and review processes. The device’s operating system provides isolation and hardware-backed encryption.

A browser wallet setup must account for additional risks. First, the user must verify that they are downloading the correct extension from the correct source. Phishing remains a common attack: a fake extension with a similar name can be placed in a third-party extension store or promoted through a sponsored search result. The wallet extension should be downloaded directly from the official repository, verified through the developer’s published signature or checksum, and the developer’s website should be accessed through HTTPS with a validated certificate. A moment spent verifying the extension’s official link can prevent installing malware designed to steal the recovery phrase or approve unauthorized transactions.

Second, the browser profile used for the wallet should be treated as a security boundary. If the browser profile is also used for banking, email with password-reset privileges, or social media accounts that could be used to recover other accounts, a compromise of that profile affects everything. Ideally, the wallet browser profile should be separate from the browsing profile used for daily work. Password managers should not fill credentials in the wallet browser. Notifications and permission requests should be reviewed carefully—a script that requests permission to “read and modify all website data” should raise immediate concern when the wallet is not actively using it.

Third, the user should establish a routine for backup testing that does not require importing the recovery phrase into a live browser environment. To test whether a recovery phrase restores the wallet correctly, create a temporary browser profile, install the extension, import the recovery phrase, verify that the addresses match, and then delete the profile. This confirms the backup is usable without exposing the phrase to the main browser environment for extended periods.

Multi-device synchronization and the loss of mobile isolation

A mobile wallet typically stores keys on one device. If the user wants to access the same funds from a desktop, they must use the same recovery phrase in two different wallets—or sync the data some other way. This creates an explicit choice point. The user must consciously decide whether to export the seed phrase, what conditions warrant accessing the funds from multiple devices, and what security measures apply to each location.

A browser extension encourages a different workflow. The user can install the same extension in multiple browsers, on multiple devices, or in multiple profiles. Browser sync can carry credentials and some data across devices automatically. The mental model shifts from “I have a mobile wallet and a desktop wallet” to “I have one wallet accessible from multiple places.” This convenience comes with a hidden complexity: the security of the wallet is now as weak as the least-secure device on which it is installed.

If the user installs the wallet extension on a work laptop, a personal desktop, and a tablet, and if one of those devices is compromised by malware, the attacker may be able to extract the encrypted seed phrase from the extension’s local storage or inject code that steals credentials as the user unlocks the wallet. The wallet’s non-custodial design means each device must hold the keys—there is no central server to compromise instead. Multi-device access is therefore a security trade-off: greater convenience in exchange for more attack surface. Users should limit the number of devices where the wallet is installed, prioritize security hardening on those devices, and ensure that each one has up-to-date operating-system patches, antivirus software, and a strong firewall.

Recovery is also more complex. If one device is lost or compromised, the user should assume the seed phrase may be exposed. This means changing the password or PIN used to encrypt it within the extension, and if there is any doubt, moving the funds to a new wallet generated from a fresh recovery phrase. The funds themselves are not lost—they are stored on the blockchain—but controlling them requires that the recovery phrase remain private. A mobile wallet user follows the same procedure, but it is simpler to remember: one phone, one place, one recovery phrase. A browser wallet user must track where the wallet is installed and which devices might have been compromised.

Non-custodial design does not mean you can recover from user error alone

The defining feature of a non-custodial wallet is that no service provider holds the private keys. Cake Wallet’s design emphasizes this: password protection, PIN control, and encrypted seed phrase storage are all managed locally on the device. The wallet never transmits keys to a server. This is genuinely different from a centralized exchange or custodian, where a company holds the keys and the user relies on the company’s security practices.

However, non-custodial does not mean recovery is simple. If a user forgets the PIN protecting the extension, the only path to recovery is importing from the recovery phrase. If the recovery phrase is lost, the funds are lost—no support team can restore it. Unlike a mobile banking application that ties account access to identity verification, a wallet extension uses only the password and recovery phrase. Users accustomed to mobile banking’s account-recovery flows should not expect similar convenience.

This is actually a feature from a privacy perspective: no recovery process that requires identity verification also means no centralized record of who owns what. But it places full responsibility on the user. Before installing a browser wallet extension, the user should have a tested backup strategy. Write the recovery phrase down on paper, store it in a fireproof safe, test that the phrase works by importing it into a fresh profile in a sandboxed environment, and verify that the restored wallet shows the same addresses and balance. Only then should the user consider the backup complete.

Users who lose the recovery phrase after installing the extension through a cake wallet download and transferring funds to it have no recourse. The wallet will not provide a recovery code or account reset. This is not a limitation of Cake Wallet specifically; it is inherent to non-custodial design. The trade-off is absolute: complete control of the keys in exchange for absolute responsibility for the backup. Users who prefer the security of a recovery process managed by a company should use a custodial service, accepting custody risk as a trade-off for that convenience.

Browser wallets and Web3 connectivity create new approval risks

One major advantage of a browser wallet extension is integration with decentralized applications and Web3 services. A user can connect the wallet to an NFT marketplace, a decentralized exchange, or a staking application with a single click. The extension injects itself into the webpage, and the dApp can request transaction approvals or signatures from the user’s wallet.

This integration model is more convenient than the mobile alternative—on a phone, connecting to a Web3 service might require copy-pasting an address or scanning a QR code. But the browser context also creates new risks. When a dApp requests approval to spend tokens or transfer NFTs, the browser wallet displays a confirmation dialog. A visual spoofing attack can make that dialog appear to be from one dApp when it is actually initiated by another. An attacker’s website can simulate the wallet’s UI and prompt the user to confirm a transaction that sends funds to the attacker’s address.

Protecting against this requires careful attention before approving any transaction. The user should pause and verify several details: the name of the requesting website or dApp shown in the confirmation dialog, the destination address (comparing it to the legitimate address if possible), the amount being transferred, and any fee. If anything looks unfamiliar, cancel immediately. Browser wallet users should also be extremely cautious about granting unlimited approval tokens. Many dApps request permission to spend “unlimited” tokens on behalf of the user, to avoid repeated approvals. This is convenient, but it means if that dApp is hacked or acts maliciously, the attacker can drain the user’s balance of that token without a second approval prompt.

Better practice is to approve only the amount needed for the immediate transaction, or to use a token approval management tool that lets the user review and revoke permissions afterward. Advanced users may maintain separate browser profiles or wallets for high-risk versus low-risk activities: one for NFT trading on verified marketplaces, another for exploring experimental protocols. A single compromised wallet approval does not then affect the entire portfolio.

Migration from mobile requires explicit steps and new habits

Users moving from a mobile wallet to a browser extension should not treat it as a simple export-and-import. The process should be deliberate and introduce no new risk. Start by generating a new recovery phrase within the browser extension—do not export the existing phrase from the mobile wallet to use in the browser. Instead, use the browser wallet to create a fresh address set, then transfer the funds from the mobile wallet to the new browser wallet address in one or more transactions. This way, the mobile recovery phrase remains secure offline, and the browser wallet uses a distinct recovery phrase managed separately.

If the user wants to maintain access to the same funds from both the mobile and browser wallet, importing the recovery phrase is necessary—but this should be done only if both devices can be kept secure. On a phone, the mobile wallet remains isolated. The browser extension shares the desktop environment with email, web browsing, and potentially compromised software. The risk is not balanced. A more secure approach is to keep the main funds on a mobile wallet and use a smaller amount in the browser wallet for dApp interaction and quick transfers.

Documentation for the wallet extension should be reviewed before setup. Cake Wallet emphasizes non-custodial design and local-only key storage, but users should verify that they understand what this means operationally. Password and PIN protection are applied to the extension; the underlying cryptographic keys are stored encrypted locally. The zero personal data collection policy is strong privacy protection, but it also means there is no account recovery or customer support pathway if the user locks themselves out of the extension.

After successful setup and backup testing, establish a regular maintenance routine. Update the browser and the extension when patches are available. Review the list of browser extensions and remove any that are no longer used. Run antivirus software and check for browser hijacking or malicious extensions quarterly. These habits are not specific to a cryptocurrency wallet—they apply to any security-critical software running in a browser. The wallet simply raises the stakes because loss of access or key exposure means loss of funds with no recourse.

Evaluating whether a browser wallet is right for your workflow

A browser wallet is appropriate for users who prioritize accessibility and regular transaction activity. If the user trades actively, interacts with dApps, or manages NFTs, the one-click approval and multi-chain support make a browser wallet convenient. If the user keeps a large balance they intend not to touch for months, a mobile wallet or hardware device is more appropriate. The risk-reward calculation is different for different use cases.

For a user who already manages crypto on a mobile wallet and is considering a cake wallet download as a second wallet, the answer depends on how much they value Web3 integration. If they want to trade on decentralized exchanges, participate in DeFi, or interact with NFT marketplaces without constantly switching devices, a browser wallet is worth the security overhead. If they only use the wallet to receive payments and store funds, maintaining a mobile-only setup is simpler and safer.

The security mindset shift is the key. Mobile users tend to think of “protecting the phone” as the main security task. Browser wallet users must think of “protecting the device, the browser, the profile, the password, and the physical backup” as an integrated system. One weak point—a shared work laptop, a password written in notes, a recovery phrase photographed and cloud-synced—can compromise the entire wallet. Users who cannot commit to this more rigorous approach should acknowledge that limitation and choose wallet software matched to the security practices they will actually follow. Sophisticated tools create sophisticated responsibilities. The most important security choice is matching the tool to the threat model and the user’s operational discipline.

Frequently asked questions

Is a browser wallet extension as secure as a mobile wallet?

No, but for different reasons. A mobile wallet benefits from OS-level isolation and hardware-backed encryption, while a browser wallet shares a security context with multiple extensions and websites. However, mobile wallets require physical security of the phone. The “more secure” choice depends on the threat model. A browser wallet may be more vulnerable to malware, while a mobile wallet is more vulnerable to physical theft or loss. Both are non-custodial, meaning the user, not a service provider, controls the keys.

Should I install the same browser wallet on multiple devices?

It is possible, but it increases risk. Each device where the wallet is installed becomes a potential attack surface. If you do install on multiple devices, prioritize security hardening on each one: keep the operating system and browser updated, use strong passwords and PINs, and maintain the recovery phrase offline, not synced across devices. For large balances, consider keeping the wallet on one device only and using a separate application for occasional access.

What should I do if I forget the password or PIN protecting my browser wallet extension?

The only way to regain access is to import the recovery phrase into a fresh instance of the wallet. If the recovery phrase is also lost, the funds cannot be recovered—no support team or account recovery process exists. This is why a tested backup stored offline is essential before transferring any funds to a new browser wallet. Non-custodial design means users have complete control, but also complete responsibility for recovery information.

Can I transfer funds from my mobile wallet to a browser wallet safely?

Yes. Create a new recovery phrase within the browser wallet, generate an address, and send funds from the mobile wallet to that address in a test transaction first. Verify the receiving address is correct and the funds arrive, then send the remaining balance. Keep both recovery phrases secure offline, and do not export the mobile phrase to the browser environment. Maintaining separate recovery phrases reduces the risk if one device is compromised.

Ledger hardware wallet setup interface showing recovery phrase entry and device confirmation steps

Ledger Wallet Extension for Beginners: Common Setup Mistakes and How to Avoid Them

New users purchasing a Ledger hardware wallet often assume that installation is straightforward: unbox the device, download the companion application, and begin managing cryptocurrency. In practice, the setup process has multiple decision points where a single error can create months of confusion, unnecessary fund transfers, or forgotten backup information. The Ledger wallet extension provides the interface between your secure hardware and the blockchain networks you wish to access, but that interface depends entirely on correct initialization and ongoing attention to the details that most beginners overlook.

The most costly mistakes are not dramatic hacks or stolen devices. They are preventable errors made during the first hour: writing down the recovery phrase incorrectly, misunderstanding which password protects what, creating accounts on the wrong network, or installing software from an unreliable source. A second category of mistakes emerges weeks or months later when a user tries to move funds between addresses, interact with a decentralized application, or reconnect after updating the device firmware. This article identifies the most frequent setup errors, explains why they matter, and provides a checklist to prevent them from the start.

Ledger hardware wallet setup interface showing recovery phrase entry and device confirmation steps

Confusing the recovery phrase, PIN, and passphrase

The single most common setup error is misunderstanding the three separate secrets that control access to funds. The recovery phrase (also called a seed phrase) is a list of 12 or 24 words generated by the hardware device. This phrase is the master key to all accounts associated with your Ledger device. The PIN is a four-digit code that you create during device setup; it protects the device itself and must be entered each time you use it. A passphrase is an optional additional security layer that creates a completely separate set of accounts derived from your recovery phrase.

Beginners frequently confuse these three elements during wallet setup. A user might write down the PIN thinking it is the recovery phrase, or assume that the Ledger wallet extension password is the same as the device PIN. These errors can cause irrecoverable loss. If you lose the 12 or 24 word recovery phrase and cannot locate a written copy, you lose access to all funds on all accounts created from that device, even if the device itself is intact. If you forget the PIN, you can reset the device and recover it using the recovery phrase, but only if you have that phrase written down correctly and stored safely.

The passphrase is the most misunderstood of the three. It is entirely optional, and if you enable it, the same recovery phrase will generate a completely different set of accounts. This is useful for advanced users who want to segregate funds—for example, keeping everyday spending money in one account and larger holdings in a separate account protected by a longer passphrase. For beginners, a passphrase is often a source of confusion because it is easy to forget you enabled it, create accounts without it, and then believe your funds are lost when they are simply in a different account derived from the same phrase.

The correct setup sequence is to write down the recovery phrase word by word as the device displays it, store that phrase in a safe location (never on a computer or phone), set your PIN to something you will remember but others cannot guess, and leave the passphrase disabled unless you have a specific reason to use it. Verify your recovery phrase before leaving the setup screen; if you have written it incorrectly, the device will catch the error.

Installing the ledger wallet extension from the wrong source

The Ledger wallet extension is a desktop browser add-on that allows you to interact with your hardware device from your computer. It is available for Chrome, Firefox, Edge, and Brave, and it is one of the highest-value targets for phishing and counterfeit distribution. A user searching “Ledger wallet extension download” may land on a page that looks nearly identical to the official Ledger site but is actually a clone hosted on a different domain. The counterfeit extension can capture private information, redirect transactions to attacker-controlled addresses, or modify transaction details before you sign them on your device.

Beginners often do not realize that a browser extension, even one that looks legitimate, can access all information you type into the browser and can intercept data before it reaches your hardware device. The official ledger wallet extension from Ledger cannot access private keys because the hardware device retains them, but a fraudulent extension can still intercept recovery phrases if you type them anywhere, record transactions you are about to sign, or hijack the browser connection to your device.

The safest installation procedure is to navigate directly to the official Ledger website, verify the URL in your browser (it should be ledger.com or a verified Ledger domain), and install the extension from the official browser extension store (Chrome Web Store, Firefox Add-ons, etc.) only. Do not click links from email, social media, or search results that claim to direct you to the extension download. Once installed, verify the extension name and publisher in your browser’s extension management page. The official ledger wallet extension will clearly display Ledger as the publisher and will match the exact name shown on the official website.

If you have already installed an extension and are uncertain whether it is legitimate, uninstall it immediately. Then clear your browser cache and cookies, update your device firmware and the Ledger Live application to the latest version, and verify that your funds are still in the correct accounts. Do not assume that using the device PIN protects you if the extension was compromised; an attacker with access to the extension can see what you are signing before you approve it on the hardware device.

Neglecting to back up and test the recovery phrase

Ledger devices generate the recovery phrase in a way that makes it mathematically certain to work. If you have written it down correctly and stored it safely, you can recover all accounts from that phrase on a new device or with recovery software. The critical step that beginners skip is testing the backup before they move substantial funds.

The proper backup procedure is to write down each word of the recovery phrase as it appears on the device screen, verify each word against the screen display before moving to the next one, and store the written copy in a secure location such as a safe deposit box, home safe, or steel backup sheet designed for seed phrases. Do not photograph the phrase, do not type it into a text document, and do not read it aloud to someone else. Once you have the written backup, consider testing it by creating a second Ledger device with the same recovery phrase and verifying that both devices generate the same accounts. This test proves that you have written the phrase correctly without creating a permanent digital copy.

Many beginners skip this test because they assume that if the device works once, the backup must be correct. In reality, a user might transpose two words, write a word in a way that is ambiguous (such as confusing “0” and “O” or “1” and “l”), or fail to write down a word at all. These errors become obvious only when you try to restore from the backup. If you discover the error months later when you actually need to recover, it may be impossible to determine which word is wrong among thousands of possibilities. Testing the backup by restoring it to a spare device (or to a software wallet if you do not have a spare hardware device) takes 30 minutes and prevents catastrophic loss.

Creating accounts on the wrong blockchain network

A Ledger device can manage accounts on multiple blockchain networks—Bitcoin, Ethereum, Solana, Polygon, and many others. The wallet setup process involves selecting which networks you want to manage and creating an account for each one. A common mistake is creating an account on the wrong network or becoming confused about which account holds which type of asset.

For example, a beginner might create an Ethereum account and then try to send Bitcoin to the Ethereum address. Bitcoin sent to an Ethereum address on the Ledger device will be permanently lost because the Bitcoin network does not recognize Ethereum addresses. Similarly, a user might create an account on the Ethereum mainnet, later accidentally create a duplicate account on the Ethereum testnet (which is used for testing and has no real value), and become confused about which account has the funds.

The Ledger wallet extension displays the blockchain network for each account at the top of the screen when you select it. Before sending funds to any address, verify three pieces of information: the type of cryptocurrency (Bitcoin, Ethereum, etc.), the blockchain network (mainnet, testnet, Layer 2 network such as Polygon), and the specific account number within your Ledger device. If you are unsure, send a small test amount first and confirm that it arrives in the correct account before sending larger amounts.

For users managing multiple accounts, a common organization mistake is not labeling them clearly. The Ledger wallet extension allows you to rename each account with a custom label, and beginners should do this immediately after creating the account. Instead of generic names like “Account 1” and “Account 2,” use descriptive labels such as “Bitcoin savings” or “Ethereum trading.” This reduces the risk of accidentally sending funds to the wrong account.

Mishandling the initial connection between device and wallet extension

The first time you connect a new Ledger device to the Ledger wallet extension, the setup wizard guides you through several steps: naming the device, verifying that the device displays the same name on its screen, connecting to a blockchain node, and selecting the networks you want to manage. Beginners often rush through this process without understanding what each step accomplishes, which leads to confusion later.

One frequent error is not completing the “verify device name” step, which asks you to confirm that the name displayed on your computer screen matches the name shown on the device itself. This verification proves that your device is actually connected to your computer and that you are not being tricked by a software counterfeit or network attack. If the device does not display the expected name, disconnect immediately; this usually indicates a problem with the connection, but it could also indicate that you are connected to someone else’s device or a spoofed device.

Another error is failing to select all the blockchain networks you plan to use during initial setup. The wallet extension can work with most blockchain networks, but some require additional setup steps or configuration of custom nodes. A user who plans to manage Solana tokens but does not select Solana during initial setup may become frustrated later when attempting to add Solana to the wallet and may not follow the correct procedure to add a new network. The safest approach is to select all networks you think you might use, even if you do not plan to move funds to them immediately. You can always manage these accounts from the wallet extension without ever depositing funds into them.

The final common error during initial connection is ignoring firmware update prompts. When you first connect a new Ledger device, the wallet extension usually prompts you to update the device firmware to the latest version. Beginners often skip this step to get started faster, but using outdated firmware can expose you to known vulnerabilities and can prevent you from using new features or newer versions of the wallet extension itself. Always update the firmware before moving substantial funds to the device. The update process takes 10–15 minutes and requires your device to remain connected to your computer without interruption.

Assuming security ends at the hardware device

A Ledger hardware wallet stores private keys in a secure element that is nearly impossible to compromise, and the device itself uses a secure operating system. Many beginners interpret this to mean that they can relax all other security practices because the hardware is “unhackable.” This assumption leads to careless behavior that undermines the security of the hardware itself.

If you store your recovery phrase in a location where someone can find it—such as a desk drawer, a notebook near your computer, or a photo on your phone—the hardware security becomes irrelevant. An attacker with your recovery phrase can restore your wallet on a different device and transfer all funds without ever touching your original hardware device. Similarly, if your computer is compromised by malware, that malware cannot steal private keys from the device, but it can read your recovery phrase if you have typed it anywhere, modify transaction details before you sign them, or trick you into signing transactions you do not intend to approve.

The three-layer security model of Ledger—secure hardware, secure operating system, and wallet extension—remains secure only if all three layers are treated as important. Keep your recovery phrase written on paper and stored in a safe location. Keep your computer updated with the latest security patches and antivirus software. Use your Ledger wallet extension only to manage your own devices and accounts, not to sign transactions on behalf of others unless you fully understand the implications. Verify transaction details on your device screen before confirming any transaction, because this is your opportunity to catch any fraud perpetrated through a compromised computer or browser.

Forgetting to manage and organize multiple accounts

As a Ledger user gains confidence, they often create multiple accounts for different purposes: savings, trading, spending, or separate cryptocurrencies. This is one of the strengths of hardware wallet architecture, but it also creates a management challenge that beginners do not anticipate.

Without a clear organizational system, a user can easily forget where they stored funds, create duplicate accounts, or send money to an account they believed was empty. The Ledger wallet extension provides account labels, but only if users actively create them. A user with ten accounts in the wallet, none of which are labeled, will struggle to locate funds or to understand their total balance across all accounts. The solution is to establish a labeling convention before creating multiple accounts: for example, “BTC-long-term,” “ETH-trading,” or “SOL-spending.” Update these labels immediately after creating each account, not weeks later when you have forgotten the purpose of each account.

Another management mistake is not keeping a separate inventory of accounts and their purposes. A simple spreadsheet or document stored securely (such as in an encrypted password manager) can record the account name, the blockchain network, the purpose of the account, the date it was created, and the approximate balance. This record should not include recovery phrases or private keys, but it should be sufficient to quickly locate funds if you have not accessed a particular account in months.

For advanced users, the option to use a passphrase creates an additional layer of account organization. However, beginners should avoid passphrases until they have mastered basic multi-account management. A passphrase is easy to forget, easy to mistype, and can create a situation where you believe funds are lost when they are actually in a separate account that you cannot access with your normal PIN and passphrase combination.

Moving forward: a setup checklist for new Ledger users

The most effective way to avoid setup mistakes is to follow a checklist that covers all critical steps before moving significant funds to your device. This checklist should be completed in order, with each step verified before moving to the next one.

First, purchase your Ledger device from an authorized retailer or directly from Ledger’s official website. Verify that the device is genuine using Ledger’s authentication instructions. Second, unbox the device and verify that it is sealed and undamaged. Third, update the device firmware to the latest version using the Ledger Live application on your computer or mobile device. Fourth, initialize the device, which generates a new recovery phrase. Write down the phrase word by word, verify it against the device screen, and store the written copy in a safe location. Fifth, set your device PIN to a four-digit code you will remember. Sixth, do not enable a passphrase unless you have a specific reason to do so. Seventh, install the Ledger wallet extension from the official browser extension store, and verify the publisher and name. Eighth, connect your device to the wallet extension and complete the setup wizard. Ninth, select all blockchain networks you might use. Tenth, create and label at least one account for each network, using descriptive names. Eleventh, do not send large amounts of funds to your device until you have completed steps 12 and 13. Twelfth, perform a test restore of your recovery phrase on a separate Ledger device or software wallet to verify that you have written it correctly. Thirteenth, practice sending and receiving small amounts of cryptocurrency to each account to ensure you understand the process before moving large amounts.

Following this checklist takes two to four hours, but it prevents the vast majority of setup mistakes that plague beginners. The time invested in careful setup is far less costly than the time lost recovering from a critical error such as a lost recovery phrase or funds sent to the wrong address.

Frequently asked questions

What should I do if I lose my recovery phrase?

If you have lost your written recovery phrase and have not stored it anywhere else, funds on your Ledger device are irrecoverable unless you remember the passphrase you enabled during setup (which most beginners have not). The only way to prevent this situation is to test your recovery phrase backup by restoring it to a second device or software wallet before you move significant funds. If you have not yet moved large amounts and you realize your backup is lost or incorrect, reset the device and generate a new recovery phrase, then store that phrase more carefully.

Can I recover my funds if I forget my device PIN?

Yes. If you forget your device PIN, you can reset the device by entering the wrong PIN three times. The device will then ask you to restore from your recovery phrase. If you have written down your recovery phrase correctly and stored it safely, you can use it to recover all accounts and set a new PIN. This is why the recovery phrase is called the “master key”—it allows you to recover access to your device and all accounts even if you forget the PIN.

Is it safe to use the ledger wallet extension on a shared computer?

It is safer than storing cryptocurrency in a software wallet on a shared computer, because your private keys remain on the hardware device. However, the ledger wallet extension can still be intercepted or compromised by malware if the computer is already infected. For maximum security, use your Ledger device only on a computer that you control exclusively, that you keep updated with security patches, and that you do not use for risky activities such as visiting untrusted websites or opening suspicious email attachments. If you must use a shared computer, ensure that each user has a separate login account and that you sign out of all applications before leaving the computer.