Mirax Review and Player Reputation in Canada

Mirax Review and Player Reputation in Canada

This research article examines what the supplied records establish about Mirax for Canadian readers. The focus is narrow: brand identity, regulatory documentation, the Canadian search-market picture, and the way a reader should interpret the available evidence about player reputation. It is not a personal playing account, a legal opinion, or a guarantee of current operating conditions.

Research question

The question is: what can the retained research records support about Mirax’s identity, Canadian market positioning, documented regulatory framework, and player-reputation evidence?

Mirax Review and Player Reputation in Canada

The answer requires separating different kinds of information. A corporate or licensing record can describe an operating structure. A search-visibility observation can describe where a brand appears in the Canadian search landscape. Neither type of record, by itself, establishes that every player has had the same experience or that all operating conditions remain unchanged.

Method and evaluation criteria

The review uses only the supplied research dossier, with a verification timestamp of September 2, 2026 and a report publication timestamp of September 2026. The retained research describes the work as independent analysis involving empirical fact-checking, technical auditing, and compliance verification. That description is itself treated as a statement from the stored research, rather than as an independently tested conclusion in this article.

Four criteria guide the assessment:

  • Identity: whether the records describe the brand’s platform and corporate lineage clearly.
  • Regulatory documentation: what the retained licensing record reports, without converting that observation into a broader legal conclusion for every Canadian province.
  • Canadian visibility: what the stored search-landscape analysis reports about the brand’s presence.
  • Reputation evidence: whether the dossier supplies player-level evidence that can support a general reputation judgment.

This method gives greater weight to direct documentation and keeps attributed research notes separate from independently established findings. It also treats silence carefully: where the selected records do not establish a point, the article does not infer the answer.

What the records say about Mirax’s identity

The retained brand-identity research reports that Mirax Casino was established in 2022 and operates as a hybrid fiat-cryptocurrency iGaming platform developed on the SoftSwiss turnkey casino engine. The same record states that the brand was initially brought to market under Hollycorn N.V. and later transitioned its direct operating licensee to Scores55 Tech B.V. The record is attributed research rather than a conclusion independently reproduced here.

A related research note describes Mirax as part of a wider corporate network within the SoftSwiss white-label and turnkey ecosystem. It reports historical alignment with Hollycorn N.V. and a current structure under Scores55 Tech B.V. This is useful for understanding that the brand’s public identity may involve more than one corporate or platform relationship. It does not, however, establish that every related site has identical policies, ownership, player support, or operating conditions.

The dossier also reports that the primary operating entity and licence holder is Scores55 Tech B.V. The supplied extract does not provide the complete company registration number in the retained wording available here, so this article does not reconstruct or supplement it.

What the licensing record establishes

The retained licensing note states that Mirax Casino operates under the regulatory supervision of the Curaçao Gaming Authority and reports a commercial gaming licence, OGL/2024/1307/0748, issued to Scores55 Tech B.V. The source named in the record is the Curaçao Gaming Authority’s Official Online Gaming License Registry, with the stored research identifying the registry as a 2025 source.

This is a documented licensing observation about the named operator and licence. It should not be expanded into a universal statement that Mirax is authorised in every Canadian province. The dossier’s Canadian regulatory note places the service within the framework governing offshore remote gaming under federal and provincial statutes, but the supplied wording does not provide a province-by-province authorization finding that would support a broader conclusion.

For a Canadian reader, this distinction matters. A Curaçao licence and a Canadian provincial authorization are different questions. The retained records establish that the research identified a Curaçao licence record. They do not, within the selected evidence, establish a current provincial registration or operating agreement for Ontario, British Columbia, Alberta, Quebec, Manitoba, Nova Scotia, or another specific Canadian jurisdiction.

Canadian search visibility and what it means

The Canadian search-landscape analysis reports high-density organic visibility for Mirax in non-regulated provincial grey-market contexts, specifically British Columbia, Alberta, Quebec, Manitoba, and Nova Scotia. This is a research note about brand recognition and search presence in September 2026.

Search visibility can help explain why Canadian readers encounter a brand. It is not the same as regulatory approval, customer satisfaction, or proof of reliable performance. The stored observation therefore supports a conclusion about discoverability, not a conclusion about player reputation. It also should not be read as evidence that all Canadian provinces treat the brand in the same way.

The term “grey market” is retained here because it appears in the supplied Canadian search analysis. It is not being used as a new legal classification created by this article. The dossier does not provide a complete province-by-province legal determination, so the article does not supply one.

Player reputation: what can and cannot be concluded

The selected records do not provide a sufficiently detailed body of player reviews, complaint statistics, independently verified withdrawal histories, or a representative survey from which to calculate a general player-reputation score. Accordingly, the supplied evidence does not establish whether Mirax has a positive, negative, or mixed reputation among Canadian players as a whole.

This limitation is central to the review. Corporate lineage, licensing documentation, and search visibility are not substitutes for player-level evidence. They can describe the setting in which a reader encounters the brand, but they do not show how a typical account holder experienced registration, play, account management, or support.

The dossier does report that formal player complaints and alternative dispute resolution follow procedures described in Section 19 of the General Terms and Conditions. It also reports that the terms document is Version 2.7, updated February 25, 2026, and that compliance documentation is described in the AML/KYC and Privacy Policy materials. These records establish the existence of documented policy and escalation references as reported by the stored research. They do not establish how often disputes occur, how they are resolved, or whether players generally regard the process favourably.

Policies and responsible-gaming documentation

The retained policy research reports that Mirax maintains publicly accessible, timestamped documentation on its primary domain. It identifies the General Terms and Conditions, the AML/KYC Policy, and the Privacy Policy as parts of the stated legal and compliance framework. The research also reports a dedicated Responsible Gaming Policy containing player-protection and self-limitation tools.

These records support a documentation finding: the stored research located named policy materials and identified their stated functions. They do not independently establish that the policies are complete, that every provision is applied consistently, or that a reader’s individual circumstances will be handled in a particular way.

A beginner should therefore distinguish between “a policy is documented” and “the policy guarantees a particular outcome.” The supplied evidence supports the first formulation when attributed to the research. It does not support the second.

How to read the evidence without overclaiming

Several common interpretations would go beyond the dossier:

  • A listed Curaçao licence should not be treated as proof of authorization across Canada.
  • Search prominence should not be treated as proof of trust, popularity, or player satisfaction.
  • A documented complaint procedure should not be treated as evidence that complaints are rare or resolved successfully.
  • A named policy should not be treated as proof of practical outcomes for every account holder.
  • A corporate relationship within a turnkey network should not be treated as proof that affiliated brands share identical conditions.

These are evidence boundaries, not additional allegations about Mirax. They explain why the research can describe documentation and market visibility while remaining unable to assign a reliable overall reputation.

Limitations and uncertainty

The principal limitation is the scope of the retained material. It contains research notes about identity, licensing, corporate structure, Canadian search visibility, policy documentation, dispute procedures, and the report’s verification date. It does not supply a statistically representative player survey or a validated reputation index.

The licensing and regulatory material is also attribution-sensitive. The dossier reports the licence and describes the Canadian offshore-gaming framework, but those observations are not converted here into a definitive province-wide legal judgment. The same caution applies to market language: the search analysis reports grey-market penetration in named provinces, but it does not establish a single legal status for all Canadian readers.

Finally, the records are time-bound. The stored research says that its operational policies, regulatory filings, banking rails, and bonus conditions were verified as of September 2, 2026. This article does not add or update any of those categories. A later reader should understand the findings as a dated research snapshot rather than a permanent description.

Conclusion

The supplied evidence supports a clear but limited profile of Mirax. The stored research describes a 2022-established hybrid fiat-cryptocurrency iGaming brand built on the SoftSwiss turnkey casino engine, with historical ties to Hollycorn N.V. and a current operating structure reported under Scores55 Tech B.V. It also reports a Curaçao Gaming Authority licence record and significant search visibility in several Canadian provincial grey-market contexts.

In the neutral profile of Mirax, the retained record describes Mirax as a brand established in 2022.

The evidence status is weaker for player reputation. The dossier identifies formal terms, compliance policies, responsible-gaming documentation, and an outlined dispute process, but it does not establish a representative Canadian player verdict. The most defensible conclusion is therefore not that Mirax has a particular reputation, but that the available records document its stated structure and policies more clearly than they measure player experience.

What method was used for this Mirax review?

The review compares only the supplied research records, using identity, regulatory documentation, Canadian search visibility, policy documentation, and player-reputation evidence as separate criteria. It preserves attributed statements and does not treat missing information as proof of absence.

Does the retained research establish a general Canadian player reputation for Mirax?

No. The supplied records do not provide a representative player survey, a validated reputation index, or enough player-level evidence to establish a positive, negative, or mixed reputation for Canadian players as a whole.

What does the licensing evidence establish?

The retained licensing note reports Curaçao Gaming Authority supervision and identifies commercial gaming licence OGL/2024/1307/0748 as issued to Scores55 Tech B.V. It does not establish a current authorization finding for every Canadian province.

What does Mirax’s Canadian search visibility show?

The stored search analysis reports high-density visibility in British Columbia, Alberta, Quebec, Manitoba, and Nova Scotia. That establishes a research observation about discoverability, not proof of player satisfaction, regulatory approval, or overall trust.

Jeigaenlinea bonos y promociones en Chile: qué permiten establecer los registros

Jeigaenlinea bonos y promociones en Chile: qué permiten establecer los registros

Pregunta de investigación y alcance

Este análisis examina qué información documentada existe sobre los bonos y las promociones asociados con Jeigaenlinea para el mercado chileno. La pregunta no es si una oferta concreta resulta conveniente ni si una promoción está disponible actualmente, sino qué puede establecerse con seguridad a partir de los registros conservados.

El término de búsqueda «Jeigaenlinea Casino Casino» aparece en la nota de desambiguación como un error ortográfico y una duplicación nominal de la marca de apuestas y juegos de azar digital «Juegaenlinea». Esa misma nota identifica variantes comerciales como Juega en Línea, JEL Casino y el portal territorializado juegaenlineachile.com. Por ello, el análisis utiliza Jeigaenlinea como referencia editorial, pero atribuye los datos a los registros sobre Juegaenlinea y no trata todas las variantes como entidades separadas.

Jeigaenlinea bonos y promociones en Chile: qué permiten establecer los registros

El alcance geográfico es Chile. Cuando un registro describe Curazao como jurisdicción de licencia o menciona una estructura corporativa internacional, ese dato se conserva como contexto de origen de la plataforma y no se transforma en una conclusión sobre autorización chilena.

Método y criterios de evaluación

Se revisó únicamente el expediente documental suministrado para esta investigación. La selección priorizó cinco registros directamente relacionados con promociones, condiciones de uso, privacidad, verificación y protección del usuario. También se consideró el registro sobre la situación regulatoria chilena, porque el significado práctico de cualquier bono depende del marco aplicable al usuario del país.

La evaluación siguió cuatro criterios:

  • Identificación: distinguir la marca objeto del análisis de errores ortográficos y variantes nominales.
  • Contenido promocional: comprobar qué afirma expresamente el expediente sobre bonos, promociones y condiciones de contratación.
  • Verificabilidad: separar la existencia de una sección o política de la disponibilidad, valor o vigencia de una oferta concreta.
  • Contexto jurídico y de protección: interpretar la información sobre licencia, reclamaciones, privacidad, verificación y juego responsable sin convertir observaciones atribuidas en conclusiones propias.

El criterio central es la fuerza de la evidencia. Los registros seleccionados son notas de investigación atribuidas: informan lo que recoge el expediente, pero no equivalen por sí solos a una auditoría independiente, una confirmación de disponibilidad en tiempo real ni una decisión de una autoridad chilena.

Qué documentan los registros sobre bonos y promociones

El registro sobre términos y políticas afirma que los términos legales, las condiciones de contratación y los reglamentos de promociones de Juegaenlinea establecen los derechos y obligaciones de los usuarios al utilizar sus productos en Chile. Esta formulación permite identificar la existencia de un marco documental para las promociones. No aporta, sin embargo, el valor de un bono, una fecha de vigencia, los requisitos de una oferta ni la confirmación de que una promoción específica esté disponible para todos los usuarios chilenos.

La diferencia es importante para una comparación seria. Que exista un reglamento de promociones no demuestra que todas las ofertas anunciadas sean intercambiables, permanentes o aplicables a cada cuenta. Tampoco autoriza a presentar una promoción como garantizada. El expediente no suministra cifras, porcentajes, límites, requisitos de apuesta, plazos ni condiciones particulares de una campaña concreta.

En consecuencia, la evidencia disponible sirve para evaluar la presencia de reglas contractuales, no para construir una tabla de ofertas. Una ficha que incluyera importes o beneficios específicos excedería el material retenido.

Condiciones contractuales, reclamaciones y verificación

El registro sobre resolución alternativa de disputas señala que el marco contractual para reclamaciones de saldo y resolución alternativa de disputas está detallado en los Términos y Condiciones Generales, mediante una cláusula de resolución de conflictos. Para el análisis de bonos, esta información es relevante porque indica dónde se ubica el mecanismo contractual aplicable a controversias sobre saldos o condiciones.

El mismo dato debe interpretarse con precisión. Que una cláusula de resolución de conflictos esté descrita en los términos no significa que el expediente haya comprobado el resultado de una reclamación, la eficacia práctica del procedimiento o la recuperación de un saldo. Los registros tampoco presentan una experiencia de usuario, una resolución individual ni una auditoría externa del mecanismo.

La nota sobre la política de prevención del lavado de dinero y Conozca a su Cliente describe esas políticas como un pilar obligatorio dentro del marco de Curazao. Para esta investigación, el dato indica que el expediente reconoce una política de cumplimiento vinculada con la plataforma. No establece cuáles son los requisitos concretos aplicables a cada persona, en qué momento se activarían ni cómo afectarían a una promoción determinada. Esas cuestiones no están especificadas en los registros suministrados.

Privacidad, seguridad y protección del usuario

El expediente indica que la gestión de datos personales y la seguridad criptográfica de Juegaenlinea se rigen por el Aviso de Privacidad y Seguridad institucional de Trickless N.V. Este punto aporta un criterio documental adicional: una persona que estudie una promoción no debería leer únicamente el beneficio anunciado, sino también revisar el marco de privacidad asociado a la cuenta.

La afirmación anterior se mantiene en el nivel que permite la fuente. El registro no presenta una prueba técnica independiente de la criptografía, una certificación de seguridad ni los resultados de una evaluación de protección de datos. Por ello, no corresponde convertir la existencia de un aviso institucional en una garantía de seguridad.

También se informa que la plataforma integra un apartado dedicado a la protección del usuario y a la prevención de conductas de juego compulsivo. Este registro demuestra, dentro del expediente, que existe un apartado identificado con esa finalidad. No demuestra el alcance de sus medidas, su aplicación en cada caso ni el resultado de su utilización. En un análisis de promociones, su relevancia consiste en recordar que el contenido promocional forma parte de un conjunto más amplio de políticas de usuario.

Jurisdicción de origen y contexto chileno

La nota sobre licencia atribuye la explotación comercial a Trickless N.V., sociedad constituida bajo las leyes de Curazao, con Número de Registro Mercantil 160941. Otro registro atribuye a esa entidad la responsabilidad del licenciamiento y la custodia del software de juego dentro de una estructura corporativa dual orientada a la prestación técnica y al procesamiento transaccional en América Latina.

Además, el expediente identifica la licencia OGL/2024/139/0125 a nombre de Trickless N.V. y señala que los usuarios pueden consultar plataformas de supervisión del regulador de origen para verificar la validez técnica de la autorización y los canales de resolución de reclamos. Estas referencias describen la documentación de origen que aparece en los registros. No equivalen a una autorización chilena ni permiten afirmar por sí solas que una oferta sea legalmente aplicable en Chile.

El contexto regulatorio chileno se describe en el expediente como un periodo de definición legislativa e institucional. Por tanto, la presencia de una licencia de Curazao debe mantenerse separada del análisis del marco chileno. Una licencia extranjera y una condición promocional publicada no resuelven, por sí mismas, la cuestión de la autorización local.

Esta distinción evita una interpretación frecuente: confundir la existencia de una referencia regulatoria extranjera con una conclusión sobre la situación jurídica en Chile. El expediente permite informar ambas piezas de contexto, pero no autoriza a fusionarlas.

Lectura comparativa de la evidencia

Desde una perspectiva comparativa, los registros ofrecen más información sobre la arquitectura documental de Jeigaenlinea que sobre el contenido económico de sus bonos. Se documentan términos y reglamentos de promociones, una cláusula de resolución de conflictos, políticas de privacidad y seguridad, medidas de verificación vinculadas con Curazao y un apartado de protección del usuario. No se documenta una oferta concreta con monto, porcentaje, fecha, límite o requisito verificable. En el perfil de Jeigaenlinea para lectores de CL, el registro describe la marca como digital de apuestas y juegos de azar.

Esto sitúa la evidencia en un nivel principalmente institucional y contractual. Es suficiente para describir qué áreas documentales deben considerarse al estudiar una promoción, pero insuficiente para clasificar ofertas por valor o para declarar cuál sería la mejor opción para un usuario chileno.

La comparación tampoco puede apoyarse en una medición de resultados. El expediente no suministra datos de aceptación de bonos, rendimiento de campañas, tiempos de resolución, experiencia general de usuarios ni auditorías independientes. Presentar cualquiera de esos aspectos como una ventaja o desventaja de Jeigaenlinea iría más allá de la evidencia retenida.

Errores de interpretación que conviene evitar

El primer error consiste en tratar el nombre de búsqueda con la duplicación «Casino Casino» como una marca independiente. La nota de desambiguación lo atribuye a un error ortográfico y nominal relacionado con Juegaenlinea.

El segundo es confundir la existencia de reglamentos con la disponibilidad de una promoción. El registro sobre términos confirma que se describen derechos, obligaciones y reglas promocionales, pero no aporta el contenido de una campaña concreta.

El tercero es convertir una referencia de licencia de Curazao en una conclusión sobre Chile. La evidencia identifica una jurisdicción y una entidad de origen; el propio contexto chileno se describe como sujeto a definición legislativa e institucional.

El cuarto es presentar políticas de privacidad, verificación o juego responsable como certificaciones independientes. Las notas documentan la existencia o descripción de esos apartados, pero no ofrecen una evaluación técnica o de resultados.

El quinto es interpretar la cláusula de resolución de conflictos como prueba de que una reclamación será resuelta favorablemente. El registro solo indica que el mecanismo está detallado contractualmente.

Limitaciones y grado de certeza

La principal limitación es la ausencia de datos promocionales concretos en los registros seleccionados. No se suministran importes, porcentajes, fechas de inicio o término, condiciones de liberación, límites, requisitos de elegibilidad ni confirmación de disponibilidad. Por ello, la investigación no puede responder cuánto vale un bono ni qué oferta está vigente.

Tampoco se suministra una verificación independiente de la licencia, de la seguridad criptográfica, del funcionamiento del procedimiento de reclamaciones o de la aplicación práctica de las políticas de protección del usuario. Esos puntos deben conservarse como afirmaciones atribuidas al expediente, no como resultados demostrados por esta investigación.

Finalmente, el alcance chileno requiere una separación cuidadosa entre información de origen y situación local. El expediente proporciona datos sobre Curazao y sobre el contexto regulatorio de Chile, pero no establece una autorización chilena específica para Jeigaenlinea ni una conclusión definitiva sobre la aplicabilidad local de una promoción.

Conclusión

Los registros permiten establecer que Juegaenlinea, identificada aquí a partir de la variante Jeigaenlinea, dispone de un marco documentado de términos, condiciones y reglamentos de promociones, junto con referencias a resolución de conflictos, privacidad, verificación y protección del usuario. También atribuyen la licencia y la estructura corporativa de origen a Trickless N.V. en Curazao.

La evidencia no permite establecer el valor ni la vigencia de un bono específico para Chile. Tampoco permite convertir la licencia extranjera en una conclusión sobre autorización chilena, ni presentar las políticas institucionales como garantías independientes. La conclusión comparativa, por tanto, es documental: el expediente describe una estructura de políticas y condiciones, pero no contiene suficiente información promocional verificable para valorar ofertas concretas.

¿Qué demuestra el expediente sobre los bonos de Jeigaenlinea?

El registro sobre términos y políticas afirma que existen condiciones de contratación y reglamentos de promociones. No suministra el importe, porcentaje, vigencia ni requisitos de una oferta concreta.

¿La licencia de Curazao confirma una autorización en Chile?

No. Los registros atribuyen la licencia de origen a Trickless N.V. en Curazao y describen el contexto chileno como sujeto a definición legislativa e institucional. El expediente no establece una autorización chilena específica.

¿Cómo deben leerse las referencias a privacidad, verificación y juego responsable?

Deben leerse como descripciones atribuidas a las políticas y apartados institucionales registrados. El expediente no aporta una auditoría independiente ni resultados que permitan tratarlos como garantías.

¿Qué papel cumple la cláusula de resolución de conflictos?

El registro indica que los Términos y Condiciones Generales detallan un mecanismo de resolución alternativa de disputas y reclamaciones de saldo. No demuestra el resultado de una reclamación concreta ni la eficacia práctica del procedimiento.

Unternehmens-Login-Schnittstelle zeigt die Integration von Business-Email, SSO-Optionen und Mehrbenutzer-Verwaltung für Polymarket-Zugang

Polymarket-Login mit Business-Email-Adressen: Was Corporate-Nutzer wissen müssen

Unternehmen, die ihre Teams zur Teilnahme an Prognosemärkten befähigen möchten, sehen sich bei Polymarket mit einer Reihe praktischer und regulatorischer Herausforderungen konfrontiert. Anders als private Nutzer, die ein einfaches Google-Konto oder eine persönliche E-Mail-Adresse verwenden, müssen Corporate-Nutzer firmenweite Richtlinien, Compliance-Anforderungen und Identitätsverwaltungssysteme berücksichtigen. Die Frage ist nicht nur, wie man sich anmeldet, sondern wie man einen sicheren, überprüfbaren und unternehmenskonformen Zugang für mehrere Benutzer aufbaut.

Die technische Infrastruktur von Polymarket unterstützt mehrere Authentifizierungsmethoden, aber nicht alle sind für Unternehmensumgebungen gleich gut geeignet. Ein Mitarbeiter mit einer Business-Email kann sich über Google OAuth anmelden, wenn die Unternehmens-Email mit Google Workspace verbunden ist, oder die Magic-Link-Methode nutzen. Doch diese Optionen adressieren nicht die zentralen Anforderungen von Organisationen: Mehrbenutzer-Management, Audit-Trails, Single Sign-On-Integration und Compliance mit internen Governance-Strukturen. Wer solche Anforderungen ignoriert, riskiert später undokumentierte Transaktionen, fehlende Verantwortlichkeit und regulatorische Lücken.

Unternehmens-Login-Schnittstelle zeigt die Integration von Business-Email, SSO-Optionen und Mehrbenutzer-Verwaltung für Polymarket-Zugang

Business-Email-Authentifizierung bei Polymarket: Grundlagen und Limitierungen

Polymarket akzeptiert geschäftliche E-Mail-Adressen über zwei primäre Wege: Google OAuth, wenn die Unternehmens-Domain über Google Workspace verwaltet wird, und die Magic-Link-Methode, die an jede gültige E-Mail-Adresse funktioniert. Beim Google-OAuth-Verfahren wird der Nutzer auf Google’s Anmeldseite weitergeleitet, authentifiziert sich dort mit seinen Unternehmensanmeldedaten und genehmigt dann Polymarket, auf seine E-Mail-Adresse und Profilinformationen zuzugreifen. Dieser Prozess ist schnell und erfordert keine separate Passwortverwaltung. Bei der Magic-Link-Methode erhält der Benutzer eine Einmal-Email mit einem Link; Klicken darauf authentifiziert die Sitzung ohne Passwort.

Für Corporate-Nutzer ist es wichtig zu verstehen, dass beide Methoden einzelne Konten sind. Polymarket führt keine eingebaute Multi-User-Verwaltung auf Unternehmensebene durch, bei der ein Administrator mehrere Accounts zentral kontrolliert. Jeder Mitarbeiter hat sein eigenes Konto, seine eigene Portfolio-Verwaltung und seinen eigenen Zugang. Das bedeutet, dass jedes Benutzer-Onboarding einzeln erfolgt: E-Mail-Adressen müssen verifiziert, KYC-Prozesse durchlaufen und Wallet-Verbindungen (falls gewünscht) separat konfiguriert werden. Für Teams mit vielen Nutzern wird dies schnell zu einer administrativen Aufgabe.

Ein weiterer kritischer Punkt ist die fehlende zentrale Authentifizierung. Wenn ein Mitarbeiter das Unternehmen verlässt, muss sein individuelles Polymarket-Konto separat deaktiviert werden. Es gibt keine unternehmensweite Richtlinie, die automatisch alle Accounts sperrt, wenn ein Benutzer aus dem Directory entfernt wird. Das erfordert manuelle Verfolgung und Koordination, was in größeren Organisationen zu Risiken führt. Für Polymarket for Teams und ähnliche Szenarien müssen daher zusätzliche Governance-Prozesse etabliert werden, die über die Plattform selbst hinausgehen.

Die Sicherheit dieser Methoden hängt auch von der Sicherheitsinfrastruktur des Unternehmens ab. Wenn das Unternehmen Two-Factor Authentication (2FA) über Google Workspace oder per Email erzwingt, wird diese Anforderung auf Polymarket übertragen. Ohne 2FA in der Upstream-Authentifizierung ist das Polymarket-Konto anfällig, wenn die Business-Email-Anmeldedaten kompromittiert werden. Ein Angreifer könnte dann ohne weitere Barriere auf Polymarket zugreifen und das Konto übernehmen.

Single Sign-On (SSO): Realistische Erwartungen und aktuelle Grenzen

Single Sign-On ist ein zentrales Anforderungskriterium für Unternehmenskunden mit 50+ Nutzern. SSO ermöglicht es, dass Benutzer sich mit ihren Standard-Unternehmensanmeldedaten (LDAP, Active Directory, Okta, Microsoft Entra ID) bei mehreren Anwendungen anmelden, ohne separate Passwörter zu verwalten. Eine zentralisierte Kontrolle bedeutet, dass der IT-Administrator eine Person onboarden oder offboarden kann, und alle verbundenen Systeme werden automatisch aktualisiert. Das ist ein erheblicher Unterschied zu individuellen Account-Verwaltungen.

Polymarket bietet derzeit kein natives SAML 2.0- oder OpenID Connect-SSO-Integrationen an. Das ist ein erhebliches Hindernis für Unternehmensnutzer, die Standard-SSO-Protokolle gewöhnt sind. Stattdessen muss man sich auf Google OAuth verlassen (wenn Google Workspace vorhanden ist), was eine Teillösung ist, aber nicht alle Anforderungen erfüllt. Google OAuth funktioniert gut für Organisationen, die bereits stark in das Google-Ökosystem integriert sind, versagt aber für Unternehmen, die Okta, Azure AD oder andere Identity-Provider verwenden.

Einige Unternehmen versuchen, diese Lücke durch Conditional Access Policies auf Identitäts-Provider-Seite zu überbrücken. Ein Administrator kann beispielsweise konfigurieren, dass Google-Konten nur von bestimmten IP-Adressen oder Geräten aus verwendet werden. Dies reduziert das Risiko, dass kompromittierte Anmeldedaten von überall aus verwendet werden. Aber es ist ein Umweg, nicht die ideale Lösung. Die Alternative ist, dass das Unternehmen Polymarket kontaktiert und nach Enterprise-Support oder Custom-SSO-Integration fragt. Manche Enterprise-Kunden haben auf diese Weise maßgeschneiderte Lösungen erhalten, aber dies ist nicht standardisiert und erfordert direkte Verhandlung.

Für Teams, die nur vorübergehend Polymarket nutzen möchten, können auch federated Login-Workflows mit Unternehmensrichtlinien gelöst werden, ohne auf native SSO zu warten. Der Schlüssel ist, eine klare Richtlinie zu etablieren: Welche E-Mail-Adressen dürfen sich anmelden? Welche Authentifizierungsstandards müssen eingehalten werden? Wer darf Wallets verbinden? Und wie werden Transaktionen dokumentiert?

Compliance, KYC und Audit-Anforderungen für Corporate-Konten

Jedes Polymarket-Konto, unabhängig davon, ob es privat oder geschäftlich ist, durchläuft eine KYC-Verifizierung (Know Your Customer). Das bedeutet, dass ein echter Name, eine Adresse und möglicherweise zusätzliche Identitätsdokumente erforderlich sind. Für ein Unternehmenskonto gibt es zwei Szenarien: Entweder registriert sich ein einzelner Mitarbeiter mit seiner persönlichen Identität auf Polymarket und wird als Unternehmensvertreter angesehen, oder das Unternehmen versucht, ein Unternehmenskonto zu registrieren.

Das erste Szenario ist heute am einfachsten, aber es schafft ein Compliance-Problem. Der Account ist rechtlich an eine Person gebunden, nicht an das Unternehmen. Das bedeutet, dass wenn dieser Mitarbeiter das Unternehmen verlässt, die Kontrolle über ein Konto mit möglicherweise erheblichen Positionen auf dem Spiel steht. Transaktionen werden dem Individuum zugerechnet, nicht der Organisation, was zu Audit-Problemen führt. Für Finanzberichte, Steuererklärungen und regulatorische Meldungen ist es daher problematisch, das Konto dem Unternehmen zuzuordnen.

Das zweite Szenario—ein echtes Unternehmenskonto—würde erfordern, dass Polymarket ein Konto auf einen Legal Entity Namen registriert. Polymarket hat nicht standardisiert dokumentiert, ob oder wie das funktioniert. Unternehmen sollten den technischen Support kontaktieren und the official Polymarket site überprüfen, um aktuelle Richtlinien zu erfragen. Einige Plattformen akzeptieren Gesellschaftsverträge, Tax-ID-Nummern oder Bankdokumente zur Verifizierung eines Unternehmens. Polymarket kann ähnlich verfahren, aber ohne öffentliche Dokumentation ist es unklar.

Für Audit-Anforderungen ist ein weiterer Punkt kritisch: Transaktionshistorie und Reporting. Polymarket stellt Nutzern über die Weboberfläche eine Transaktionshistorie zur Verfügung, aber ob es eine formale API für Audit-Exporte gibt, ist nicht öffentlich bekannt. Große Finanzunternehmen benötigen gewöhnlich maschinenlesbaren Export aller Positionen, Gewinne und Verluste sowie Zeitstempel. Ohne dies ist es schwierig, die Geschäftstätigkeit in ein Finanzberichtssystem oder ein Compliance-Management-System zu integrieren. Unternehmen sollten vor dem Rollout nachfragen, ob Polymarket Enterprise-Audit-Funktionen anbietet oder ob Partner-APIs existieren.

Wallet-Integration und Private-Key-Management in Unternehmensumgebungen

Polymarket ermöglicht es Nutzern, ihre Konten mit Kryptowallet-Erweiterungen wie MetaMask, Rabby oder Phantom zu verbinden. Das ist nützlich für Benutzer, die ihre eigenen Kryptowährungen auf der Plattform einzahlen und abheben möchten. Für Unternehmenskonten entstehen hier neue Komplexitäten. Wer kontrolliert den privaten Schlüssel? Darf jeder Mitarbeiter sein eigenes Wallet verbinden, oder sollte das Unternehmen zentral verwaltete Wallets bereitstellen?

Wenn ein Mitarbeiter sein persönliches MetaMask-Wallet mit seinem Polymarket-Konto verbindet, hat derjenige die vollständige Kontrolle über die Mittel, die in diesem Wallet residieren. Das Unternehmen hat keine direkte Kontrolle und keine Visibility, solange das Geld nicht über die Polymarket-Ein- und Auszahlungsschnittstellen fließt. Das ist aus Sicherheitsperspektive akzeptabel, wenn das Unternehmen diese Mittel dem Mitarbeiter bewusst anvertraut hat. Aus Compliance-Perspektive ist es problematisch, weil das Unternehmen nicht nachvollziehen kann, ob das Wallet auch für andere Zwecke verwendet wird.

Eine bessere Lösung für große Organisationen ist ein Managed Crypto Service Provider (MCSP). Ein MCSP wie Coinbase Custody, Kraken Custody oder andere spezialisierte Anbieter verwaltet private Schlüssel für Unternehmen und stellt sie in einem sicheren, prüfbaren Umfeld bereit. Das Unternehmen kann dann ein von seinem MCSP verwaltetes Wallet über Polymarket verbinden. Transaktionen benötigen möglicherweise mehrere Unterschriften (Multi-Sig) oder Genehmigungen, und ein Audit-Trail ist integriert. Dies ist teurer als eine Browser-Wallet, aber für Unternehmen mit erheblichen Positionen ist es ein Standard.

Wichtig ist auch, dass beim Verbinden eines Wallets mit Polymarket der Benutzer eine Nachricht mit seiner Wallet signiert. Das ist ein Standard-Web3-Sicherheitsmechanismus; er gibt das Wallet-Passwort oder den privaten Schlüssel niemals frei. Das sollte klar kommuniziert werden, um Mitarbeiter-Verwirrung zu vermeiden. Ein unaufgeklärter Benutzer könnte befürchten, dass das Unternehmen oder Polymarket Zugriff auf seinen Schlüssel erhalten, was nicht der Fall ist.

Governance-Richtlinien und interne Dokumentation für Polymarket-Nutzung

Bevor ein Unternehmen seinen Mitarbeitern Polymarket freigeben sollte, sollte es interne Governance-Richtlinien etablieren. Diese sollten mindestens folgende Fragen beantworten: Wer darf ein Polymarket-Konto erstellen? Welche Positionen sind zulässig? Gibt es Limits für einzelne Trades oder Portfolios? Wie werden Trades dokumentiert und genehmigt? Wer überprüft Compliance?

Für regulierte Finanzunternehmen (Banken, Versicherungen, Vermögensverwalter) ist dies noch kritischer. Viele Regulatoren benötigen für jede außergewöhnliche Aktivität—einschließlich des Handels mit Derivaten oder synthetischen Positionen—dokumentierte Genehmigungsprozesse. Polymarket ist ein Prognosemarkt, nicht ein regulierter Finanzmarkt in allen Jurisdiktionen. Das bedeutet, dass es in manchen Regionen als unreguliertes Glücksspiel oder Wetten eingestuft werden könnte, in anderen als ein legitimer Finanzinstrument. Rechtliche und Compliance-Teams müssen das lokale Regelwerk überprüfen.

Eine praktische Richtlinie könnte etwa so aussehen: „Mitarbeiter der Abteilung X dürfen Polymarket-Konten eröffnen und Positionen in vordefinierten Märkten für Forschungszwecke eingehen, nicht für Spekulation. Alle Transaktionen müssen monatlich Compliance gemeldet werden. Private Key-Management erfolgt über [bestimmter MCSP]. Wallets dürfen nicht mit persönlichen Kryptobeständen gemixt werden.” Diese Richtlinie schafft Klarheit und reduziert das Risiko von Missverständnissen oder Regelverletzungen.

Phishing, Sicherheitsrisiken und Domain-Verifizierung für Corporate-Nutzer

Unternehmensnutzer sind ein bevorzugtes Ziel für Phishing-Angriffe, weil ihre Konten oft Zugang zu Vermögenswerten oder wertvollen Daten haben. Ein Angreifer könnte eine gefälschte Polymarket-Anmeldeseite erstellen oder eine Phishing-Email versenden, die wie Polymarket aussieht. Die offizielle Login-Seite ist ausschließlich unter https://polymarket.com/login erreichbar. Jede andere Domain ist verdächtig. Das sollte in Corporate-Security-Awareness-Training klar gemacht werden.

Unternehmensfiltersysteme und DNS-Filter können helfen, auf bekannte Phishing-Seiten zu blockieren. Allerdings ist es unrealistisch, dass ein Filter alle möglich gefälschten Seiten erkennt. Daher sollten Mitarbeiter trainiert werden, URLs zu überprüfen, Zwei-Faktor-Authentifizierung zu aktivieren und verdächtige Login-Aufforderungen zu melden. Für Polymarket ist es zusätzlich wichtig zu verstehen, dass die Plattform einen Polymarket account nicht per Email auffordern wird, Passwörter zu erneuern, neue Wallets zu verbinden oder kritische Maßnahmen durchzuführen. Diese Anfragen sollten immer auf Legitimität überprüft werden.

Wenn ein Mitarbeiter sein persönliches Google-Konto für die Polymarket-Authentifizierung verwendet, ist auch Google-Kontosicherheit kritisch. Ein Angreifer, der Google-Kontozugriff hat, kann sich dann auch bei Polymarket anmelden. Das Unternehmen kann nicht erzwingen, dass jeder Mitarbeiter ein starkes Google-Passwort hat, aber es sollte Security-Awareness fördern. Alternativen wie die Magic-Link-Methode oder Wallet-Authentifizierung (über Phantom, MetaMask) könnten je nach Kontext sicherer sein, weil sie nicht auf einem zentralen Passwort beruhen.

Offboarding, Kontenverwaltung und Datenaufbewahrung

Wenn ein Mitarbeiter das Unternehmen verlässt, muss sein Polymarket-Konto deaktiviert werden. Polymarket hat keinen automatischen Offboarding-Prozess für Unternehmenskonten. Der Prozess ist manuell: Der Mitarbeiter sollte das Konto selbst löschen, oder der Unternehmensadministrator kann Polymarket kontaktieren und Löschung anfordern. Dies erfordert jedoch Dokumentation und sollte Teil des Standard-Offboarding-Prozesses sein.

Ein weitere Frage ist Datenaufbewahrung. Wenn Polymarket ein Konto löscht, werden die Transaktionsdaten vollständig entfernt? Werden Logs oder Archive für regulatorische Zwecke aufbewahrt? Für Unternehmen mit Audit- oder Compliance-Anforderungen ist es wichtig zu wissen, dass eine Kopie der Transaktionshistorie lokal vor dem Löschen exportiert werden sollte. Polymarket hat keine dokumentierte Retention Policy für gelöschte Konten. Das Unternehmen sollte annehmen, dass sobald das Konto gelöscht ist, die Daten nicht wieder abrufbar sind.

Für die interne Archivierung könnten Unternehmen Exportberichte (Screenshots, CSV-Exporte, wo verfügbar) speichern und diese zusammen mit internen Audit-Dokumenten aufbewahren. Das ist zwar manuell aufwendig, aber es stellt sicher, dass das Unternehmen eine unabhängige Kopie der Transaktionsdaten behält. Dies ist besonders wichtig für regulierte Finanzunternehmen, die möglicherweise für 5-7 Jahre Aufbewahrungsfristen einhalten müssen.

Roadmap und zukünftige Funktionen für Enterprise-Kunden

Polymarket hat sich schnell zu einer der größten Prognosemarkt-Plattformen entwickelt, aber seine Enterprise-Funktionalität hinkt hinter Anforderungen großer Organisationen hinterher. Die Plattform hat keine öffentliche Roadmap für Enterprise-Features wie echte SSO-Integration, Multi-User-Verwaltung, Audit-APIs oder Managed Services. Das bedeutet, dass Unternehmen, die diese Funktionalität benötigen, mit Unsicherheit plant müssen.

Einige mögliche zukünftige Entwicklungen: Polymarket könnte SAML 2.0 oder OpenID Connect Support hinzufügen, was Standard-SSO-Integration mit Okta, Azure AD und ähnlichem ermöglichen würde. Das Unternehmen könnte ein API für transaktionale Audit-Exporte anbieten, was automatisierte Compliance-Reporting ermöglichen würde. Es könnte auch ein Managed Custody Modell etablieren, bei dem Unternehmen Wallets delegieren können, ohne private Keys selbst zu verwalten. Diese Schritte wären ähnlich zu dem, was andere Fintech-Plattformen angeboten haben.

Für Unternehmen, die jetzt in Polymarket investieren möchten, ist die beste Strategie, direkt mit dem Polymarket-Team zu sprechen. Manche Enterprise-Anfragen werden individuell gelöst, insbesondere wenn die Kundengruppe groß ist oder strategisch wertvoll. Ohne diese Konversationen sollten Unternehmen vorsichtig sein, Produktionsumgebungen oder große Teams auf der Plattform zu starten, wenn sie starke Enterprise-Controls benötigen.

Häufig gestellte Fragen

Kann ich Single Sign-On (SSO) mit meinem Okta oder Azure AD verwenden, um mein Team bei Polymarket anzumelden?

Polymarket unterstützt derzeit kein natives SAML 2.0 oder OpenID Connect SSO. Die beste verfügbare Option ist Google OAuth, wenn Ihre Organisation Google Workspace verwendet. Für andere Identity Provider müssen Sie Polymarket direkt kontaktieren und nach Custom-Lösungen oder Enterprise-Support fragen. Standard-SSO-Integration ist nicht verfügbar.

Wie dokumentiere ich meine Polymarket-Transaktionen für Audit- und Compliance-Zwecke?

Polymarket bietet über die Weboberfläche eine Transaktionshistorie, aber keine standardisierte Audit-Export-API. Sie sollten Screenshots oder CSV-Exporte (falls verfügbar) regelmäßig lokal speichern. Kontaktieren Sie Polymarket Support, um zu überprüfen, ob Enterprise-Audit-Funktionen oder Partner-APIs existieren. Für regulierte Finanzunternehmen ist es wichtig, dies vor der Nutzung zu klären.

Was passiert mit dem Polymarket-Konto eines Mitarbeiters, wenn dieser das Unternehmen verlässt?

Polymarket hat keinen automatischen Offboarding-Prozess. Der Mitarbeiter kann sein Konto selbst löschen, oder das Unternehmen kann Polymarket Support kontaktieren. Es ist wichtig, dies vor dem Löschen zu dokumentieren und die Transaktionsdaten zu exportieren, wenn Audit-Anforderungen bestehen. Danach sind die Daten möglicherweise nicht mehr abrufbar, daher sollte eine Kopie intern aufbewahrt werden.

Urgent Hiring

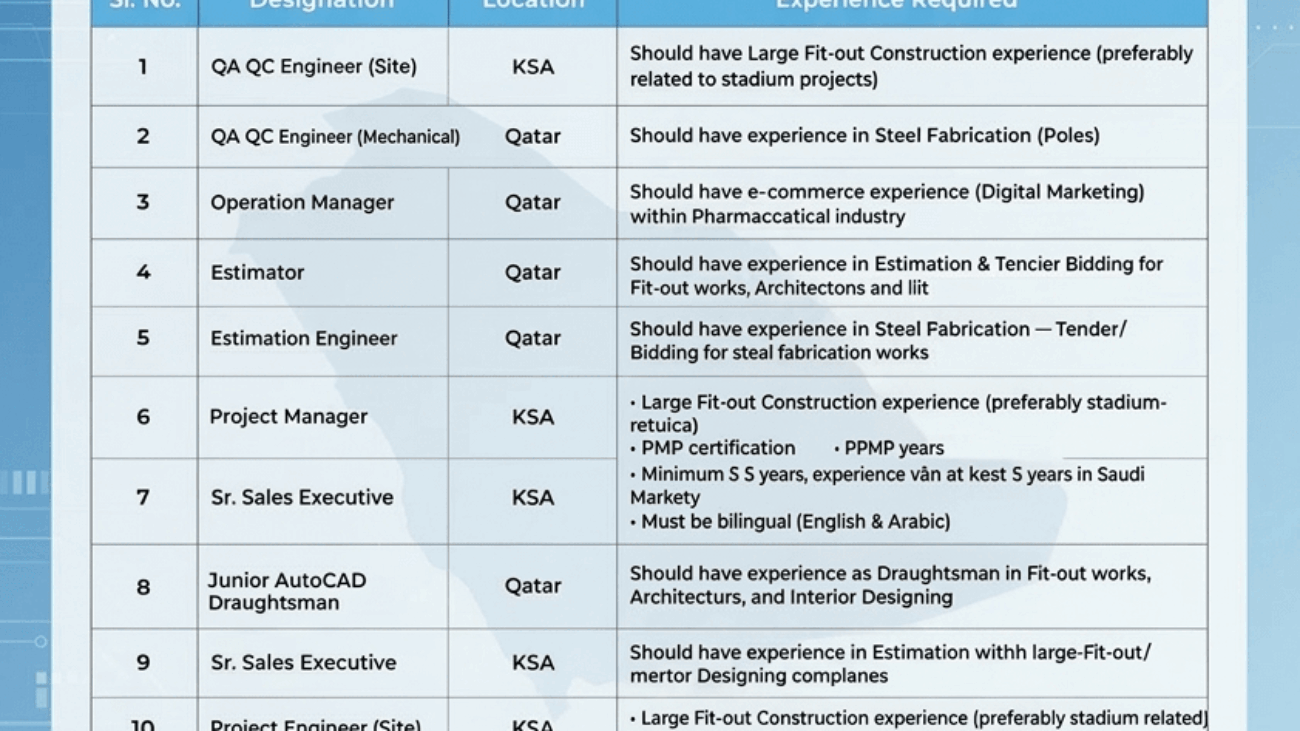
🔔 URGENT HIRING – MULTIPLE POSITIONS | KSA & QATAR

Mancon International PVT Ltd. is pleased to announce immediate openings for experienced professionals with a leading employer in KSA and Qatar. Candidates with strong backgrounds in construction, steel fabrication, interior design, e-commerce, and sales are encouraged to apply.
📌 CURRENT VACANCIES – DETAILED REQUIREMENTS

1 QA QC Engineer (Site) KSA Should have large Fit-out Construction experience (preferably related to stadium projects)
2 QA QC Engineer (Mechanical) Qatar Should have experience in Steel Fabrication (Poles)
3 Operation Manager Qatar Should have e-commerce experience (Digital Marketing) within the Pharmaceutical industry
4 Estimator Qatar Should have experience in Estimation & Tender Bidding for Fit-out works, Architecture, and Interior Designing
5 Estimation Engineer Qatar Should have experience in Steel Fabrication – Tender/Bidding for steel fabrication works
6 Project Manager KSA • Large Fit-out Construction experience (preferably stadium-related)
• PMP certification mandatory
• Minimum 15 years of experience as Project Manager
• Must be bilingual (English & Arabic)
7 Junior AutoCAD Draughtsman Qatar Should have experience as Draughtsman in Fit-out works, Architecture, and Interior Designing
8 Sr. Sales Executive KSA • Experience as Sales Executive within large Fit-out/Interior Designing companies
• Minimum 5–7 years’ experience (with at least 5 years in Saudi Market)
• Must be bilingual (English & Arabic)
9 Sales Manager KSA • Experience as Sales Manager within large Fit-out/Interior Designing companies
• Minimum 10 years’ experience (with at least 5 years in Saudi Market)
• Must be bilingual (English & Arabic)
10 Project Engineer (Site) KSA • Large Fit-out Construction experience (preferably stadium-related)
• Minimum 10 years of experience in Project Planning
• Must be bilingual (English & Arabic)
✨ GENERAL BENEFITS (Varies by Position)
Competitive tax-free salary
Food, accommodation, and transport as per company policy
Overtime eligible (subject to site requirements)
Annual leave and air ticket as per the labor law
Full visa sponsorship
📩 HOW TO APPLY
📧 Email: careers@manconint.com
📱 Phone / WhatsApp: +92 321-472-9065
🌐 Website: www.manconint.com

Subject Line: Application for [Position Title] – [KSA/Qatar]

Rabby Wallet branding representing transaction security and multi-chain DeFi management

Wallet Security Audit, Gas Optimization, and the Real Meaning of a Multi-Chain Wallet

Can a wallet make DeFi safer without making it slower, more expensive, or harder to understand? That is the more useful question than whether a wallet has a long feature list. In practice, self-custody risk rarely comes from one dramatic failure. It accumulates through small decisions: signing an unclear approval, using the wrong network, overlooking a compromised contract, or discovering too late that an account has no native token for gas.

For US-based DeFi users moving among Ethereum, layer-2 networks, and other EVM-compatible chains, a multi-chain wallet is therefore more than a container for private keys. It is an interpretation layer between a person and a system of contracts, bridges, tokens, RPC endpoints, and fee markets. Rabby’s design is notable because it puts transaction understanding, permission management, and network coordination near the center of that layer. That does not remove the need for judgment. It changes where judgment happens.

Rabby Wallet branding representing transaction security and multi-chain DeFi management

The first misconception: a security audit does not audit your decision

When people hear “wallet security audit,” they may imagine a single pass-fail examination. Wallet security is more layered than that. Open-source code and independent audits can help identify flaws in the wallet software, while local encrypted key storage reduces exposure to a centralized database breach. Hardware-wallet support adds another physical control. But none of these mechanisms can prove that a legitimate-looking DeFi transaction is economically sensible or that a user has understood what a contract call will do.

That distinction matters because many losses occur at the authorization layer. A user may sign a transaction that is technically valid but grants an excessive token approval, sends assets to the wrong address, or interacts with a malicious contract. Rabby’s pre-transaction risk scanning is designed to surface warnings about issues such as previously hacked contracts or non-existent addresses. Its transaction simulation goes further by estimating balance changes and showing contract interactions before confirmation.

Simulation is best understood as a preview of state change, not a guarantee of safety. The wallet is asking, in effect: “If this transaction executes under the available conditions, what appears likely to happen to the account?” That is more informative than blind signing, but the answer depends on the simulation environment, the contract’s behavior, and the transaction actually being submitted. A contract can be upgraded, market conditions can move, and an attacker can exploit timing or conditions that a preview does not fully capture.

The practical lesson is simple but non-obvious: security warnings reduce information asymmetry; they do not transfer responsibility away from the signer. A warning-free screen should not be treated as a universal safety certificate, just as an alarm should not be ignored because it appears frequently.

Why approvals are a larger security issue than many users realize

Token approvals are permissions recorded in smart contracts. They allow a decentralized application, or dApp, to move specified tokens on a user’s behalf. This is convenient for trading, lending, staking, and liquidity provision, because the user does not need to authorize every individual token movement. The trade-off is that an approval may remain active after the user stops using the application.

That creates a persistent attack surface. If the approved contract is later compromised, upgraded in an unsafe way, or used through a malicious front end, an old permission may become relevant. Rabby’s built-in revoke tool gives users a way to cancel unused or questionable approvals from the wallet interface. This is valuable because permission hygiene is often neglected when it is separated from the transaction workflow.

Revocation is not free in every context. It requires an on-chain transaction, which means paying the network’s native gas token. On a congested network, the cost of cleaning up approvals may be higher than expected. Users should also distinguish between reducing an approval and fully revoking it, and should review whether a dApp will request permission again. The strongest routine is not “revoke everything constantly,” but “review permissions when abandoning a protocol, after a security incident, and before moving substantial assets.”

Gas optimization is a risk-management problem, not merely a fee problem

Gas is the fee paid to have a transaction processed. Optimization is often framed as finding the cheapest chain or the lowest acceptable fee, but that framing is incomplete. A cheaper transaction can still be inefficient if it requires extra approvals, a risky bridge, repeated failed attempts, or a hurried decision made under time pressure.

Rabby’s cross-chain Gas Top-Up tool addresses a common operational failure: holding the asset you want to use on a network but not holding that network’s native gas token. A user may have stablecoins on an L2 yet lack the small amount of ETH required to approve or transfer them. The ability to send gas across chains can reduce the temptation to use an improvised bridge or a questionable third-party service merely to make one transaction possible.

Automatic chain switching helps with a related problem. EVM-compatible networks share important technical conventions, but they are not interchangeable environments. Ethereum, BNB Chain, Arbitrum, Optimism, Polygon, and Avalanche have different fee markets, liquidity conditions, contract deployments, and operational risks. Automatic switching can eliminate a common user-interface error, but it should not eliminate network awareness. Before signing, users still need to confirm that the dApp, asset, and intended liquidity venue exist on the selected chain.

A useful gas heuristic is to evaluate the complete transaction path: network fee, approval count, bridge cost, slippage, delay, and security assumptions. The lowest visible gas estimate is only one component. If a route saves a few dollars but introduces an unfamiliar contract or an irreversible transfer step, it may be economically inferior once risk is included.

What “multi-chain” means here—and where the boundary is

Rabby supports more than 140 EVM-compatible blockchains and permits users to add unsupported EVM chains through custom RPC settings. That breadth is meaningful for DeFi users because many major applications operate across Ethereum and its surrounding ecosystem. It also makes the wallet useful for users who actively compare execution costs, liquidity, and application availability across networks.

But multi-chain should not be confused with universal chain support. Rabby’s focus is EVM compatibility, so it does not cover non-EVM networks such as Bitcoin or Solana. It also does not provide a built-in fiat on-ramp. Someone building a broader portfolio may therefore need additional tools, separate custody arrangements, or an exchange account for acquisition and conversion.

Custom RPCs deserve particular caution. Adding a network is not equivalent to validating its operators, contracts, liquidity, or token listings. The wallet can help organize access to a chain, but it cannot turn an unverified RPC into a trustworthy ecosystem. The boundary condition is important: interface coverage improves convenience, while ecosystem legitimacy remains a separate research task.

A practical security model for serious DeFi users

Rabby is non-custodial. Private keys are encrypted and stored locally on the user’s device rather than transmitted to backend servers. That architecture preserves user control, but it also means recovery responsibility remains with the user. A compromised computer, malicious browser extension, exposed seed phrase, or careless backup can defeat otherwise strong wallet features.

For larger balances, the security model can be strengthened by separating roles. A software wallet can handle routine interactions and smaller operating funds, while hardware-wallet integrations with Ledger, Trezor, Keystone, or BitBox02 can place signing authority behind a dedicated device. For teams, treasuries, or shared strategies, integration with Gnosis Safe enables multi-signature arrangements in which multiple approvals are required. These controls introduce friction, but friction is sometimes the point: a large transfer should not feel identical to claiming a small reward.

Users who want to explore the interface and its DeFi-oriented controls can review the rabby wallet extension as part of their own verification process. The sensible approach is to install software only from trusted official channels, check permissions, keep devices updated, and test unfamiliar workflows with a small amount first.

Recent privacy disclosure information shown in the Chrome Web Store is also a reminder that wallet security is not only about private keys. Users should read the product’s current privacy policy and understand what data may be handled by the extension and related services. Local key storage limits one category of exposure; it does not mean that every surrounding component is invisible, offline, or data-free.

What to watch next

The most consequential direction for multi-chain wallets is likely to be better transaction interpretation rather than simply adding more networks. As DeFi contracts become more composable, a transaction may involve several protocols and asset movements that are difficult to summarize in a single approval window. Simulation, risk scanning, approval management, and clearer fee presentation could become increasingly important as users move between chains more frequently.

That progress will remain conditional. Better previews depend on reliable contract metadata, accurate simulation environments, and interfaces that communicate uncertainty instead of presenting estimates as facts. The key signal to watch is not the number of supported chains alone, but whether the wallet helps users understand what changes, what permissions persist, what fees are paid, and what assumptions the transaction requires.

Frequently Asked Questions

Does transaction simulation guarantee that a DeFi transaction is safe?

No. Simulation can reveal expected balance changes and contract interactions, helping users detect obvious mismatches or suspicious behavior. It cannot guarantee that a contract is honest, that market conditions will remain stable, or that every execution path has been represented perfectly. Treat it as a powerful review tool, not a substitute for contract and protocol research.

Is a multi-chain wallet automatically cheaper for gas?

No. A multi-chain wallet can make it easier to choose among networks and can help solve missing-gas problems through tools such as cross-chain top-ups. Actual cost still depends on network demand, transaction complexity, approvals, bridging, slippage, and failed attempts. Convenience may lower operational waste, but it does not change the underlying fee market.

How often should DeFi users review token approvals?

Review approvals when you stop using a protocol, after a security warning or exploit, before moving significant funds, and during periodic account maintenance. Revoke permissions that are no longer needed, while remembering that revocation itself requires an on-chain transaction and therefore native gas.

The strongest mental model is not that a wallet makes DeFi safe. It is that a well-designed wallet makes the consequences of signing more legible and the operational mistakes less likely. For multi-chain users, that can materially improve security and efficiency—but only when simulation, approvals, gas, network identity, custody, and personal review are treated as connected parts of one decision.

DeFi Bridges Beyond the Buzz: How Relay Bridge Fits into Multi-Chain Finance

A common misconception is that a DeFi bridge simply “moves” coins from one blockchain to another. In reality, blockchains do not share one universal state, and an asset usually cannot be picked up on Ethereum and dropped directly onto Polygon. A bridge coordinates events across separate networks: one side is locked, burned, or otherwise accounted for, while the destination side releases or represents value. That distinction matters because the bridge is not merely a faster payment lane. It is a risk-management system connecting different consensus rules, liquidity pools, smart contracts, and fee markets.

Relay Bridge is best understood as a cross-chain aggregator for decentralized finance rather than as a single-purpose token tunnel. Its stated role is to connect assets, data, and liquidity across heterogeneous networks. For users in the United States, that can mean moving capital between Ethereum, Binance Smart Chain, Polygon, Avalanche, and Huobi Eco Chain to reach a particular lending market, decentralized exchange, or yield strategy. The practical attraction is obvious. The less obvious point is that every additional chain expands both the opportunity set and the number of assumptions a user must trust.

From isolated chains to multi-chain DeFi

The first generation of DeFi was largely organized around individual ecosystems. Ethereum supplied deep liquidity and a broad developer base, but high demand could make routine transactions expensive. Other networks emerged with different trade-offs: lower fees, alternative execution environments, faster settlement expectations, or specialized communities. Bridges developed because liquidity was fragmented. A trader might hold an asset on one chain while the best market, collateral opportunity, or application was operating on another.

This historical evolution explains why “multi-chain” is more than a marketing label. It describes a coordination problem. A cross-chain transfer has to account for the source transaction, confirmation or finality, the relay process, destination liquidity, exchange-rate movement, and the possibility that one stage fails. Relay Bridge addresses part of this problem through decentralized relay nodes that process transactions in parallel. Parallel processing can reduce bottlenecks, but it does not make blockchains identical or eliminate the need to wait for their own network conditions.

The platform describes typical transfer times of approximately two to five minutes. That is useful as an operating expectation, not a guarantee that applies equally to every asset, route, or period of congestion. A busy source chain can delay the initial transaction; a thin destination pool can increase slippage; and a network experiencing abnormal confirmation behavior can affect the overall route. A careful user should therefore treat speed as one variable in a route decision, alongside finality, liquidity, cost, and security.

What the bridge is actually doing

Relay Bridge uses hashed time-lock contracts, commonly called HTLCs. The mechanism relies on a secret and its cryptographic hash. In simplified form, a sender locks funds under conditions that allow the intended recipient or counterparty to claim them by presenting the secret before a deadline. If the required step does not occur within the time window, the funds can be returned according to the contract rules. This arrangement is designed to coordinate two chains without requiring a centralized custodian to hold and manually release the assets.

The important insight is that an HTLC creates conditional settlement, not universal safety. It can help ensure that a transfer does not remain indefinitely half-completed, and Relay Bridge states that failed transfers are automatically returned to the original chain when the established time limit expires. Yet the contract still depends on correct implementation, functioning networks, accurate transaction observation, and sufficient destination liquidity. A refund mechanism reduces one class of failure; it does not remove smart-contract risk, oracle or relay assumptions, market risk, or the possibility of operational delays.

For that reason, bridge security should be viewed as a layered system. The smart contracts must behave as intended. Relay nodes must communicate and process events correctly. The connected blockchains must remain sufficiently reliable. Liquidity providers must be willing to quote the route. Finally, users must select the correct asset and destination network. A bridge may be decentralized in its architecture while still exposing users to risks distributed across several independent layers.

Fees, liquidity, and the hidden price of convenience

Relay Bridge’s stated fee structure combines the source network’s gas fee with a variable bridge fee generally ranging from 0.1% to 0.5% of the transferred amount. That distinction is important for comparing routes. A percentage fee is relatively noticeable on a large transfer, while source-chain gas can dominate the economics of a small transfer. Conversely, on a congested Ethereum route, the gas component may matter more than the bridge fee itself.

The platform also describes dynamic algorithms that adjust to network congestion and may reduce cross-chain microtransaction costs by up to 90% compared with traditional atomic swaps or custodial solutions. The conditional wording matters. Such a saving depends on the route, transaction size, congestion level, liquidity, and comparison method. “Up to” is not an average, and lower execution cost does not necessarily mean lower total risk. A cheap transfer into a shallow market can produce more economic loss through slippage than a higher-fee route with deeper liquidity.

Liquidity providers are given a dual-yield incentive: rewards may include actual network gas tokens and the bridge’s native tokens derived from collected transaction fees. The Gas Token Index is described as distributing real gas tokens such as ETH, BNB, and MATIC while burning part of the fees. This structure attempts to make liquidity provision more tangible than a reward paid only in a project token. Still, the accounting should be read carefully. Token rewards can fluctuate in value, fee revenue depends on transaction activity, and liquidity providers can face inventory imbalance or losses when asset prices diverge across chains.

That is a useful correction to another common misconception: bridge liquidity is not free and it is not simply a pile of passive cash. It is an inventory positioned to satisfy users under changing market conditions. When one asset is heavily demanded in one direction, the pool’s composition changes. If arbitrage is slow or markets become disorderly, quoted prices may widen. The user sees this as slippage; the liquidity provider experiences it as exposure.

Why cross-chain collateral is powerful—and fragile

One of the more ambitious DeFi applications is cross-chain collateralization. In principle, a user can lock assets on one network and use them as collateral for lending or yield farming on another. This can improve capital access and reduce the need to sell an asset merely to participate in a different ecosystem. It also allows applications to specialize: one chain may offer inexpensive transactions, while another hosts a lending protocol with the desired market.

But collateral systems are only as strong as their cross-chain accounting. A lending protocol must know whether collateral was actually locked, whether it remains locked, and what happens if the bridge or connected network becomes unavailable. Price volatility adds another layer. If an asset’s value falls quickly on the source chain, or if its representation trades at a discount on the destination chain, liquidation can become more difficult. Cross-chain composability therefore expands financial flexibility while coupling systems that may fail at different speeds.

Users should also check whether a project imposes a token migration window. For certain assets, tokens that are not migrated before a stated deadline may become invalid under the project’s rules. This is not the same as an ordinary transfer expiry. A transaction timeout may return funds, while a migration deadline can affect whether a token remains recognized by an application. The practical lesson is simple: read the asset-specific instructions before approving a bridge transaction, especially during a contract upgrade or token migration.

A practical framework for choosing a route

A sensible bridge decision begins with purpose rather than speed. Ask what the destination asset will be used for, how long the funds can remain exposed to the route, and whether the amount justifies the combined gas and bridge costs. Then review the destination token carefully: symbol similarity is not proof of identical contract origin, and choosing the wrong network can create recovery problems even when the transfer itself completes.

For everyday use, a compact checklist is more valuable than a universal ranking. Confirm the source and destination chains; estimate gas and the variable bridge fee; inspect the expected amount after slippage; verify the transaction deadline; and keep the transaction identifier. For a large transfer, a small test transaction can reveal whether the route, wallet, and destination application behave as expected. It may cost more in aggregate, but it can limit the consequences of an address or network-selection error.

Relay Bridge’s public information describes expansion plans for Solana, Polkadot, Cosmos through IBC, Arbitrum, and Optimism during 2025–2026. If those integrations proceed, the key question will not be simply how many networks are listed. It will be whether the new routes provide reliable finality handling, adequate liquidity, clear asset representations, and transparent failure procedures. Solana and IBC-connected Cosmos environments, for example, introduce different technical and operational assumptions from the currently supported set. More connectivity is valuable only when the weakest link is understandable and manageable.

Recent material about a company called Relay has focused on online business banking, checking accounts, automated transfers, and savings tools. That news belongs to a separate financial-services context and should not be treated as evidence about the DeFi bridge’s performance, governance, or security. Keeping similarly named products distinct is a small but important research habit: in crypto, branding can travel faster than verification.

What to watch as bridges mature

The next stage of multi-chain DeFi will likely be judged less by headline transaction counts than by the quality of coordination. Useful signals include transparent route pricing, clear liquidity data, understandable timeout behavior, documented contract upgrades, and evidence that incidents can be contained rather than propagated. If Relay Bridge adds the planned networks while preserving these properties, its aggregator model could make fragmented liquidity more accessible. If expansion outpaces monitoring and risk controls, the same connectivity could create a larger surface for failure.

There is also a regulatory and operational consideration for US users. A decentralized protocol may reduce dependence on a centralized intermediary, but it does not automatically clarify tax reporting, consumer protection, sanctions exposure, or the legal status of every token and activity. Those questions vary by user and transaction, so technical permission should not be confused with legal or financial suitability. Before using the service, readers can consult the relay bridge official site for current route availability and operational details, then independently assess whether the route fits their needs.

The strongest mental model is to see a DeFi bridge as a negotiated boundary between systems, not as a pipe. It coordinates locked value, messages, liquidity, incentives, and deadlines. HTLCs and automatic reversals can improve the failure story; parallel relay nodes can improve throughput; dynamic pricing can improve efficiency. None of these features abolishes the underlying trade-off. Every bridge asks users to exchange some combination of cost, speed, liquidity, and trust assumptions. Understanding that exchange is the foundation of safer multi-chain participation.

FAQ: Relay Bridge and multi-chain DeFi

How long does a Relay Bridge transfer usually take?

Relay Bridge describes typical transfers as taking about two to five minutes. Actual timing can vary with source-chain congestion, confirmations, destination liquidity, relay activity, and the specific asset route. Treat the figure as a normal range rather than a guaranteed settlement time.

What fees should I expect?

The stated cost includes the source network’s gas fee plus a variable bridge fee generally ranging from 0.1% to 0.5% of the transferred amount. Before confirming, compare the total received amount, not just the percentage fee, because gas and slippage can materially change the economics.

Does an HTLC make a cross-chain transfer risk-free?

No. An HTLC can coordinate conditional settlement and support an automatic return if the transfer does not complete before its deadline. It does not eliminate smart-contract vulnerabilities, price slippage, connected-network attacks, relay failures, or user mistakes such as selecting the wrong destination network.

Why might someone use cross-chain collateral?

Cross-chain collateral can let users lock an asset on one network while using it in lending or yield-farming activity on another. The benefit is greater capital flexibility. The limitation is that the system becomes dependent on accurate cross-chain accounting, reliable pricing, and the continued operation of both the bridge and the DeFi application.

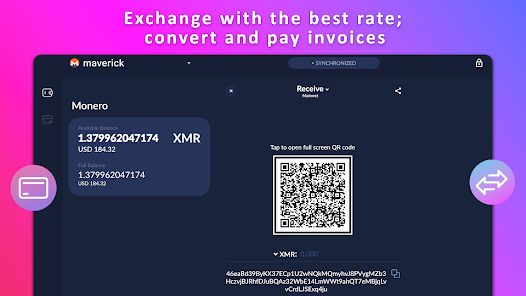
Mobile wallet interface illustrating multi-currency asset management and in-wallet exchange decisions

Mobile Crypto Wallet Exchange: What “Exchange in Wallet” Really Means

You are standing in a coffee shop in the United States, trying to pay with one cryptocurrency while the funds you hold are denominated in another. A mobile wallet offers an exchange button, quotes a rate, and appears to solve the problem in seconds. The temptation is to treat this as a simple convenience feature. It is not. A wallet exchange combines asset conversion, transaction signing, liquidity, privacy decisions, and third-party risk inside one small interface. If the conversion fails, the problem may be an unfavorable price, a delayed blockchain transaction, a service provider’s policy, or a compromised phone.

The central misconception is that “exchange in wallet” means the wallet itself has become a fully private exchange. Usually, the wallet remains the software that controls or helps control your keys, while a separate exchange service, liquidity provider, or swap mechanism handles the conversion. That distinction matters. Self-custody can reduce dependence on a centralized custodian, but it does not remove counterparty risk, network surveillance, market volatility, or operational mistakes. A secure mobile crypto wallet is therefore best understood as a control panel for several systems, not as a magic privacy shield.

Mobile wallet interface illustrating multi-currency asset management and in-wallet exchange decisions

How an in-wallet exchange actually works

When a user exchanges Bitcoin for Monero, or one supported asset for another, the application must obtain a price and route the trade. In a common design, the wallet requests a quote from an external provider, displays the expected amount, and asks the user to approve one or more blockchain transactions. The wallet may sign the transaction locally, but the quote, routing, settlement, and fee calculation can still depend on outside infrastructure.

That creates several distinct stages: price discovery, transaction construction, authorization, broadcast, settlement, and delivery of the destination asset. Each stage has a different failure mode. A quote can expire. Network fees can change. A transaction can remain pending. The provider can reject a transaction because of jurisdiction, compliance screening, liquidity, or asset support. The receiving wallet may ultimately show fewer coins than the initial estimate because the rate moved or fees were deducted.

This is why the displayed exchange rate should not be the only number a user examines. The economically relevant figure is the final amount received after service fees, network fees, spreads, and possible slippage. Slippage is the difference between the expected execution price and the price actually obtained. It tends to matter more in thinner markets or during abrupt price movements. A “fee-free” exchange may still be expensive if the spread is wide.

The phrase “mobile wallet exchange” also hides a custody question. If a service asks the user to deposit funds to an address controlled by the provider and later sends back the converted asset, the user is temporarily exposed to counterparty and settlement risk. If the swap is structured through transactions that remain under the user’s control until completion, the custody profile may be different, but it is not automatically risk-free. The user still has to verify addresses, understand the route, and protect the signing device.

Privacy is not a single setting

Monero and Bitcoin illustrate why multi-currency support requires more than a list of coin icons. Monero is designed to obscure important transaction relationships through protocol-level privacy features. Bitcoin transactions, by contrast, are publicly visible on a transparent ledger, even when identities are not written directly into the transaction. A Bitcoin wallet can improve privacy through careful address management and spending practices, but it cannot make the Bitcoin ledger operate like Monero’s.

An exchange between the two assets may create a privacy boundary rather than eliminate one. The provider may see the source asset, the destination address, timing information, device or account metadata, and the transaction path it manages. Even if the blockchain transaction itself reveals limited personal information, network-level signals and service records can create a meaningful profile. Privacy therefore depends on the protocol, the wallet’s architecture, the provider’s data practices, the user’s network environment, and what happens before and after the exchange.

A useful mental model is to separate three kinds of privacy. Ledger privacy concerns what observers can infer from blockchain data. Network privacy concerns information exposed when the device communicates with nodes, servers, or exchange providers. Behavioral privacy concerns patterns created by repeated address use, predictable amounts, timing, account registration, and links to regulated platforms. Improving one layer does not necessarily improve the others.

For Bitcoin users, address reuse is especially revealing because it makes transactions easier to connect. Generating a fresh receiving address is helpful, but it is not a complete solution if a user later consolidates funds, repeatedly uses the same exchange provider, or links transactions to a known identity. For Monero users, protocol-level protections do not excuse poor device security or careless disclosure of addresses and payment information. Privacy reduces certain forms of visibility; it does not protect a phone that is infected or a seed phrase that has been photographed.

Security begins outside the exchange button

The strongest protection offered by a non-custodial wallet is generally control of the signing key. That protection disappears in practice if the recovery phrase is stored in a cloud note, entered into an unfamiliar website, or shared with someone claiming to be support. A legitimate wallet does not need a user’s recovery phrase to “verify” a transaction. Anyone who obtains it may be able to recreate the wallet elsewhere and move the funds.

Mobile devices introduce a concentrated attack surface. Screen overlays, malicious applications, SIM-related account attacks, clipboard replacement, unsafe backups, rooted or jailbroken operating systems, and fake wallet downloads can all undermine an otherwise sound protocol. Biometric unlocking can make daily use safer and more convenient, but biometrics usually protect access to the device or application; they do not replace the recovery phrase as the underlying authority.

Transaction verification deserves particular attention. Before approving a transfer, compare the asset, network, destination address, amount, and fee. For an exchange, also inspect the quoted output, expiry period, refund or failure procedure, and whether the provider requires an additional deposit. A familiar logo is not evidence that the transaction is safe. Address poisoning and phishing work precisely because users confirm the appearance of an interface instead of the details of the transaction.

For larger balances, a separate signing device or hardware wallet can reduce exposure to a compromised phone, although it adds setup complexity and can make urgent transfers less convenient. A practical division is to keep limited spending funds on a mobile wallet and use stronger isolation for savings. The correct boundary depends on the amount at risk, the user’s ability to maintain backups, and how frequently the funds must move.

Readers evaluating a privacy-focused multi-currency wallet can review an explanation of a wallet download here, but a download page should never substitute for independent verification. Obtain software from a source you can authenticate, check that the application and update path are genuine, and create the recovery backup before depositing meaningful funds. If the backup cannot be restored in a controlled test, the wallet is not operationally reliable, regardless of its feature list.

Common myths and the more accurate version

Myth: An exchange inside a wallet is always safer than using an exchange website

Correction: it may reduce copying addresses between applications and may preserve self-custody for part of the process, but safety depends on the actual routing model. An embedded provider can still hold funds temporarily, collect metadata, impose restrictions, or expose the user to smart-contract or service risk. Fewer visible steps do not necessarily mean fewer technical steps.

Myth: Multi-currency support means every asset receives the same privacy protection

Correction: privacy properties belong primarily to the protocol and the surrounding transaction environment. A wallet can present Monero and Bitcoin beside each other, but it cannot transfer Monero’s ledger characteristics to Bitcoin. It can offer better address handling, local key control, or privacy-oriented network options, yet the underlying chain remains a decisive boundary.

Myth: A confirmed transaction proves the exchange succeeded

Correction: confirmation proves that a particular blockchain transaction was accepted according to that network’s rules. It does not prove that the destination service has credited the converted asset, that the quote was fair, or that the receiving address was correct. Exchange completion requires checking the destination balance and, where relevant, the provider’s settlement status.

Myth: Privacy means avoiding all records

Correction: privacy is better described as reducing unnecessary exposure and improving control over who can infer what. Users in the US may still encounter tax, accounting, or service-reporting obligations depending on the activity and applicable rules. Technical privacy and legal compliance are separate questions. A wallet can help limit casual blockchain surveillance without making obligations disappear.

A reusable decision framework

Before using an in-wallet exchange, ask five questions. Who controls the funds during the swap? Where does the quote come from? What information leaves the device? What happens if the transaction is delayed or rejected? Can the received asset be independently verified afterward? These questions are more useful than judging an application by the number of supported coins or the smoothness of its animation.

For routine spending, convenience may reasonably outweigh small price differences. For a privacy-sensitive conversion, the user may instead prioritize a provider’s data minimization, transparent fees, address control, and clear failure handling. For a large transaction, a small test transfer can reveal whether the route, destination, and settlement process behave as expected. The test does not eliminate risk, but it limits the cost of an incorrect assumption.

The most important forward-looking signal is not simply whether wallets add more assets. It is whether they make the invisible parts of exchange visible: custody transitions, quote sources, data sharing, fee composition, and settlement status. If interfaces expose those mechanics clearly, users can make informed trade-offs. If they hide them behind a single “swap” button, convenience may grow while understanding shrinks.

FAQ

Does an in-wallet exchange require me to give up custody?

Not necessarily. Some designs keep the user in control of keys while transactions are arranged through an external provider. Others require a temporary deposit or account-based settlement. Read the transaction flow and determine who controls the funds at each stage rather than relying on the wallet’s branding.

Is Monero automatically private when used in a mobile wallet?

No. Monero provides protocol-level privacy properties, but device compromise, address disclosure, network metadata, unsafe backups, and third-party exchange records can still expose information. Privacy is a system outcome, not a single switch.

What is the safest first step before exchanging Bitcoin or Monero?

Verify the software source, secure and test the recovery backup, review the complete quote, and send a small test amount when the transaction is significant. Confirm the destination asset and address on the device itself, not only in a copied message or web page.

A mobile wallet can make crypto exchange more accessible, but accessibility should not be confused with simplicity. The exchange button compresses a chain of economic and security decisions into one gesture. Users who unpack those decisions—custody, liquidity, privacy layers, verification, and recovery—are better positioned to use multi-currency tools without mistaking convenience for protection.

Rabby Wallet logo representing multi-chain DeFi portfolio management and transaction security

Why DeFi Portfolio Tracking, Security, and Gas Optimization Belong in the Same Wallet

The most expensive DeFi mistake is not always a high gas fee. Sometimes it is signing a transaction that looked routine, approving a contract that no longer needs access, or discovering that a profitable position is scattered across several chains and impossible to manage quickly. That is the counterintuitive lesson of multi-chain finance: portfolio visibility, transaction security, and gas management are not separate conveniences. They are parts of one risk system.

For a US-based DeFi user moving between Ethereum, Arbitrum, Optimism, Polygon, BNB Chain, or Avalanche, the wallet is more than a place to store tokens. It is the control surface through which capital enters protocols, changes networks, grants permissions, and pays execution costs. A wallet such as Rabby is designed around that reality. Its value is best understood not as a promise of perfect safety, but as an attempt to reduce the number of decisions a user must make blindly.

Rabby Wallet logo representing multi-chain DeFi portfolio management and transaction security

The first myth: a portfolio tracker is only a dashboard

Portfolio tracking sounds passive: display token balances, identify lending positions, and estimate the value of assets. In DeFi, however, a portfolio is not just a list of coins. It is a set of claims on smart contracts, liquidity pools, lending markets, vaults, bridges, and reward systems, often distributed across multiple networks. The important question is not merely “How much do I own?” but “What can change my ownership, and under which conditions?”

This distinction matters because a wallet connected to a DeFi portfolio platform can help users see exposure that would otherwise be fragmented. A user may hold the same stablecoin on several chains, have a token approval active on an old decentralized application, and retain a small amount of collateral in a lending protocol. Each item can look harmless in isolation. Together, they create an operational profile: more networks to monitor, more permissions to review, and more opportunities to spend gas inefficiently.

Rabby’s DeFi-oriented design links portfolio awareness with transaction review. Its automatic network switching can identify the chain required by a decentralized application, reducing one common source of friction: attempting to interact with the right application while the wallet is set to the wrong network. That does not make a protocol trustworthy, and it does not remove the need to verify the website and contract address. It simply reduces a layer of avoidable interface error.

Security is a decision process, not a warning label

A common misconception is that a wallet is “secure” because it blocks every dangerous transaction. No wallet can reliably eliminate every risk created by malicious code, compromised websites, social engineering, bad key management, or user confirmation. The more useful mental model is decision support. A secure workflow gives the user better information before an irreversible action and makes risky permissions easier to inspect afterward.

Rabby’s transaction simulation engine follows this logic. Before signing, it can show estimated balance changes and provide more detail about contract interactions. Its pre-transaction risk scanning can also flag potential concerns, such as interactions with previously hacked contracts or non-existent addresses. These features are particularly valuable because blockchain transactions are often opaque at the moment of signing: a button may say “confirm,” while the underlying call could transfer tokens, alter collateral, or grant a spending allowance.

Simulation is not proof of safety. It is an interpretation of what a transaction is expected to do under the simulated conditions. State can change between simulation and execution, contract behavior may depend on external data, and a legitimate-looking action can still expose a user to economic risks such as liquidation, slippage, or impermanent loss. The practical lesson is to treat simulation as a second set of eyes, not as a substitute for protocol research.

Approval management illustrates the same principle. A token approval allows a smart contract to spend tokens on a user’s behalf, sometimes up to a large or effectively unlimited amount. The approval itself is not a transfer, but it expands what the contract can do later. Rabby’s built-in revoke tool helps users cancel permissions associated with unused or suspicious decentralized applications. Revoking can reduce future exposure, although the action itself costs gas and does not recover assets already taken.

Gas optimization begins with reducing unnecessary actions

Gas is the network fee paid for computation and state changes. Its dollar cost depends on the chain’s fee market, the complexity of the transaction, and the market value of the native gas token. Many users approach gas optimization by searching for the cheapest chain. That is only part of the problem. A cheaper transaction can become expensive if it requires several bridge transfers, repeated approvals, failed attempts, or a rushed migration between networks.

A better framework separates three costs: the fee for executing an action, the cost of moving assets between chains, and the cost of operational complexity. The third category is easy to overlook. If a user forgets which chain holds the required asset, switches networks repeatedly, or cannot pay the native fee at the moment an opportunity appears, the resulting delay or failed transaction may matter more than a small difference in gas price.

Cross-chain Gas Top-Up addresses a practical version of this problem. It allows users to send gas fees across different chains so they can transact on a network where they do not yet hold its native gas token. This can be useful when funds are already positioned on a chain but the wallet lacks the small amount of ETH, MATIC, BNB, AVAX, or another native asset needed for execution. The feature improves access to liquidity already under the user’s control; it does not make the underlying transaction free, and the top-up process has its own execution and exchange considerations.

Gas optimization also requires knowing when not to transact. Consolidating small positions may improve portfolio simplicity but cost more in fees than the position is worth. Revoking every approval immediately may be sensible for a high-risk wallet, yet economically inefficient if the user will return to a trusted protocol and must approve again later. Batching actions, selecting a lower-cost execution window where the network supports meaningful fee variation, and avoiding unnecessary cross-chain movement can help—but the best choice depends on the user’s time horizon and risk tolerance.

Multi-chain support creates both reach and a larger attack surface

Rabby supports more than 140 EVM-compatible blockchains, including major networks such as Ethereum, BNB Chain, Arbitrum, Optimism, Polygon, and Avalanche. It also allows users to add unsupported EVM networks through custom RPC settings. This breadth can be useful for DeFi users who manage positions across different execution environments, but it introduces an important boundary condition: adding a network is not the same as validating it.

Custom RPCs require judgment about the endpoint, chain identity, token representations, explorer information, and applications deployed there. A familiar wallet interface can make an unfamiliar chain feel established when it may have a smaller developer community, thinner liquidity, or weaker operational history. Network support therefore expands choice, not certainty. Users should verify chain details independently and avoid treating automatic switching as an endorsement of every application that requests it.

There is also a compatibility limit. Rabby is focused on EVM-compatible networks and does not provide native support for non-EVM ecosystems such as Solana or Bitcoin. That makes it a coherent tool for an EVM-centered strategy, but not a universal wallet for every digital asset. It also does not include a built-in fiat on-ramp, so users who need direct card or bank funding may require a separate service and an additional transfer step.

Self-custody changes the meaning of convenience

In a non-custodial model, private keys are encrypted and stored locally on the user’s device rather than transmitted to backend servers. This reduces dependence on a centralized custodian, but it transfers responsibility to the owner. Device security, recovery phrases, phishing resistance, browser hygiene, and backup procedures remain decisive. Open-source architecture and security audits can improve transparency and scrutiny, yet they cannot guarantee that a particular installation, extension download, device, or user interaction is uncompromised.

For larger balances, separating daily activity from long-term custody is often more sensible than keeping everything in one hot wallet. Rabby integrates with hardware wallets including Ledger, Trezor, Keystone, and BitBox02, and it supports multi-signature management through Gnosis Safe. Hardware signing can keep key material isolated from the everyday browser environment, while multisignature arrangements require more than one authorized approval. Both approaches add friction. That friction is not a defect when the objective is to slow down high-impact mistakes, but it may be inconvenient for rapid, low-value transactions.

For readers evaluating the wallet’s workflow in detail, the product overview is available here. The useful question is not whether one interface is universally superior to another. It is whether the wallet’s review tools match the user’s actual behavior: number of chains, frequency of contract interactions, size of holdings, reliance on hardware signing, and tolerance for manual verification.

A reusable checklist for safer DeFi execution

Before signing, first identify the intended outcome: which asset should leave, which asset should arrive, and on which chain. Next, inspect the simulation for unexpected balance changes or contract calls. Then check the application domain and contract identity rather than relying solely on a familiar logo. After execution, review approvals periodically and consider whether the position still justifies the fees and permissions required to maintain it.

For gas decisions, compare the full route rather than a single fee quote. Ask whether a bridge, approval, swap, and deposit are all necessary; whether the position can remain where it is; whether a small gas top-up avoids a larger and more complicated transfer; and whether the expected benefit exceeds the transaction cost. This framework is more durable than memorizing which chain is “cheapest,” because fee markets and protocol conditions change.

The next meaningful development in wallet design is likely to be better coordination between visibility and execution. If portfolio data, simulations, approval records, and cross-chain fee management become more tightly connected, users may be able to evaluate not just a transaction’s immediate result but its effect on total portfolio risk and operating cost. That outcome is conditional, however. It depends on accurate data, clear explanations, reliable chain integrations, and users who understand the limits of automated warnings.

Frequently Asked Questions

Does transaction simulation guarantee that a DeFi transaction is safe?

No. Simulation can clarify expected balance changes and contract interactions, and risk scanning can identify known warning signs. It cannot guarantee that the protocol is economically sound, that the website is genuine, or that conditions will remain unchanged between simulation and execution. Users should combine simulation with contract, domain, slippage, and protocol checks.

Can cross-chain gas top-up eliminate network fees?

No. It helps provide the native gas token needed to transact on another supported chain when the user does not already hold it there. The top-up operation and the eventual transaction still involve costs, and the most efficient route depends on the assets, networks, and timing involved.

Is a multi-chain wallet suitable for Bitcoin or Solana assets?

Not necessarily. Rabby is focused on EVM-compatible networks, so it is well suited to an EVM-centered DeFi portfolio but does not natively support non-EVM networks such as Bitcoin or Solana. Users with broad cross-ecosystem holdings may need separate wallet infrastructure.

The sharper conclusion is that portfolio tracking, security, and gas optimization all address the same underlying problem: making informed state changes across systems that are fast, fragmented, and difficult to reverse. A capable wallet can reduce blind spots and unnecessary friction. It cannot replace verification, sound key custody, or economic judgment. In DeFi, that distinction is not a footnote; it is the foundation of responsible execution.

Rabby wallet logo; emphasizes features like transaction simulation, MEV protection, cross-chain gas top-up and hardware wallet integration relevant to advanced DeFi users.

Why transaction simulation and MEV-aware wallets matter for yield farmers — a practical comparison for advanced DeFi users

Surprising fact: many profitable yield-farming opportunities collapse not because the strategy was wrong, but because a blind signature or a failed gas estimate handed the trade to an MEV bot or left the user with stuck funds. In plain terms, a single poorly previewed contract call can turn a 20% APY into a loss after front-running, sandwiching, or revert gas costs. That reality reframes the wallet choice from “convenience” to “active risk-management”—and it’s why tools that simulate transactions and scan for contract-level risks have moved from optional niceties into operational necessities for US-based DeFi practitioners.

This article compares three practical approaches to smart contract interaction for yield farming and WalletConnect-style dApp access: (A) a baseline wallet without transaction simulation, (B) a wallet that simulates and scans transactions before signing, and (C) the same simulation-plus-protection wallet augmented by hardware multisig and gas-top-up capabilities. For each, I’ll explain mechanisms, trade-offs, where they break, and what to watch next—so you can pick the tool that fits your capital, behavior, and threat model.

Rabby wallet logo; emphasizes features like transaction simulation, MEV protection, cross-chain gas top-up and hardware wallet integration relevant to advanced DeFi users.

Core mechanics: how simulation and pre-sign checks change the signing decision

Mechanism first: a “blind” wallet hands you the raw transaction data and asks you to sign. You must infer, from token amounts and the dApp UI, what the chain will do. A transaction-simulating wallet executes a dry-run of the transaction logic against a node or local trace engine and reports expected balance changes, internal contract calls, and gas estimates before you sign. That extra step converts uncertainty into structured information: you move from guessing “does this contract swap tokens correctly?” to seeing a modeled outcome, which is crucial for complex composable flows like multi-hop swaps or auto-compounding vault deposits.

Why it matters for yield farming: vault strategies, auto-compounders, and aggregator routings bundle multiple contract calls. A revert in the middle can still consume gas; a mispriced approval can allow an allowance drain, and an optimizer’s routing can route through low-liquidity pools that suffer slippage or impermanent loss. Simulation surfaces these failure modes and quantifies expected token deltas; pre-transaction risk scanning can flag interaction with an address linked to a past exploit or a contract lacking source verification, adding a second independent check.

Side-by-side: three wallet patterns and who they fit

Below I compare the three patterns with focus on yield farming + WalletConnect dApp use. Each column lists the mechanism, primary benefit, main trade-offs, and failure modes.

Option A — Baseline wallet (no simulation)

Mechanism: standard RPC flow; user approves transactions produced by dApps, often via WalletConnect or injected provider. Benefit: simplest UX, widest app compatibility. Trade-offs: higher exposure to blind-signing mistakes, inability to surface internal calls or simulate gas under varying chain conditions. Failure modes: front-running, sandwich attacks, approve-malware, unexpected reverts consuming gas.

Option B — Simulation + pre-transaction scanning (single-signer)

Mechanism: before signing, the wallet runs a simulated execution and a risk scan that cross-references warnings (e.g., previously exploited contract, suspicious bytecode, or zero-address interactions). Benefit: materially reduces blind-sign risk; shows token balance deltas, possible internal transfers, and realistic gas use. Trade-offs: slightly longer sign flow, dependence on accurate simulation nodes and heuristics; false positives and false negatives are both possible. Failure modes: simulation depends on a recent state snapshot—if mempool conditions change (very fast markets), real execution can still be MEV-targeted; scanning may miss novel attack vectors.

Option C — Simulation + pre-scan + multisig/hardware + cross-chain gas tools

Mechanism: combines Option B protections with multi-signature workflows (via Gnosis Safe integration), native hardware wallet support (Ledger, Trezor, Keystone, BitBox02), and tools to top-up gas across EVM chains. Benefit: best-fit for capital at scale or institutional workflows—defence in depth: simulated transparency, human review across co-signers, and cold-key signing for high-value operations. Trade-offs: more operational friction, coordination overhead for multisig, and potential delays in fast-execution arbitrage-style yield ops. Failure modes: multisig reduces single-key compromise but can slow timely exits; lack of non-EVM support prevents access to certain cross-chain yield opportunities.

How WalletConnect changes the picture and why simulation matters there too

WalletConnect is the common bridge between mobile wallets and dApp front-ends. It standardizes message passing and signing but does not solve blind-signing risk by itself. When you pair a wallet over WalletConnect, the wallet still receives transaction payloads from the dApp; if it lacks a simulation engine, you’re back to Option A behavior. A wallet that combines WalletConnect compatibility with pre-sign simulation converts that channel into a safer conduit: the mobile-based user sees the same modeled outcomes they would on desktop, which matters because many yield ops begin on one device and finish on another.

In practice, that means your evaluation of a wallet for yield farming must weigh three properties: simulation fidelity (how closely the dry-run matches real chain behavior), timeliness (how fast the simulation runs relative to mempool volatility), and integration (does the wallet support hardware keys and multisig when you need them?).

Practical trade-offs: speed, security, and composability

Trade-off 1 — Speed vs. safety: high-frequency strategies (arbitrageors chasing millisecond spreads) will favor low-latency signing and may accept blind-sign risk with automated monitoring. Most retail and even many professional yield farmers trade far less frequently and benefit from a small delay to get a simulation and a risk scan. Decide by expected reaction time: if you need to exit within seconds for a strategy to work, a multisig will be too slow; if you operate weekly rebalance cycles, safety-first choices dominate.

Trade-off 2 — Composability vs. permission control: smart contract approvals enable composability but increase attack surface. Tools that show approvals and offer revocation are vital. Active approval management—revoking allowances to contracts you no longer use—reduces long-tail risk from compromised dApps but adds cognitive load; consider automation or a policy (e.g., revoke after 30 days of inactivity for non-core approvals).

Trade-off 3 — Breadth of chain support vs. specialization: wallets focused on EVMs (over 140 supported chains in some wallets) give you the largest DeFi universe today, but they exclude non-EVM rails like Solana or Bitcoin. If your strategies depend on cross-paradigm yields, you’ll need multiple custody solutions and bridge-aware risk practices.

Non-obvious insights and one sharper mental model

Insight: think of transaction simulation like an “expectation operator” in statistics. It doesn’t guarantee the realized outcome, but it reduces variance in decision-making by giving you an expected delta and a set of conditional flags. That’s different from “security” in the binary sense—simulation reduces informational asymmetry between you and market adversaries, but it cannot prevent MEV that exploits real-time mempool order. The right heuristic: prefer simulation when your strategy benefits from reducing execution uncertainty, but combine it with ordering protections (e.g., private relays, MEV-resistant RPCs) if front-running materially changes profitability.

Corrected misconception: simulation is not a magic bullet that prevents all losses. It’s a decision-support tool. It tells you what a canonical node expects to happen given current chain state. If you rely on that as an oracle for market timing during volatile windows, you may be surprised. Always ask: how stale is the state snapshot the simulator uses? Was the run performed via a public RPC that sees the whole mempool, or a private trace that cannot model adversarial ordering?

Where these tools break—limitations and operational failure modes

Limitations to watch:

– EVM-only scope: wallets that commit to EVM chains give broad DeFi access but will not help if an opportunity or risk sits on non-EVM rails. – Local private key storage is safer from server-side compromise but vulnerable to device compromise and phishing. Hardware wallets mitigate this but add UX friction. – Open-source wallets under MIT encourage community review, but that does not equal formal security guarantees; audits and responsible disclosure matter. – Gas-top-up tools solve a friction point on unfamiliar chains but create a tiny attack surface (cross-chain messaging).

Operational failure cases: a simulation that reports successful token deltas but the real transaction reverts due to changed pool liquidity; a multisig flow where a co-signer delays approval and the opportunity vanishes; a risk scanner that misses a novel flash-loan-based exploit. These are not hypothetical—they are observed trade-offs in active DeFi markets.

Decision heuristics and a short checklist for yield farmers

Heuristic 1: If your wallet holds >$10k in active yield positions, prioritize simulation + pre-scan + hardware signing. Heuristic 2: If you depend on sub-minute execution, accept lighter protection but pair it with private order relays or bots under your control. Heuristic 3: Always revoke excessive approvals; use built-in revoke tools or on-chain revocation transactions as part of weekly hygiene.

Checklist before executing a smart-contract yield operation:

1) Run a simulation and read the token balance deltas. 2) Check the pre-transaction risk scan for flagged addresses or missing source code. 3) Confirm approvals are minimal and revoke unnecessary allowances. 4) For large amounts, route the action through multisig with hardware keys. 5) If you lack gas on the target chain, use a gas top-up tool rather than emergency bridging at peak costs.

What to watch next (signals, not guarantees)

Watch for two connected signals: improvements in public RPCs that offer MEV-resistant ordering and broader adoption of transaction simulation as a UX baseline for mainstream wallets. If more wallets integrate multisig, hardware support, and gas-top-up natively, the barrier to safer yield farming will drop. Conversely, increasing sophistication of mempool-based MEV strategies means simulation tools must evolve to include adversarial-ordering scenarios to remain decision-useful. Recent product positioning emphasizes Rabby as a strong candidate in this space—if you want to test a wallet that combines simulation, approval revocation, Gnosis Safe integration, hardware wallet connectors and cross-chain gas top-up, start exploring it here.

FAQ

Q: Does transaction simulation prevent MEV?

A: No. Simulation reduces informational asymmetry by showing an expected outcome given current chain state, but it cannot prevent adversarial ordering in the mempool. For MEV-sensitive trades, combine simulation with private relays, limit orders, or specialized execution services that provide MEV-resistant ordering.

Q: How reliable are pre-transaction risk scanners at catching exploitable contracts?

A: They are useful but imperfect. Scanners flag known bad actors or suspicious patterns (missing source, previously exploited addresses), which helps avoid repeat offenders. They can miss zero-day or orchestrated attacks. Treat scanner output as a risk signal, not absolute proof of safety, and combine it with manual review for large exposures.

Q: Should I always use multisig for yield farming?

A: Multisig is excellent for protecting large, slow-moving positions and institutional capital because it reduces single-key risk. It is less suitable for high-frequency strategies that require rapid unilateral action. Consider a hybrid model: single-signer hot wallets for tactical positions and multisig for core treasury or long-term vault deposits.

Q: What’s the main operational overhead of simulation-enabled wallets?

A: Slightly longer signing flows and the need to interpret simulation output. There can also be occasional false-positive warnings that require judgment. The trade-off is usually worthwhile if you value reduced surprise risk and clearer approval management.